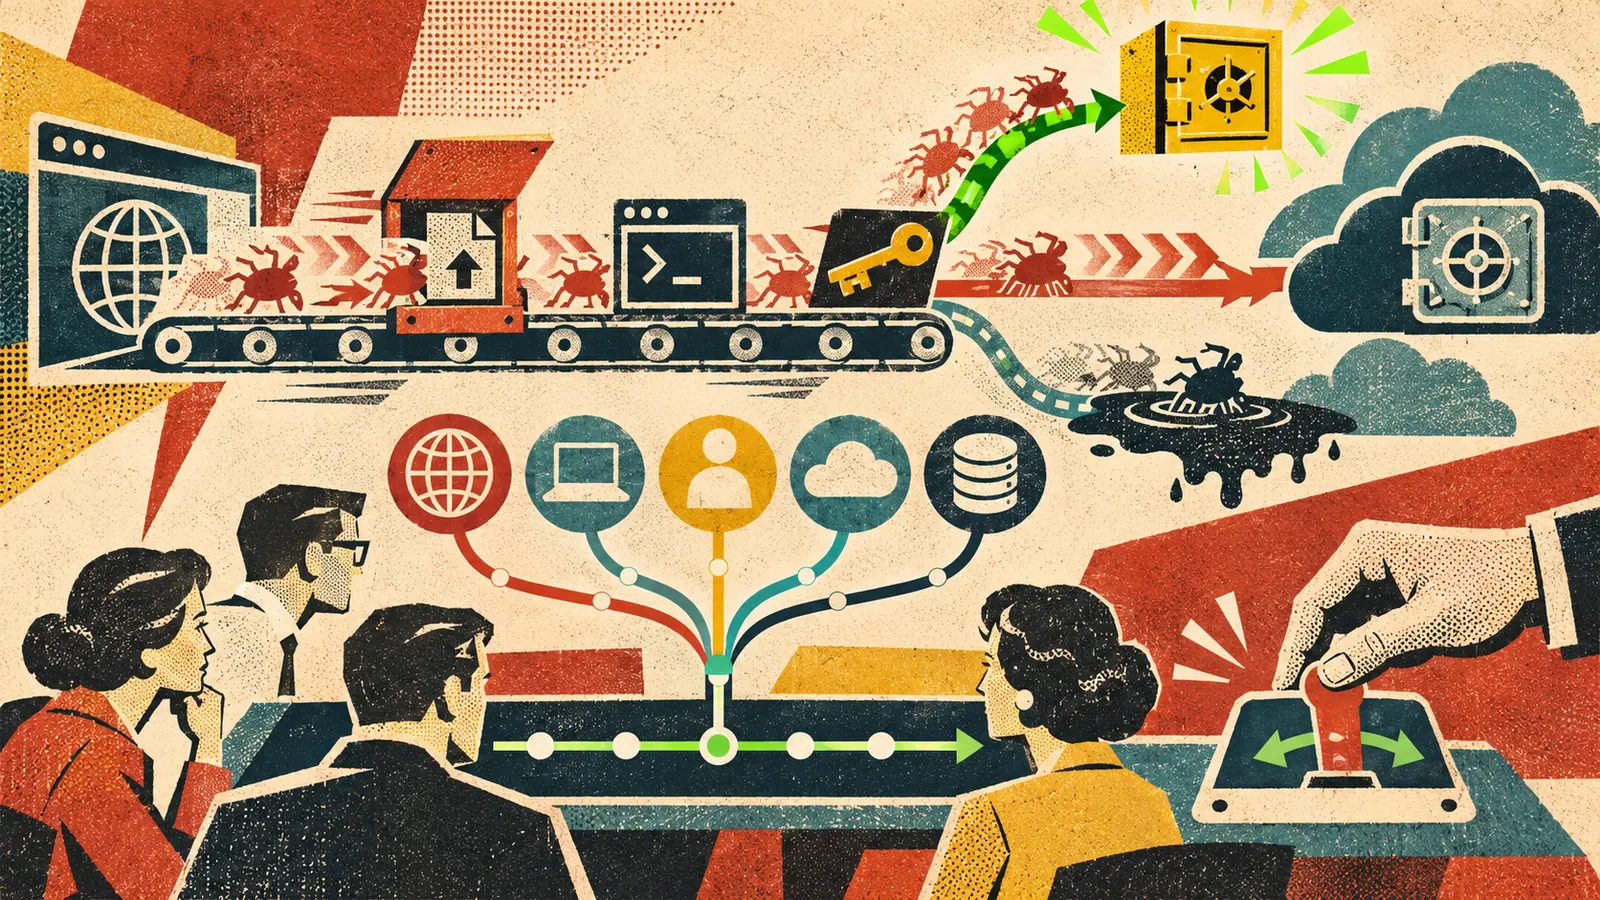
THE SIGNAL IN ONE SENTENCE
The worrying thing about an AI-assisted cyberattack is not that the model invents a brand-new species of crime. It is that the old crimes stop taking coffee breaks. Microsoft Threat Intelligence reported on November 6 that Storm-3358, a financially motivated intrusion cluster it places in Cambodia, used the agentic offensive security framework ARTEX against financial organizations during October. Microsoft says the cluster primarily targets Southeast Asia, with a smaller number of large financial organizations elsewhere. The reported chain is familiar. Scan public systems. Find weak web applications. Exploit anonymous file upload or server-side request forgery. Install remote-access tools. Steal or obtain credentials. Use compromised cloud identities. Move sideways. Keep access. Take data. ARTEX did not perform this alone. Microsoft says the actor combined it with conventional automation and existing tools. The agents used utilities such as curl and netcat, and the attackers deployed WISP, vshell and AdaptixC2 remote-access tools. Web shells, credential abuse and cloud persistence remained part of the job. That is the useful signal. Stop treating the model name as the incident. The incident is the sequence. An agent can try many requests quickly, retry a technique with small variations and jump into the next phase as soon as something works. If the security team watches each product in isolation, the activity may look like a noisy scanner over here, a strange upload over there, a new process on one server and an odd cloud sign-in five minutes later. The attacker experiences one continuous campaign. The defender experiences four unrelated tickets. Fix that mismatch. Join web, endpoint, identity, cloud and data events into one timeline. Detect behavior that changes phase quickly, not only a known IP address or user-agent string. Place decoys where automated exploration will find them. Use tarpits to consume the attacker's time and tool budget. Make stolen credentials narrow, short-lived and difficult to reuse. Keep an external stop path for public services and cloud identities. Preserve evidence fast enough that containment does not erase the story. Microsoft publishes indicators for this activity, and defenders should use them. Microsoft also warns that attackers rotate proxies and VPNs. An address can be useful on Sunday and stale by lunch. Behavior lasts longer. Rapid scanning followed by several exploit variations, a web-shell action, a command-line download, a new persistence mechanism, a risky cloud sign-in and unusual data access is a chain worth stopping even when none of the tools says ARTEX on the box. The machine-speed defender is not necessarily another autonomous agent with permission to unplug the bank. It is a system that correlates evidence quickly, slows suspicious automation and gives a human a clean decision before the fifth alert becomes an exfiltration report. Attackers have shortened the chain. Defenders need to shorten the handoff.
01
WHAT ACTUALLY CHANGED
Microsoft linked a new financially motivated campaign to ARTEX use. The company says Storm-3358 began targeting financial-sector organizations with ARTEX in October 2026. Microsoft describes the cluster as Cambodia-based and primarily focused on financial organizations in Southeast Asia, plus a smaller number of large financial organizations globally. Storm names are Microsoft tracking labels. They organize observed activity and attribution assessments. They are not a court finding or a complete public identity for every person involved.
The reported activity spans the attack chain instead of stopping at scanning. Microsoft observed ARTEX used with conventional automated tools to scan public systems and exploit anonymous file upload and server-side request forgery weaknesses. The actor installed WISP, vshell and AdaptixC2 remote-access tools for persistence and lateral movement. Microsoft also reports web-shell use, credential compromise, compromised cloud identities, brute-force attempts, password spraying, API enumeration and database dumping among ARTEX capabilities or observed related behavior. Each technique existed before agentic AI. The change is how quickly a system can choose, retry and connect them.
The public report emphasizes behavior over a single signature. Microsoft says agentic frameworks tend to send a wide range of requests in a short period, retry variations on one technique and move to a later stage at machine speed. ARTEX can use common tools and browser automation, including Nmap, curl, wget, Python HTTP clients and headless Chromium through Playwright. Some traffic may expose default user-agent strings. Microsoft cautions that blocking those strings will not stop an agent that can quickly change them. The string is a clue. The sequence is the stronger signal.
Microsoft recommends active deception alongside conventional detection and response. The report points to honeypots, decoys, tarpits and fake wins. A decoy gives an automated attacker an attractive but worthless object. A tarpit consumes time and budget. A fake win presents evidence that the objective has already been achieved. Microsoft says these controls reduced attack traffic reaching real assets in its tests and produced high-confidence signals useful for attribution. That is a Microsoft-reported test result, not a universal guarantee. Deception has to be isolated, monitored and designed so it cannot become another route into production.
02
WHY THIS MATTERS
Financial organizations already operate under severe time pressure during an intrusion. Public services, payment systems, customer identities, employee accounts, cloud applications and third-party connections create many possible paths. An agent that can try those paths continuously makes fragmented ownership expensive. The web team cannot close its ticket while the identity team is still discovering that the same campaign reached the cloud.
Static indicators age faster when the attacker can reconfigure cheaply. IP addresses, domains, file hashes and user-agent strings are valuable for immediate hunting. They are also easy to rotate or imitate. Defenders need rules for durable behaviors such as rapid technique variation, unusual tool sequences, service processes launching shells, new application credentials, impossible privilege changes and high-volume access after a suspicious sign-in.
Valid credentials can make malicious activity look annoyingly ordinary. Once an attacker obtains a password, token or cloud application identity, requests may pass basic authentication. The useful question changes from did this identity authenticate to what did it do next. Join sign-ins with role changes, application credential additions, Graph or API calls, mailbox or storage access and outbound data movement.
Deception can create the pause that automation removes. An agent is good at exploring. That curiosity can be turned into a sensor. Decoy credentials, fake services and canary data can produce a signal with little legitimate ambiguity. Tarpits can slow repeated requests and burn the attacker's budget. The goal is not a cartoon trapdoor. It is a safe detour that buys responders time and evidence.
The defense should not become an unsupervised counterattack. Automated correlation, enrichment, containment suggestions and pre-approved rate limits can help. Retaliatory access, destructive action or broad identity revocation can create legal, operational and safety problems. Put humans on decisions that affect customers, money movement, core services or evidence, and make emergency actions reversible whenever possible.
03
WHERE IT COULD HELP
- Build one campaign timeline. Correlate web requests, application logs, endpoint processes, DNS, proxy events, identity sign-ins, cloud control-plane changes and data access with shared entity and time fields.
- Detect phase changes. Alert when scanning is followed quickly by upload, server-side request forgery, shell execution, tool download, persistence, credential use or cloud access, even when each event alone falls below a threshold.
- Plant high-confidence decoys. Create monitored credentials, services, shares and records that legitimate workflows never touch. Route any interaction into a fast human review and containment path.
- Use tarpits carefully. Slow suspicious enumeration and repeated exploit variations at the edge without delaying real customers or revealing production details. Measure whether the delay actually creates response time.
- Shorten credential life. Prefer phishing-resistant authentication, narrowly scoped service identities, short-lived tokens and conditional access. Make application credentials visible, owned and easy to revoke.
- Watch cloud activity after authentication. Correlate service-principal and user sign-ins with new credentials, role assignments, consent grants, API enumeration, mailbox or file access and unusual resource volume.
- Preserve before removing. Capture configuration, identity, process, network and cloud evidence before deleting malicious applications or credentials when urgent risk allows. Do not delay containment while waiting for a perfect export.
- Pre-authorize reversible controls. Define who can isolate a host, disable an integration, block an identity, restrict egress or rate-limit an endpoint, plus the evidence threshold and rollback process for each action.
- Hunt beyond published indicators. Use current IPs, domains and tool artifacts as pivots, then expand to the associated behaviors, time ranges, identities and adjacent systems. Assume infrastructure can change.
- Replay the chain. After containment, reconstruct the campaign from first contact through persistence and data access. Turn every missed handoff into a detection, ownership or evidence improvement and test it in the next exercise.
KEEP A HAND ON THE WHEEL
Microsoft is the primary source for the attribution, victim observations, tool use and defensive test claims in this article. The company bases its report on telemetry and threat intelligence available to it. The public post does not provide a complete victim list, complete forensic record or independent confirmation for every affected organization. Storm-3358 is a Microsoft tracking name for a cluster of activity. Cambodia-based is an attribution assessment, not a claim that Cambodia, Cambodian institutions or people generally are responsible. Public reporting should not convert a technical cluster label into a national accusation. ARTEX was one component in a broader attack chain. Microsoft says the actor combined it with conventional automation, public tools, remote-access software, compromised credentials and cloud identities. Blocking the ARTEX name, a default user-agent string or one server address will not remove the underlying weaknesses. The report contains indicators that were active or observed in late October and early November 2026. Indicators age. Validate them against current intelligence, preserve historical matches and avoid treating their absence as proof that an environment is clean. Deception controls need their own safety review. A decoy should not contain real secrets, expose customer data, create a bridge into production or generate so much noise that responders ignore it. A fake win should divert an intruder without causing an automated defender to declare the real environment safe. Automated defensive action can also fail at machine speed. Rate limits can block customers. broad identity revocation can interrupt critical operations, and a containment script can erase volatile evidence. Keep high-impact actions scoped, observable, reversible and under named human authority.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on November 8, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US