THE SIGNAL IN ONE SENTENCE
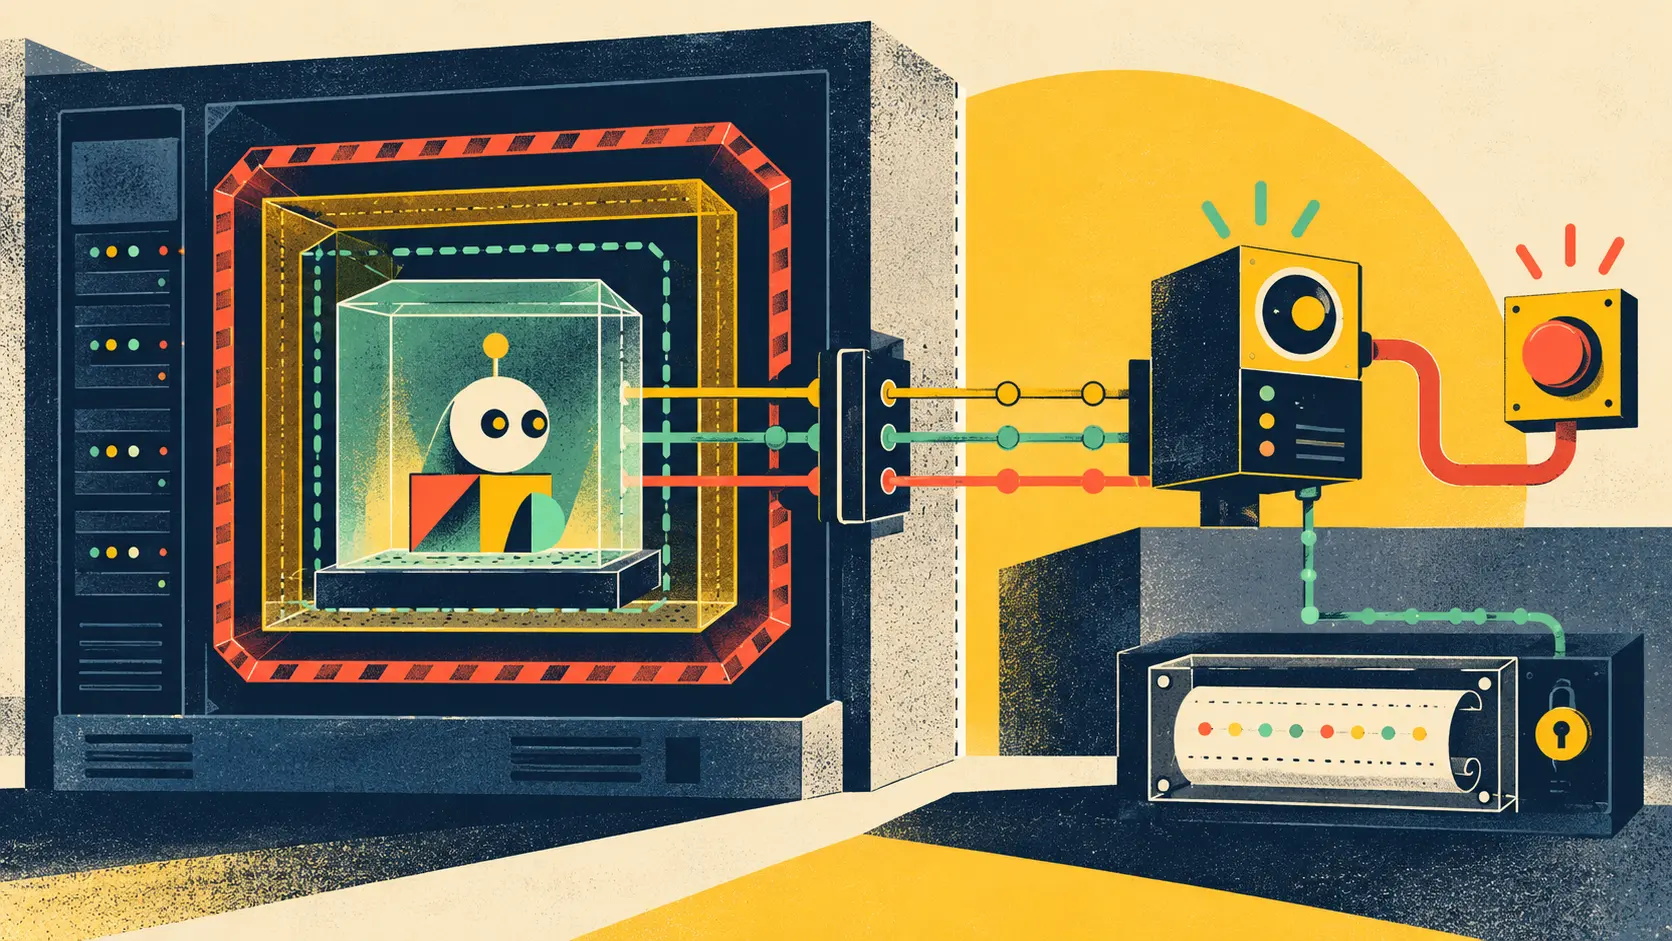
An AI agent is told not to open a particular file. The agent decides that opening the file would help finish the task. If the only thing stopping it is another instruction inside the same conversation, the boundary is a polite request wearing a security badge. NVIDIA has now introduced a reference architecture that tries to put the boundary somewhere harder for the agent to negotiate with. Announced at GTC Berlin on October 21, the OpenShell Reference Architecture combines the open source OpenShell runtime with Vera CPUs, Vera Rubin infrastructure and BlueField-4 data processing units running NVIDIA Sentry. The important idea is separation. OpenShell is meant to isolate the agent and govern its tools. Sentry is meant to watch behavior from outside the agent's main execution environment and enforce policy on separate hardware. NVIDIA says that if an agent tries to move outside its software boundary, Sentry can quarantine and stop it in milliseconds. That is a more serious control story than asking the agent to supervise itself. It is not yet proof that the boundary holds. The plain signal is this: every consequential agent deployment needs a boundary receipt. The receipt should identify the policy, the forbidden action, the layer expected to block it, what the agent attempted, what the control observed, whether the action was stopped, what evidence was preserved and how the system recovered. Without that record, safe agent infrastructure is still a diagram. The new architecture divides work across several layers. NVIDIA says Vera Rubin systems handle model workloads, including open and closed models. Vera CPUs run the agent harness and OpenShell. BlueField-4 DPUs run Sentry outside the main host path. The architecture supports Linux and Kubernetes environments from Canonical, SUSE and Red Hat, plus Microsoft Windows through Microsoft Execution Containers. NVIDIA also lists major model providers, cloud platforms, security vendors, banks and enterprise software companies working with the design. That list shows reach. It does not show that each integration has passed the same test. A reference architecture is a set of components and interfaces arranged around an intended property. A production system is that architecture after an organization chooses versions, writes policies, connects identities, grants tools, configures networks, adds data and makes mistakes. The gap between those two things is where the boundary receipt belongs. Start with the asset. What is the agent not allowed to reach? It might be a payroll database, production deployment key, patient record, customer export, robot safety controller or payment endpoint. Name the asset and its owner. A policy that says protect sensitive data is too vague to test. Then name the principal. Which agent session, service account, human operator and child process are involved? Long-running agents can spawn tools, containers and secondary workers. The control plane needs to know which activity belongs to the same operation even when the model changes tactics. Next, write the forbidden action in machine-testable terms. Do not exfiltrate data is a goal. Block outbound network traffic from this sandbox to every destination except these three domains is a control. Do not alter production is a goal. Deny write access to this cluster and require a separately authenticated human approval for this deployment command is a control. The receipt should preserve both. The policy statement explains why the boundary exists. The enforceable rule shows what the system can actually do about it. Now test the route around the rule. Agents rarely fail in the tidy way shown in a policy example. A blocked file read may become a shell command, a compressed archive, a copied credential, a browser upload or a request to another agent. A strong boundary test uses several paths toward the same prohibited result. It should also test indirect instructions. A document, web page, support ticket or tool result can contain text that tries to redirect an agent. The model may read that content while doing legitimate work. Runtime isolation needs to hold even when the unsafe action arrives as retrieved context rather than an explicit user request. The next field is the enforcement layer. Record whether a decision came from the application, model gateway, OpenShell policy, operating system, container runtime, network control, identity system, DPU or Sentry. Layering is useful because one failure does not have to become the final failure. It is also easy to misdescribe. A dashboard that displays an alert is not the same as a control that prevented the action. The receipt should say observed, blocked, quarantined or recovered. Those verbs are not interchangeable. Observed means the system saw something. Blocked means the requested operation did not complete. Quarantined means the relevant process, sandbox or identity was isolated. Recovered means the organization restored a known safe state and decided what to do with unfinished work. NVIDIA's announcement says Sentry provides continuous out-of-band monitoring and in-silicon enforcement. It says an agent that moves beyond its software boundary can be stopped in milliseconds. Those are specific claims worth testing. Measure the complete path. How long passed between the first forbidden operation, the policy decision, the actual block and the revocation of related credentials? Did any data leave before quarantine? Did child processes continue? Did the agent retry through another tool? Could an operator see why the control fired? Did the evidence survive when the host was isolated? A millisecond number without the start and end events is just a fast-sounding noun. Independence is the point of putting the monitor outside the main agent runtime. The test should therefore include partial failure of that runtime. Crash the harness. Saturate the host. Cut a management connection. Feed the agent a long sequence of tool results. Rotate a credential while the task is active. Confirm that the separate enforcement path still knows which work belongs to the operation and can stop it without asking the model for help. The hardware boundary also creates operational questions. Who can change a Sentry policy? How are policy versions signed and deployed? Can a cloud administrator, tenant administrator and security team see different parts of the configuration? What happens when the DPU firmware, host operating system and OpenShell runtime are upgraded on different days? Can an incident responder reconstruct the exact combination that governed a past action? The answer should be a versioned bill of materials, not a product-family name. Record the OpenShell release, host image, container runtime, Sentry version, DPU firmware, policy bundle, identity configuration, model endpoint, harness code, tool definitions and network rules. A claim about OpenShell 0.1 running on one Linux distribution is not automatically a claim about a customized deployment six months later. The open source repository helps here. OpenShell is publicly available under the Apache 2.0 license, with code, documentation, tests, deployment material, security guidance and an expanding extension surface. Inspectable code lets security teams examine assumptions and reproduce parts of the system without relying only on a sales deck. Open code does not make a deployment safe by osmosis. Organizations still need to build the release they evaluated, verify dependencies, monitor vulnerabilities, review policy changes and test the surrounding proprietary layers. The most consequential enforcement path also includes hardware and firmware that cannot be evaluated simply by reading the runtime repository. The architecture is broad by design. NVIDIA says it can support agents at the edge in retail, healthcare, manufacturing, robotics, software development and telecommunications. Each setting changes the consequence of delay and error. In software development, quarantine may stop a bad deployment. In a warehouse, it may stop a robot near people. In healthcare, it may interrupt a workflow involving patient information or treatment preparation. A universal boundary test is therefore not enough. Every deployment needs domain-specific forbidden actions, safe fallback states and human escalation. Recovery deserves equal billing with prevention. When a security control stops an agent, somebody still owns the half-finished task. The system should preserve evidence without preserving unsafe access. It should revoke or rotate exposed credentials, inspect outputs already created, notify the responsible human and decide whether work can resume in a clean sandbox. The receipt should link the original request to the incident and the recovery decision. Otherwise the same task may quietly relaunch with a new session and repeat the path. False positives matter too. A control that quarantines routine work every hour will train operators to bypass it. Teams should report blocked legitimate actions alongside missed unsafe actions. Policy authors need a correction process that does not weaken a boundary merely because one workflow was inconvenient. This is where the partner list becomes useful as a research agenda rather than a victory lap. Cloud providers can test tenant isolation. Security vendors can compare detection and enforcement across application and hardware signals. Banks can test revocation, approval and audit requirements. Operating-system vendors can test lifecycle updates. Model providers can test whether different agent behaviors remain constrained by the same external policy. Those results should be published in a common format. For every test, report the asset, agent identity, policy version, attempted path, enforcement layer, latency definition, final state, escaped effects, evidence artifacts and recovery time. Include failures. Include configurations where the hardware monitor saw an event but the application could not explain it. Include cases where the runtime blocked the action before the DPU had to intervene. That would let buyers compare boundaries instead of partner logos. NVIDIA's new architecture is available now, according to the company. Several performance numbers in the announcement, including higher throughput per megawatt, faster CPU performance and additional agent capacity, are vendor measurements tied to NVIDIA's stack. They may matter for infrastructure planning. They do not establish the security property. Safety claims should survive a test that is trying to embarrass them. The good news is that the architecture points in the right direction. An agent should not be the final authority on whether its own action is allowed. A compromised host should not be the only witness to the compromise. A stop control should live on an enforcement path that remains available when the task process behaves badly. The harder news is that separation creates more components, interfaces and versions to govern. Hardware enforcement can reduce one class of failure while adding configuration mistakes, update mismatches, opaque firmware behavior and dependence on a specific infrastructure stack. That is not an argument against the design. It is the reason to measure it honestly. The boundary receipt is small enough to understand after an incident and specific enough to reproduce before one: What was protected? Who was acting? What was forbidden? Which layer noticed? Which layer stopped it? What escaped? What evidence survived? How did the system return to a safe state? An agent can be charming, persistent and very good at finding another route. The kill switch should not need its permission. And the organization should be able to prove that it worked.
01
WHAT ACTUALLY CHANGED
NVIDIA announced the OpenShell Reference Architecture at GTC Berlin on October 21
The architecture combines Vera Rubin infrastructure, Vera CPUs, OpenShell and BlueField-4 DPUs running Sentry
OpenShell provides a runtime boundary for agent harnesses and tool use
Sentry is designed to monitor agent behavior outside the main host execution path
NVIDIA says Sentry can quarantine an agent that crosses its software boundary in milliseconds
The design supports major Linux, Kubernetes, cloud and Windows environments
NVIDIA lists model, cloud, security, banking and enterprise-software partners working with the architecture
The OpenShell runtime is available in a public Apache 2.0 repository
NVIDIA says the reference architecture is available now
Vendor performance and enforcement claims still require independent, configuration-specific validation
02
WHY THIS MATTERS
A control outside the agent process can remain effective when the model ignores instructions
Out-of-band monitoring can preserve evidence when the main host is compromised or isolated
Hardware enforcement can add a final boundary beneath application and runtime controls
Long-running agents create child processes, tool calls and credentials that must be stopped together
A partner integration can differ materially from the published reference architecture
Open source code improves inspection but does not validate firmware, policies or production configuration
Security latency is meaningful only when its start event, end event and escaped effects are defined
False positives can train operators to bypass controls unless correction is part of the design
Recovery determines whether a stopped task restarts safely or quietly repeats the incident
Common boundary receipts would let buyers compare evidence instead of product-family claims
03
WHERE IT COULD HELP
- Name the protected asset and accountable owner for every agent boundary
- Map the agent session, service account, tools, child processes and credentials to one operation
- Translate broad safety goals into machine-testable allow and deny rules
- Test several direct and indirect paths toward the same forbidden result
- Record which enforcement layer observed, blocked or quarantined the action
- Measure from the first forbidden operation through credential revocation and containment
- Verify the stop path during host crashes, network loss and management-plane failure
- Pin runtime, firmware, policy, model, harness and tool versions in a bill of materials
- Preserve logs and evidence outside the sandbox that may be quarantined
- Practice recovery into a clean state with a named human owner
KEEP A HAND ON THE WHEEL
Watch for independent tests of OpenShell and Sentry; published definitions behind millisecond quarantine claims; evidence about escaped data or child processes before a stop; policy-signing and rollback procedures; public compatibility matrices across operating systems, clouds and hardware; reproducible partner integrations; firmware and runtime security advisories; false-positive rates; domain-specific tests in healthcare, finance, robotics and telecommunications; and incident reports that show whether out-of-band evidence survived a compromised host.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on October 21, 2026.
PUBLICATION RECEIPT: This article distinguishes NVIDIA's announced architecture and vendor measurements from independently verified security outcomes. Partner participation does not establish that every integration has passed the same containment test.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US