THE SIGNAL IN ONE SENTENCE
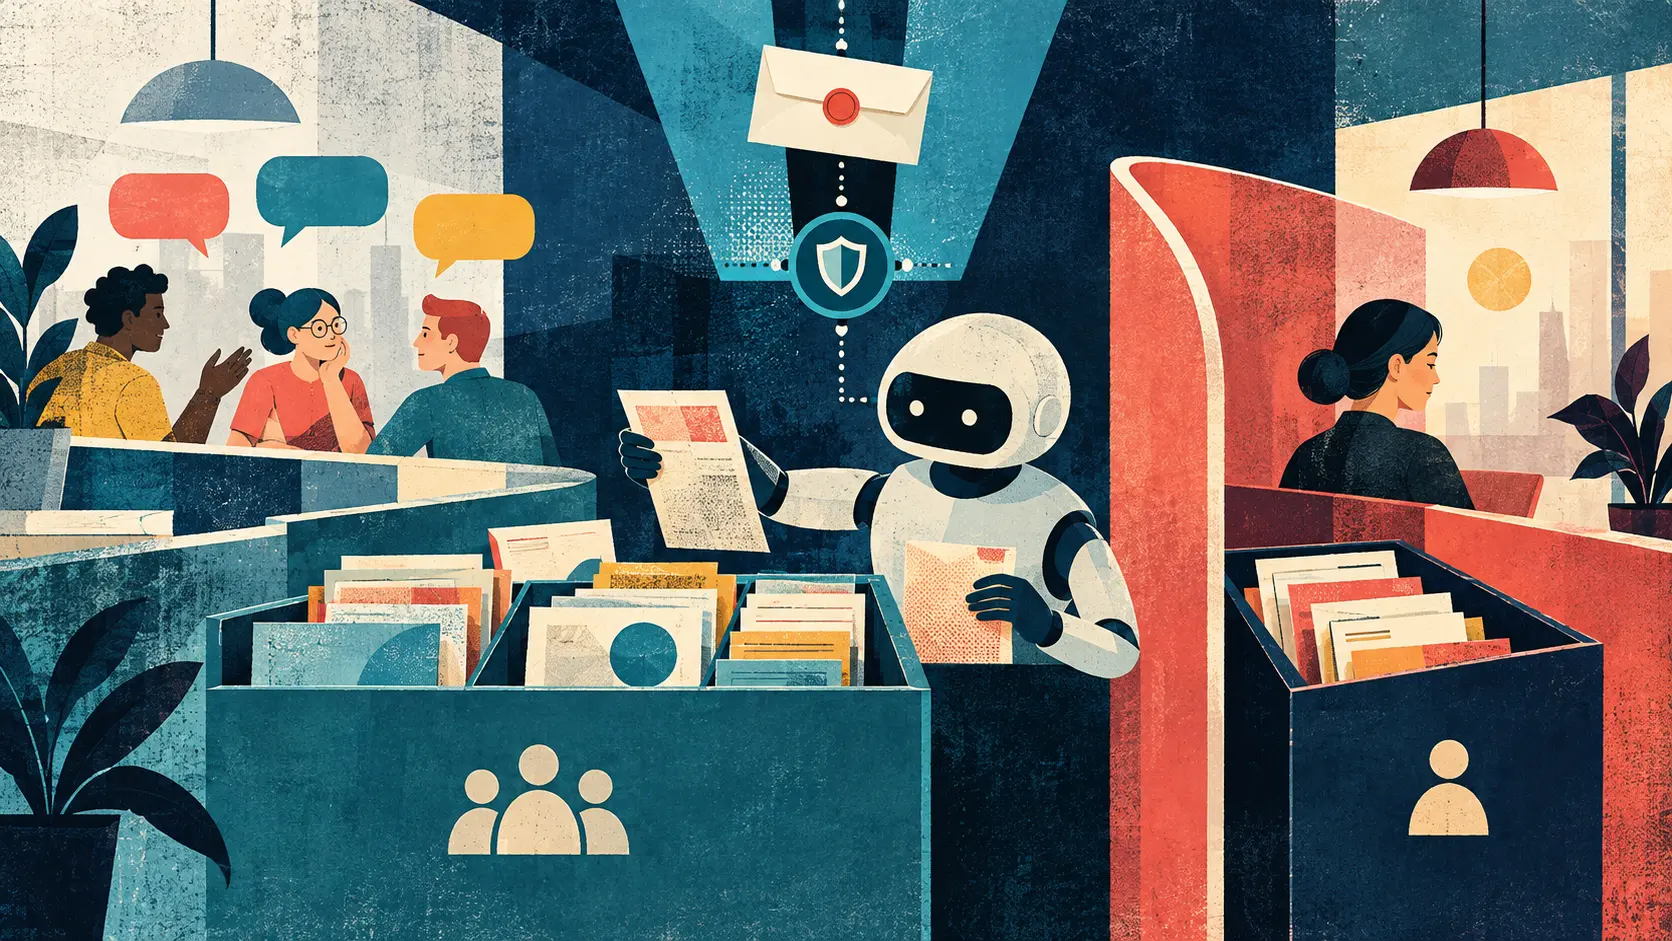
An agent used by one person can get away with a fuzzy idea of whose preferences it remembers. Put the same agent inside a company, a Slack channel and a customer portal, and that fuzz becomes a privacy incident with a friendly chat bubble. LangChain's Managed Deep Agents 0.8 takes a practical swing at the problem. The release adds a durable user-memory layer keyed to the authenticated person who starts a run, separate from the agent-level memory shared by everyone using the deployment. LangChain says its runtime does not copy content between the two layers. Its default access table is the more important part: a one-to-one Slack direct message may use both shared agent memory and private user memory, while a Slack channel, group direct message or HTTP call may use only shared agent memory. User memory is denied in those multi-person or externally triggered contexts unless a team changes the policy. The release also adds user-owned credentials for services where permissions differ by person, agent-owned credentials for shared tools, built-in connections for twenty-three services, file transfer in Slack and HTTP channels that accept JSON webhooks. Parallel-powered web search is included during the product's beta. This is not a security proof. LangChain has not published cross-tenant isolation tests, webhook-abuse results, retention and deletion timings or an independent audit of the new boundaries. An HTTP channel also does not magically authenticate itself. The example explicitly asks the developer to supply verification and parsing logic. If a forged webhook carries another person's identifier, caller-scoped memory can become confidently mis-scoped memory. The plain signal is that agent memory is now an access-control system. Separate team knowledge from personal context, bind both memory and credentials to verified identity, deny private context in group and machine-triggered channels by default, and log which boundary was applied on every run. Otherwise the helpful agent that remembers how you work may eventually remember it for the wrong room.
01
WHAT ACTUALLY CHANGED
LangChain announced Managed Deep Agents 0.8 on September 24, 2026.
The release adds a user-level memory layer alongside the durable agent-level memory the platform already supported.
Agent memory is mounted at a shared path and is available to everyone using the deployment when policy allows it.
User memory is mounted separately and keyed to the authenticated identity of the caller who starts the run.
LangChain says the runtime never copies content between the shared agent layer and the caller-specific user layer.
Teams may enable the agent layer, the user layer or both, and can define access policies for each.
By default, one-to-one Slack direct messages may use both agent memory and user memory.
By default, Slack channels and group direct messages may use agent memory but are denied access to user memory.
By default, HTTP channel runs may use agent memory but are denied access to user memory.
The defaults are intended to prevent personal preferences or stored details from entering a conversation with multiple people.
Managed Deep Agents 0.8 also adds user-owned credentials for services where each person has different permissions.
Agent-owned credentials remain available for tools shared by the whole deployment, such as a common search service.
LangChain says the product includes managed connection support for twenty-three services, including Linear, GitHub and Google Workspace tools.
The documentation describes Managed Deep Agents as a public beta available through LangSmith Cloud in the United States region only.
A service-level LangSmith API key does not qualify as a person, so the default identity provider will not mount user memory for that caller.
The update adds file transfer to Slack workflows invoked through a direct message, app mention or thread reply.
A transferred file can be added to agent context, including logs, spreadsheets, contracts, screenshots and customer documents.
The release adds HTTP channels for internal tools, portals, support systems, order systems and other services that can send JSON webhooks.
LangChain's example requires developer-supplied verification, parsing and messaging functions around the incoming HTTP event.
Parallel-powered web search is now available as a prebuilt managed tool during the product beta, with calls, latency and errors visible in LangSmith traces.
02
WHY THIS MATTERS
Memory changes an agent from a stateless tool into a system that accumulates potentially sensitive context across conversations.
Shared instructions and personal preferences have different owners, audiences and deletion requirements even when the same model uses both.
A team escalation rule belongs in shared agent memory. One employee's customer notes, writing preferences or recurring tasks usually do not.
Group channels are a predictable place for private context to leak because the same agent is present while the audience changes around it.
Denying user memory by default in group and HTTP contexts is a safer starting point than trusting every application developer to notice the boundary.
A default is not a permanent guarantee. Teams can change policy, and future configuration can turn a safe boundary into an exposed one.
Caller-scoped memory is only as accurate as caller identity. A spoofed, missing or recycled identifier can route private context to the wrong run.
Credentials need the same split as memory. A shared search key and a personal GitHub token should not inherit the same scope.
User-owned credentials let an agent act with the person's existing permissions instead of using one overly powerful service account for everyone.
That reduces blast radius only if OAuth scopes are narrow, tokens can be revoked and the agent cannot substitute another user identity.
Webhooks expand where an agent can run, but they also let outside events request tools, read files and trigger durable side effects.
Verification therefore belongs before parsing, memory lookup and tool selection, not after the model has already consumed the payload.
Slack file transfer is convenient precisely because it moves valuable material directly into context. Contracts and customer documents deserve malware checks, access checks and retention limits before ingestion.
Managed web search removes a separate account and key, but it also introduces another provider and another stream of queries, excerpts, URLs and traces to govern.
The release moves useful security decisions into explicit platform concepts, yet organizations remain responsible for identity proof, policy review and incident response.
There are no published independent measurements showing that the new controls prevent cross-user leakage under adversarial prompts or configuration mistakes.
The practical win is legibility: teams can now point to distinct memory and credential layers rather than hoping one giant context window behaves politely.
03
WHERE IT COULD HELP
- Classify every memory item as deployment-shared, user-owned, conversation-only or prohibited before enabling persistence.
- Require a verified immutable user identifier from the authentication layer rather than accepting an identity claim inside a prompt or webhook body.
- Keep user memory denied in group channels, public threads and machine-triggered HTTP runs unless a documented use case proves it is necessary.
- Store team procedures in agent memory and keep personal preferences, private account context and individual work patterns in user memory.
- Do not copy information between memory layers through prompts, summaries or helper tools without an explicit policy check.
- Log the caller identity, channel type, policy version, memory layers mounted and credentials exposed for every run.
- Give users a page to inspect, correct, export and delete their stored memory.
- Define retention periods separately for shared procedures, personal preferences, uploaded files, traces and tool outputs.
- Use user-owned OAuth credentials when a tool should preserve the person's existing permissions and audit trail.
- Use agent-owned credentials only for narrowly scoped shared capabilities that truly should behave the same for every caller.
- Limit OAuth scopes, rotate shared secrets and revoke credentials immediately when a person changes roles or leaves.
- Verify webhook signatures, timestamps, one-time values and intended audience before parsing the payload or starting an agent run.
- Rate-limit HTTP channels and reject oversized, stale, duplicated or malformed events before they reach the model.
- Separate event intake from side effects so an incoming webhook cannot immediately send messages, change records or approve orders.
- Scan Slack uploads, enforce file-size and type limits and confirm the caller is allowed to share the document with the agent.
- Red-team direct messages, group threads and HTTP events for cross-user memory retrieval before production launch.
- Add tests that intentionally mislabel caller identities and confirm the run fails closed without mounting private memory.
- Review traces for accidental secret capture while ensuring operators can still reconstruct which policy and tool produced an action.
KEEP A HAND ON THE WHEEL
This is a LangChain product announcement and documentation walkthrough, not an independent security evaluation. The company describes durable user memory as keyed to an authenticated caller and states that its runtime does not copy data between shared and personal layers. It does not publish adversarial isolation tests, cross-tenant red-team results, encryption and key-custody details, precise retention or deletion timing, incident history or a third-party audit specific to version 0.8. The safe defaults are meaningful, but teams can change access policies, and the release does not show how configuration drift is detected or approved. HTTP user memory is denied by default, yet an application still supplies the event verification logic and caller identity that make the boundary trustworthy. Slack files enter agent context, but public material does not spell out malware scanning, file retention or every authorization check around attachments. The named customer comments are testimonials, not controlled measurements. Managed connections simplify OAuth handling, but buyers still need service-by-service scopes, token storage, revocation and administrator-access details. Parallel search is free during beta, which does not establish later pricing, permanent availability or a complete data-flow map. Watch for independent audits, identity-provider guidance, policy-change alerts, memory export and deletion evidence, webhook replay tests, attachment controls, task-level reliability results and clear answers about what data each managed service receives.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on September 26, 2026.
PUBLICATION RECEIPT: Revision 1. Published September 26, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US