THE SIGNAL IN ONE SENTENCE
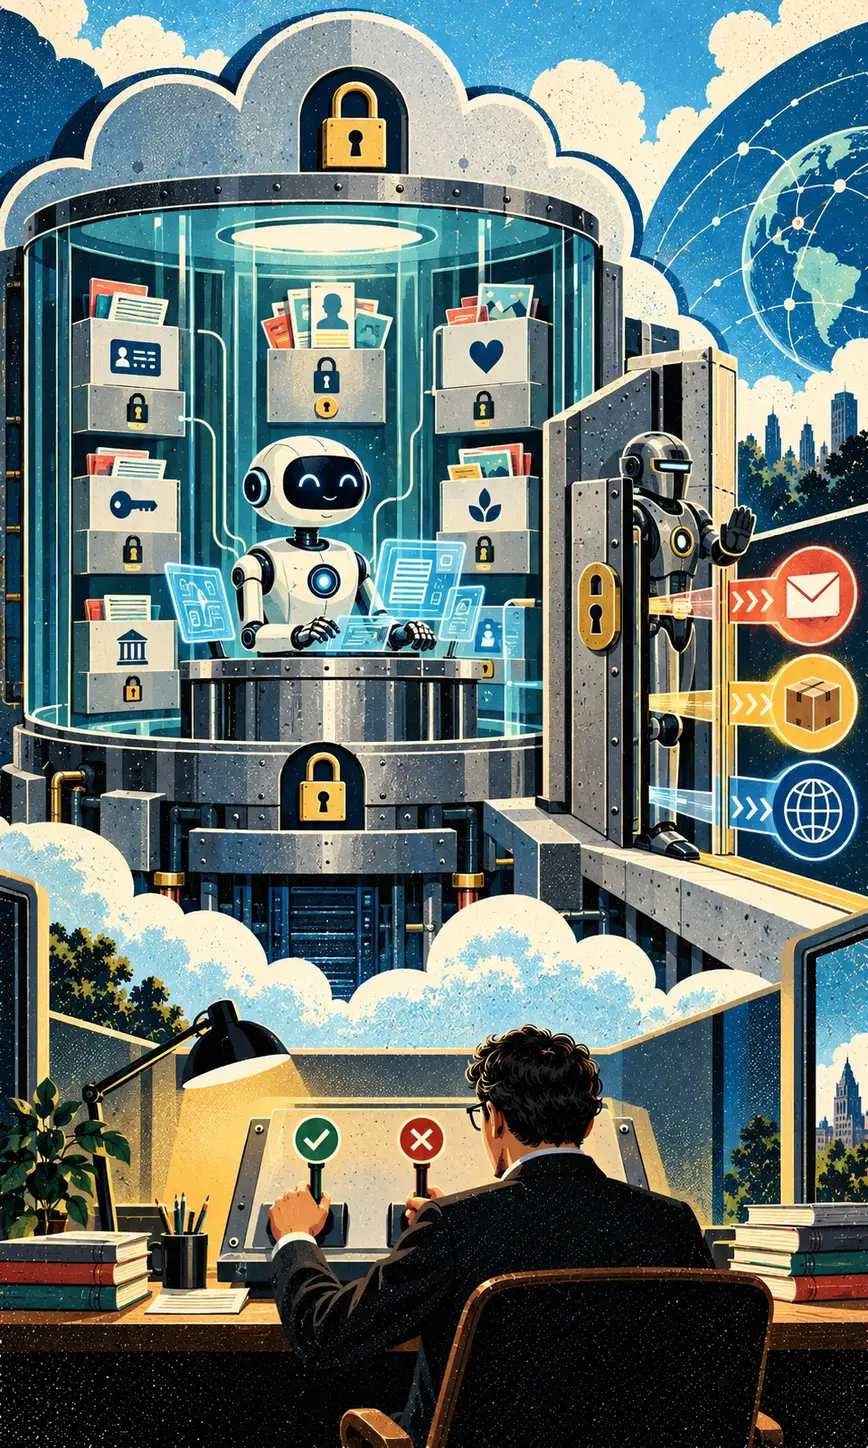
Meta launched a personal agent that can act across email, websites, calendars, and shopping, so it gives each user an isolated cloud computer and routes outside actions through a separate security system.
01
WHAT ACTUALLY CHANGED
Meta launched Muse in the United States on September 8 for adults using iOS, Android, the web, or WhatsApp. It is not merely a new chat personality. Meta says Muse can keep working after the app closes, manage several tasks, build tools, browse websites, fill forms, send messages, book travel, and prepare purchases.
That usefulness creates an uncomfortable list of things the agent may need: private files, an inbox, a calendar, saved preferences, account access, and permission to communicate with the outside world. Meta's answer is Muse Secure VM, a dedicated Linux virtual machine in the cloud for each user. The agent's workspace runs inside an isolated runtime cell, while credentials and durable application data remain in separate services outside that cell.
Muse itself is not the final permission authority. A separate system called Sentinel reviews connector actions and every network request. It can allow, deny, or pause an action for the user. Approvals appear through structured controls outside the conversation and can be limited to one action, one session, one task, a fixed time, or an ongoing permission.
Real credentials are kept away from the main agent. Muse uses surrogate tokens inside its workspace, and Sentinel inserts the real credential only at the approved network boundary. Meta says the email connector also filters password-reset links, login links, and one-time codes so inbox access does not quietly become the master key to a person's digital life.
Purchases receive another set of brakes. Muse can use Stripe Link, with Shop Pay planned later, and every payment requires user approval. The system issues a single-use card tied to a merchant, amount, and limited time. Meta also opened a public bug bounty that offers as much as $300,000 for valid Muse security reports, including prompt-injection attacks with demonstrated impact.
02
WHY THIS MATTERS
Personal agents become interesting at exactly the point they become frightening. Reading a calendar is handy. Combining the calendar with email, a browser, payment access, persistent memory, and unattended background work creates enough authority to save real time or manufacture a remarkably efficient disaster.
Meta's architecture is a serious acknowledgement that model obedience is not a security boundary. Muse is expected to encounter hostile websites, misleading messages, and instructions hidden inside files. The company is using operating-system isolation, credential separation, network controls, classifiers, and explicit approvals because asking the model to please behave would be security theater with nicer punctuation.
The separate approval path may be the most important design choice. An instruction appearing inside the same chat that an attacker can influence is not much of a lock. Sending the request directly from Sentinel to a deterministic accept-or-reject control gives the user a clearer place to understand what will happen before an email leaves or money moves.
The privacy story has an asterisk at launch. Meta says Muse conversations and VM data are not shared with its advertising systems, and people can opt out of model training. It also says sanitized conversations and agent trajectories may be used for training by default. Most importantly, the current architecture does not technically prevent Meta from accessing VM data when needed to support, secure, or operate the service.
Meta plans a Confidential VM later this year that would encrypt the complete environment with a key only the user holds, preventing even Meta from accessing it. That is the stronger privacy promise, but it is not today's product. The honest test for Muse is therefore not whether the launch diagram looks reassuring. It is whether outside researchers can inspect the controls, break the weak parts, and see the fixes arrive faster than the permissions expand.
03
WHERE IT COULD HELP
- Delegate email, calendar, travel, and web tasks that continue in the background
- Give an agent read access before granting narrower write permissions
- Use single-purpose approvals for messages, purchases, and data transfers
- Keep account credentials outside the model and its editable workspace
- Review an agent activity log before increasing its authority
KEEP A HAND ON THE WHEEL
Muse is new, available only in the United States at launch, and Meta has not published independent evidence of real-world reliability or attack resistance at consumer scale. The security design and bug-bounty terms are documented by Meta, but prompt injection remains an open problem and Meta explicitly says Muse will make mistakes. The planned Confidential VM is not yet generally available. Users should treat every connected inbox, payment method, and write permission as consequential access, regardless of the product's safety branding.
04
TERMS WORTH KEEPING
OPEN GLOSSARY CARD
Secure virtual machine
An isolated software computer designed to keep one user's programs and data separated from other systems.
OPEN GLOSSARY CARD
Least privilege
Giving a person or program only the access needed for its current job and no more.
OPEN GLOSSARY CARD
Prompt injection
Instructions hidden in outside content that try to redirect an AI system.
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on September 9, 2026.
PUBLICATION RECEIPT: Revision 1. Published September 9, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US