THE SIGNAL IN ONE SENTENCE
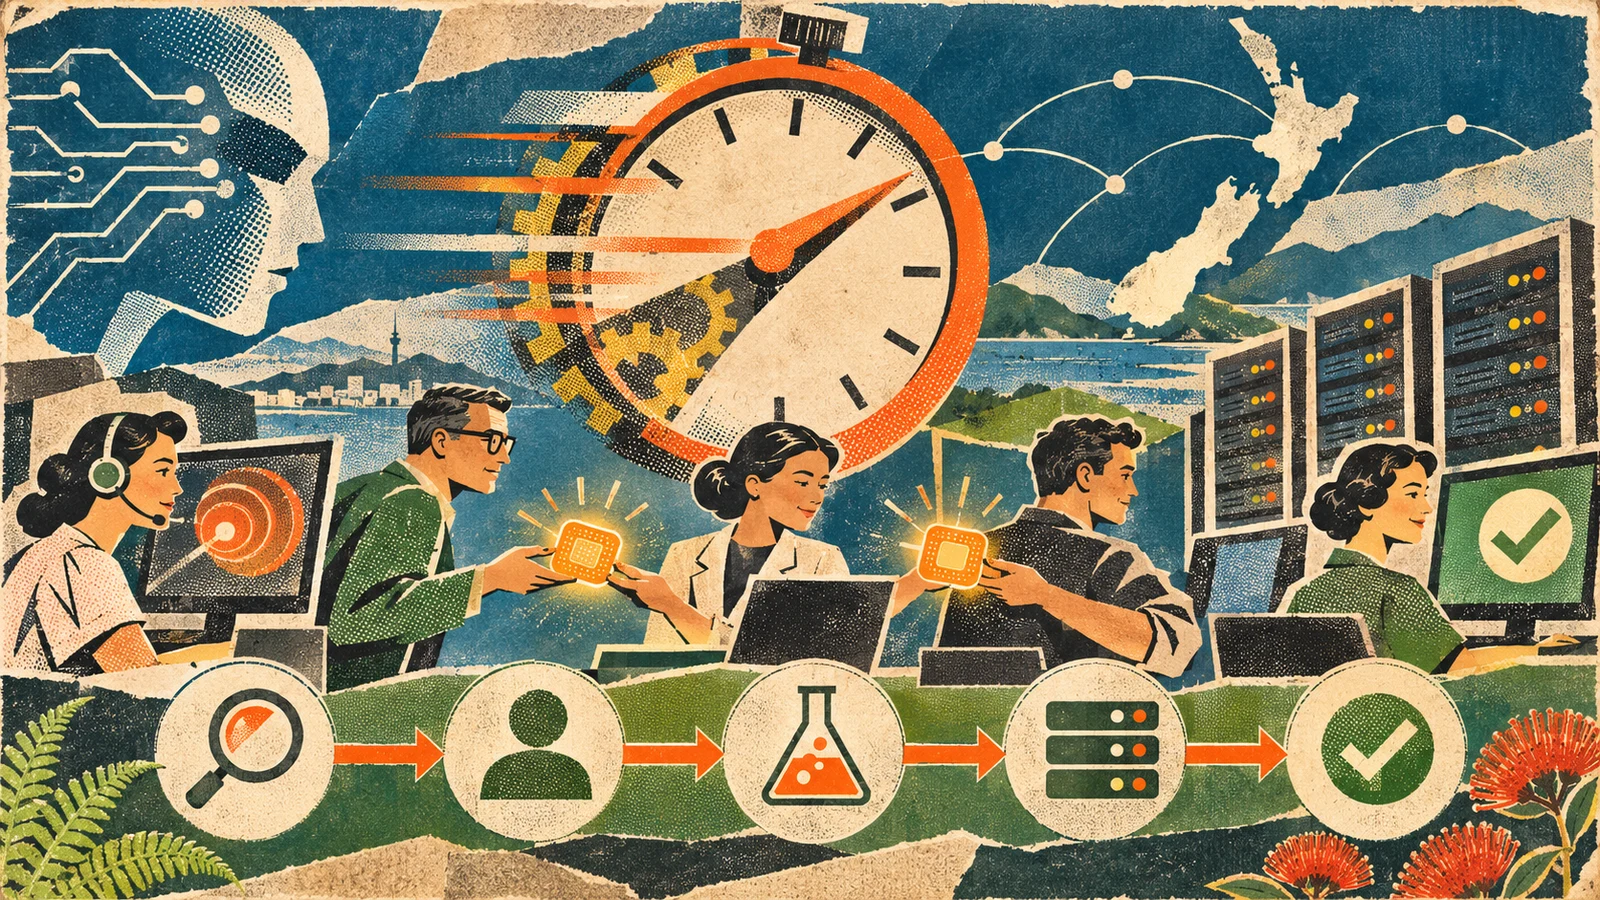
New Zealand's National Cyber Security Centre has a blunt message for leaders: frontier AI is likely to make some cyber attacks faster, cheaper and easier to scale. The useful response is not to buy a larger red dashboard. It is to shorten the patch clock. The NCSC published its Cyber Threat Report 2026 on September 24. In the report's first strategic judgement, the agency says AI can help attackers discover vulnerabilities, automate reconnaissance, try passwords at scale and make phishing or impersonation more convincing. The same tools can help defenders search for weaknesses and respond more quickly. That is an assessment of direction, not a stopwatch reading from the future. The report does not say every attack will become a machine-speed event or quantify exactly how much faster a particular exploit will arrive. It does ask leaders whether their organizations have enough people and resources for a faster tempo of patching and updates. That question deserves an operational answer. Start the clock when a critical weakness becomes relevant to your environment. That may be a vendor advisory, an internal discovery, a report from a researcher or evidence that an exploit is already being used. Then record every handoff. When did the team confirm that the affected product exists in the organization? When did someone determine whether it is exposed? When was an owner assigned? When was a mitigation approved? When did testing start? When did the fix reach production? When did somebody independently confirm that the vulnerable service was no longer reachable? The final confirmation matters. A ticket marked complete is not the same as a closed exposure. This sounds like basic operations because it is basic operations. The NCSC's recommendations are refreshingly unromantic: reduce the attack surface, patch faster, deal with legacy systems, strengthen identity and access controls, and prepare the incident response team. AI does not make those jobs obsolete. It makes excuses about them age faster. The first practical metric should be time to owner. A security alert can sit in a queue while three teams debate whether the server belongs to infrastructure, the application group or a supplier. That argument is part of the patch clock. Measure it. Set a short assignment target for critical, internet-facing systems. If the owner is uncertain, give the incident lead temporary authority to assign one. The organization can settle the org chart later. The vulnerability will not wait for a tidy meeting invite. Next, separate mitigation time from patch time. Sometimes the vendor fix is not ready. Sometimes the patch can break a clinical device, a factory line, a payroll run or an emergency service. A safe organization should not pretend those constraints disappear because the threat moved faster. It should have pre-agreed emergency options. Disable a feature. Restrict an exposed service. Put a vulnerable system behind stronger authentication. Block a protocol. Segment a network. Increase logging. Move a workload behind a protective control. Take the service offline when the risk justifies it. Record the mitigation, its owner, its expiry date and the test showing it actually reduced exposure. Temporary controls have a charming habit of becoming permanent furniture. Testing still matters. A reckless patch can turn a cyber risk into an outage. That is especially serious in operational technology, healthcare, transport, local government and other environments where digital systems touch physical safety or essential services. The answer is not to skip testing. It is to build a faster safe lane before the crisis. Maintain representative test environments. Keep rollback procedures current. Pre-approve emergency change windows. Know which systems can tolerate automated deployment and which require human supervision. Practice restoring from backups. Put the application owner, security team and operations lead in the same drill before a real exploit starts the clock. Then measure the distribution, not just the average. An organization can report a lovely average patch time while a handful of dangerous systems remain exposed for months. Publish the median and the 90th percentile by severity and asset class. Separate internet-facing systems, employee devices, cloud services, operational technology and unsupported legacy equipment. Track the slow pieces individually: Discovery to asset confirmation. Confirmation to owner assignment. Owner assignment to mitigation decision. Decision to tested deployment. Deployment to independent verification. That sequence turns a vague promise to patch faster into a map of the bottleneck. If asset confirmation takes two days, the organization probably needs a better inventory. If owner assignment takes a day, governance is the problem. If testing takes two weeks, fund the test environment. If deployment stalls on supplier permission, change the contract. If verification never happens, the process is measuring ticket closure instead of risk closure. The NCSC's incident figures add local context without proving that AI caused the trend. The agency received 4,673 incident reports in the year to June 30, down from 5,995 in the previous period. It triaged 369 incidents for specialist support or potential national significance, up from 331. Of those, 162 were assessed as likely criminal or financially motivated. The report says four incidents reached its most serious categories, as many as in the previous ten years combined. It also records $23.8 million in direct financial losses reported to the NCSC, down from $26.9 million. Those numbers need care. The agency says they describe the incidents reported to it and the cases it worked on. They are not a complete census of every cyber incident in New Zealand. Year-to-year movement can reflect reporting behavior, case definitions and the mix of incidents, not only a changing threat. The report also cites examples supplied by others, including an AI-related espionage campaign described by Anthropic. Treat that as Anthropic's assessment, not an independently established NCSC finding. The same discipline should apply to the early 2027 warning. The NCSC says malicious actors may have advanced AI-enabled capabilities by then. That is a planning judgement. It is a reason to prepare, not a measured prediction with a guaranteed date. Preparation must reach suppliers. Many New Zealand organizations, especially smaller businesses, schools, health providers, councils and community services, do not control every layer of their technology. Their patch clock runs through software vendors, managed-service providers and cloud platforms. Contracts should require timely vulnerability notices, clear severity information, supported versions, emergency mitigation guidance, patch availability, change logs and confirmation when a supplier-controlled exposure has been fixed. Ask how quickly the provider can identify affected customers and whether it will share evidence after an incident. For small organizations, the answer cannot be a giant security operations center in every office. Shared services, sector playbooks, managed patching, trusted advisories and practical procurement standards matter more than another complicated portal. Identity controls deserve equal attention. If AI improves phishing and impersonation, patching software alone will not stop account takeover. Use phishing-resistant authentication where possible. Limit administrator privileges. Review dormant accounts. Require a second person for high-impact financial and access changes. Make the help desk verify unusual recovery requests through a separate channel. Test those controls with realistic exercises, including convincing audio, video and written impersonation. The purpose is not to embarrass staff. It is to find the process that allows one persuasive message to override every other safeguard. AI can help defenders inside the same loop. It can summarize advisories, match them to an asset inventory, prioritize likely exposure, suggest tests and search logs for signs of exploitation. Keep a person accountable for the decision. The model may miss an asset, invent a package relationship, misunderstand a version or confidently recommend a mitigation that breaks the service. Preserve the source advisory, the model output, the human decision and the verification result. Use automation to remove waiting, not responsibility. The board-level view can fit on one page. Show the number of critical exposed weaknesses, the median and 90th-percentile time through each stage, the oldest unresolved case, unsupported systems, emergency mitigations past their expiry date, suppliers that missed notice or patch obligations, and the results of the last incident exercise. Add the resources required to change the numbers. If the slowest stage needs two release engineers, say so. If a hospital needs a safer test environment, fund it. If the oldest systems cannot be patched, put their isolation or replacement date on the capital plan. If a small public service depends on one overworked contractor, fix the concentration risk. The strategic signal from New Zealand is not that an AI attacker is about to press a magic button and defeat every network. It is that parts of the attack cycle can compress while many organizations still move at committee speed. Measure the patch clock. Expose the waiting. Protect the safety checks. Give people authority to act. Pay for the boring infrastructure that turns a warning into a verified fix. The dashboard can come later.
01
WHAT ACTUALLY CHANGED
New Zealand's National Cyber Security Centre published the Cyber Threat Report 2026 on September 24, 2026.
The report assesses that frontier AI will increase both cyber risks and defensive opportunities.
The NCSC says AI can accelerate vulnerability discovery, reconnaissance, brute-force activity and personalized phishing or impersonation.
The agency advises organizations to reduce attack surfaces, accelerate patching, address legacy systems, strengthen identity and access controls, and prepare incident response.
It asks leaders whether they have enough people and resources for a faster tempo of patching and updates.
The NCSC received 4,673 incident reports in 2025/26, compared with 5,995 in the previous year.
It triaged 369 incidents for specialist support or potential national significance, up from 331.
Of those triaged incidents, 162 were assessed as likely criminal or financially motivated.
The official release says four incidents reached the two most serious categories, matching the previous ten years combined.
Reported direct financial losses were $23.8 million, down from $26.9 million.
02
WHY THIS MATTERS
Faster vulnerability discovery can shorten the time between a public weakness and active exploitation.
The delay inside an organization often comes from inventory gaps, unclear ownership, slow testing or supplier dependencies rather than the patch itself.
A single average can conceal a small number of critical systems that remain exposed for months.
Essential services need a fast lane that preserves safety testing, rollback and human authority.
Unsupported legacy systems turn a patching problem into a replacement, isolation and capital-planning problem.
Small organizations depend on shared services and supplier performance, so the patch clock must include contractual handoffs.
Improved phishing and impersonation make identity controls and payment verification as important as software updates.
AI can help defenders prioritize work, but its output still requires source evidence, human review and independent verification.
Measuring every handoff makes it possible to fund the actual bottleneck rather than buying a generic security product.
Closing a ticket does not prove that an exposure is closed.
03
WHERE IT COULD HELP
- Start the clock when a critical weakness becomes relevant to the organization, not when a meeting is scheduled.
- Track discovery to asset confirmation, owner assignment, mitigation decision, testing, deployment and verification separately.
- Publish median and 90th-percentile times by severity and asset class.
- Set a short owner-assignment target for critical internet-facing systems.
- Maintain an emergency mitigation menu for cases in which a patch is unsafe or unavailable.
- Give every temporary mitigation an owner, evidence check and expiry date.
- Maintain representative test environments and current rollback procedures.
- Pre-approve emergency change windows and practice them before a crisis.
- Independently verify that the vulnerable service is no longer exposed after deployment.
- Keep unsupported systems on an isolation or replacement plan with a funded date.
- Require suppliers to provide timely notices, supported-version guidance, mitigations, patches and closure evidence.
- Use phishing-resistant authentication and separate-channel verification for high-impact changes.
- Exercise response procedures with realistic AI-assisted impersonation scenarios.
- Preserve the source advisory, AI output, human decision and verification result when automation assists triage.
- Report the oldest unresolved critical exposure and every emergency mitigation past its expiry date.
- Attach staffing, test-environment, supplier and replacement costs to the board-level patch-clock report.
KEEP A HAND ON THE WHEEL
The NCSC report is a strategic threat assessment. It does not measure a universal increase in attack speed or prove that every attacker already has advanced AI capabilities. The agency's warning about possible advanced capabilities by early 2027 is a planning judgement, not a guaranteed forecast. Incident counts describe reports received and cases handled by the NCSC from July 1, 2025 through June 30, 2026. The report says its statistics and case studies are illustrative and do not represent every cyber incident in New Zealand. Lower total reports and lower reported direct losses should not be read as proof that national cyber risk fell. Reporting behavior, definitions and the mix of incidents can change the totals. The Anthropic campaign example is attributed to Anthropic's assessment and was not independently established by the NCSC. Faster patching must not erase safety testing, rollback, service continuity or human approval in essential and physical systems. Watch for sector-specific patch-time data, independent evidence of AI-assisted attack speed, supplier response standards, support for smaller organizations, legacy-system replacement funding and exercises that test whether the faster process works under pressure.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on November 17, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US