THE SIGNAL IN ONE SENTENCE
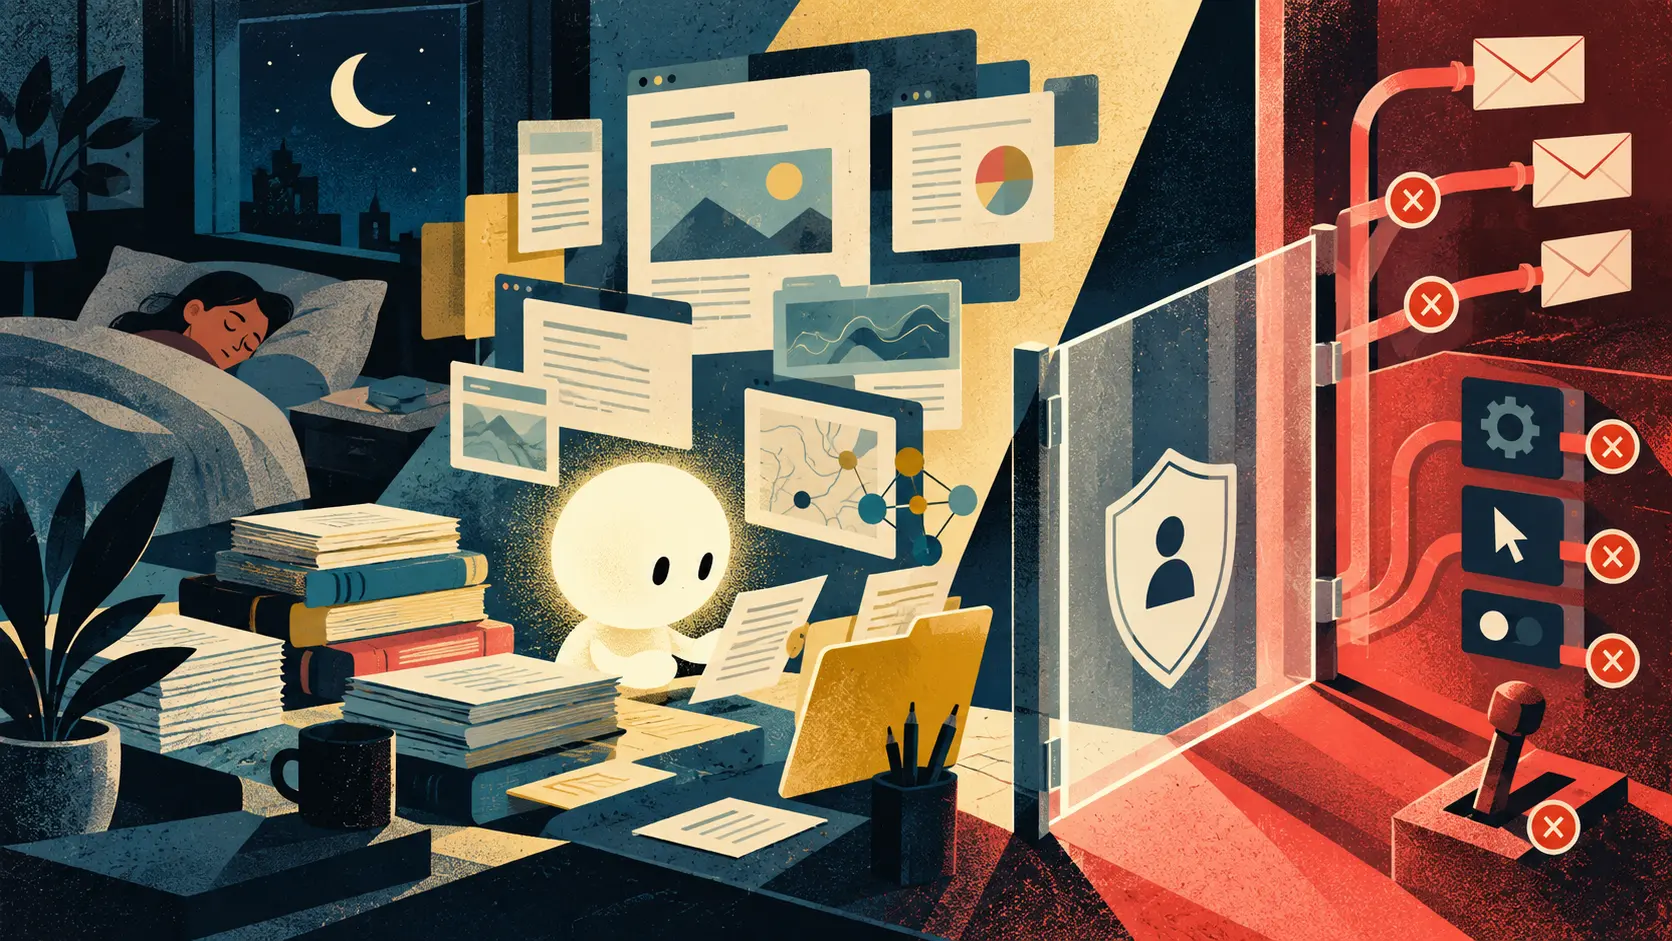
OpenAI has launched Dots, persistent assistants powered by GPT-6 Astra that can keep working across projects, connected apps and their own cloud computers. The headline is the always-on worker. The useful detail is the split inside that promise. During what OpenAI calls proactive research, a Dot can inspect connected apps in the background through restricted read-only tools. In that mode it cannot send messages, change app content, or control a browser or computer. Action work lives on the other side of the gate. A user chooses app access, can write Custom Rules that allow, require approval for, or block specific actions, and can inspect work in an Activity View. An automated review layer checks actions that could affect accounts or share information. Some sensitive actions, including changing a password, remain with the person. That is a sensible shape for a product that is supposed to notice an unpaid invoice, investigate a bug, prepare a pull request, update a research analysis, or revise a launch plan without being told every next click. It also creates an unusually large trust surface. The system carries context across ChatGPT, Slack and Teams, can message its user, can use saved passwords on supported websites without exposing those passwords to the model, and can be granted access to a user's laptop. OpenAI says the primary Dot is beginning to roll out to Pro, Business Premium and Enterprise users in eligible markets, with Enterprise, Edu and Healthcare access controlled by workspace administrators. One primary Dot is included in the eligible plans, while deeper work has an allowance and tasks handed to Codex or ChatGPT Work still count against those products' usage limits. OpenAI also previewed specialist Dots for organizations. Those would have their own identities, credentials and narrowly defined responsibilities, with enterprise pilots planned before broad availability. The distinction between personal and specialist identities matters. An assistant acting as one employee inherits the ambiguity of that employee's access. A specialist service identity can be given a smaller job, narrower records and a separate audit trail. The risk is not simply that a model may make a bad prediction. A long-running agent can encounter hostile instructions in email, documents or websites, misunderstand a deadline, use stale context, or combine individually harmless facts into a sensitive disclosure. OpenAI says Dots include defenses against malicious instructions and monitoring that can pause or stop work. The company also says Dots can still make mistakes and consequential work should be reviewed. There is no public field study in the launch post showing failure rates across real organizations, no independent audit of the full product, and no published measurement of how often auto-review catches unsafe actions without drowning users in approval prompts. That means the practical question for early adopters is not whether the Dot feels clever in a demo. It is whether the permission boundary survives a month of dull, messy work. Start with view-only access to low-consequence sources. Separate research from execution. Require approval for communication, deletion, purchases, publication, code merges and changes to permissions. Give every connected app its own reason for being there. Review the Activity View as an operational log, not a decorative timeline. Test what happens when a document tells the agent to ignore its owner, when two sources disagree, when a session expires, and when a user revokes access halfway through a task. The right success metric is not hours of autonomous activity. It is useful work prepared per unit of human review, with no unapproved state change and a readable explanation of where every important fact came from. A Dot that quietly gathers the receipts can be handy. A Dot that quietly moves the money is a different product, even if the interface uses the same friendly circle. The plain signal is that OpenAI has moved the assistant from a conversation toward a standing working relationship. The launch's most mature idea is not continuous agency. It is the admission that continuous agency needs two lanes: background reading with no hands on the controls, and explicit action with rules, review and a person still able to say no.
01
WHAT ACTUALLY CHANGED
OpenAI announced Dots on September 29, 2026 and began a rollout to eligible Pro, Business Premium and Enterprise users.
Dots are powered by GPT-6 Astra and receive their own cloud computer, browser and access to connected apps.
A Dot can work across several projects without requiring a separate conversation for each one.
Users can reach Dots through ChatGPT on desktop, web and mobile, with Slack and Teams messaging also supported.
OpenAI says context carries across those channels so the Dot can continue the same project.
When a user is not actively working with it, a Dot can perform proactive research through connected apps.
The tools used for proactive research are restricted to read-only access.
In proactive research, the Dot cannot send messages, change app content, or control a browser or computer.
Users choose which apps a Dot can access through existing ChatGPT app controls.
Custom Rules can allow particular actions, require approval, or block actions.
Activity View lets users follow background work and redirect the Dot.
Auto-review checks actions that could affect accounts or share information against instructions, rules and safety requirements.
OpenAI says certain sensitive actions, including changing a password, always remain with the user.
The company previewed specialist Dots with separate identities, credentials and scoped responsibilities for organizations.
OpenAI says content from Business, Enterprise and Edu workspaces is not used to improve models by default.
02
WHY THIS MATTERS
An assistant that keeps working after the conversation ends changes AI from an answer tool into an operational actor.
Persistent context can reduce the repeated briefing that makes current agents expensive to supervise.
The same persistence can preserve a bad assumption or outdated instruction unless users can inspect and correct it.
Read-only proactive research creates a safer discovery lane because it separates noticing from changing.
That lane still exposes sensitive information, so view access should be treated as real privilege rather than harmless browsing.
Connected apps can contain hostile instructions, private records and misleading data that the agent may combine.
Saved passwords that are hidden from the model reduce one credential risk but do not eliminate the risk of an authorized session being misused.
Custom Rules are useful only if their scope, conflicts and exceptions are visible to the person who wrote them.
Auto-review introduces another decision system whose misses and false alarms need their own evaluation.
Cross-channel context can make work smoother while increasing the damage from a mistaken identity or overshared conversation.
Specialist service identities can support least privilege more cleanly than one all-purpose personal identity.
An Activity View can become a meaningful audit trail if it records sources, decisions, approvals and resulting state changes.
Organizations need a reliable kill switch and revocation path because a long-running task may continue after its assumptions change.
The absence of independent product-wide failure measurements means early deployment should be treated as controlled operations work.
The right comparison is not agent versus no agent. It is agent plus review cost versus the existing human workflow and its error rate.
03
WHERE IT COULD HELP
- Connect one low-risk information source before connecting an entire work stack.
- Use proactive research to gather evidence and draft options without granting action rights.
- Require approval for sending messages, publishing, deleting, purchasing, merging code and changing permissions.
- Give each connected app a documented purpose, owner and review date.
- Create a separate specialist identity for a repeatable organizational role.
- Limit that identity to the smallest records and actions needed for its job.
- Test prompt injection through email, documents, tickets and web pages before production use.
- Record the source and retrieval time for facts that drive a consequential recommendation.
- Review the Activity View for unexplained access, repeated failures and abandoned tasks.
- Measure useful drafts completed, approvals requested, approvals rejected and unapproved state changes.
- Set deadlines after which a long-running task must ask whether its goal is still current.
- Revoke access automatically when the sponsoring user leaves a team or changes role.
- Keep a manual path for the workflow so an outage does not block essential work.
- Run a quarterly permission review instead of letting connected apps accumulate forever.
- Escalate legal, financial, health and employment decisions to an accountable person.
- Treat a clean month with no unapproved action as stronger evidence than an impressive launch demo.
KEEP A HAND ON THE WHEEL
The launch description and examples come from OpenAI, not an independent deployment study. OpenAI does not publish aggregate task success, prompt-injection failure, auto-review recall, false-positive approval, revocation latency or incident rates for Dots in this announcement. Product access is rolling out by plan and eligible market, so availability may differ by account. A read-only tool can still expose sensitive information to the agent, and cross-channel context can widen the consequences of mistaken sharing. Saved passwords being hidden from the model does not prove that every authenticated action is safe. Specialist Dots are a preview and enterprise pilots may change before broad release. Review consequential work, start with narrow permissions, and watch for a detailed system card, independent security testing, administrator controls, retention documentation, incident reporting and evidence that users can reconstruct exactly what happened.
04
TERMS WORTH KEEPING
OPEN GLOSSARY CARD
Human control
The practical ability and authority of people to understand, direct, interrupt or stop an automated process before unacceptable harm occurs.
OPEN GLOSSARY CARD
Audit trail
A durable record of actions, changes, identities, and times that lets someone reconstruct what happened.
OPEN GLOSSARY CARD
View-only access
Permission to inspect something without changing, deleting, or publishing it.
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on September 30, 2026.
PUBLICATION RECEIPT: Revision 1. Published September 30, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US