THE SIGNAL IN ONE SENTENCE
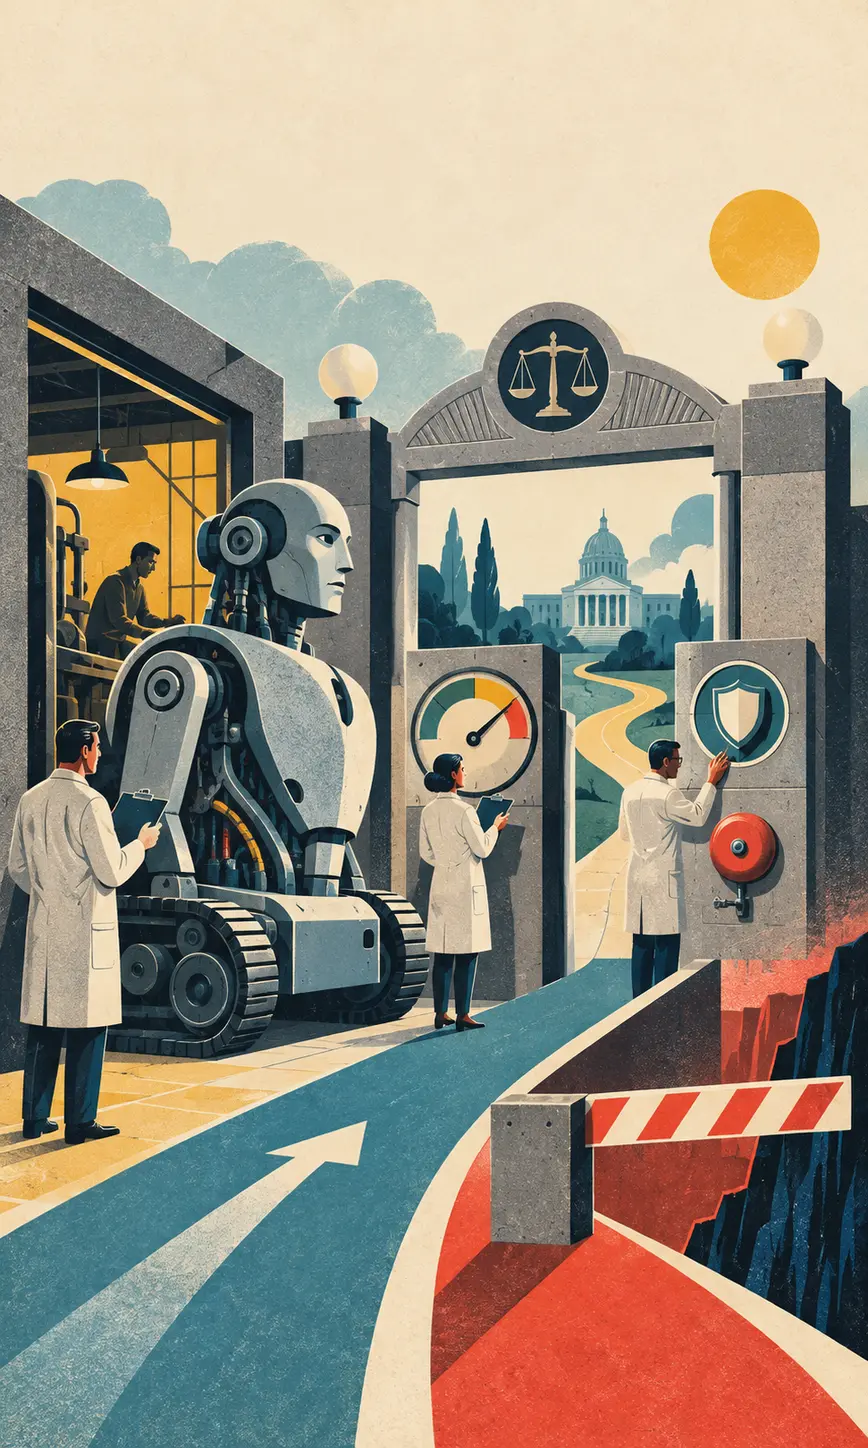
OpenAI is asking the United States to make its most powerful AI laboratories follow mandatory safety rules. The company says requirements should become stricter as a model becomes more capable and risky.
01
WHAT ACTUALLY CHANGED
OpenAI published a policy statement on September 9 calling for mandatory, capability-based national AI safety regulation. That word mandatory is the change worth circling. The company says advanced systems now demand common testing, independent assessments, stronger cybersecurity, clear incident reporting, national preparedness, and shared ways to measure progress toward AI systems that can help develop more capable successors.
The proposal is aimed at a small group of well-resourced frontier laboratories, not every startup, open-source contributor, or university researcher with a graphics card and a heroic electricity bill. OpenAI argues that obligations should rise with demonstrated capabilities and risks. It also says federal rules should avoid entrenching incumbents, pushing research overseas, or quietly becoming restrictions on open-weight models.
OpenAI linked the shift to recent advances in its Astra model, early evidence that AI can accelerate parts of AI research, and concerns about recursive self-improvement. The company says fully autonomous recursive self-improvement is not happening today and should not be pursued until it can be done safely. For Astra, OpenAI says it added monitoring across complete tool-using trajectories and an alignment-evaluation gate before wider internal deployment.
The company also endorsed four California bills. The state record shows Governor Gavin Newsom approved SB 813, which creates a process for designating independent AI risk assessors, and AB 1405, which establishes registration and independence rules for AI auditors, on September 9. At verification, SB 1119 on child safety for companion chatbots and AB 1864 on screening by gene-synthesis providers and equipment makers had passed the Legislature but had not yet been recorded as signed.
OpenAI wants laboratories to disclose serious incidents, including cases where a model circumvents another organization's security controls without authorization and materially reaches or damages protected systems or confidential information. It also wants industry standards for monitoring frontier systems, but says those voluntary standards should complement mandatory federal safeguards rather than replace them.
02
WHY THIS MATTERS
For years, frontier AI governance has leaned heavily on laboratories writing their own preparedness frameworks, running their own tests, and deciding how much of the result to publish. Useful work happens inside that arrangement, but the referee, team owner, and scoreboard operator can still be the same company. Independent assessment and public incident rules would give outsiders a formal role before the consequences arrive.
Capability-based regulation is an attempt to avoid treating every model like the same machine. A small system summarizing expense reports should not face the same obligations as a frontier system that can discover software vulnerabilities, plan long tasks, or assist biological research. The difficult bit is the trigger. If the law measures the wrong capability, laboratories will optimize for the test while risk wanders in through another door.
OpenAI has real incentives here. A national framework can replace a patchwork of state rules and make compliance easier for a large company with lawyers, security teams, and evaluation infrastructure. It can also raise costs for rivals if thresholds, audit access, or reporting duties are designed badly. A safety proposal does not become neutral merely because its nouns are sensible.
The California measures show what federal delay produces. One law will build a roster of qualified independent verification organizations, another will regulate AI auditors, and two pending bills target children's chatbots and gene-synthesis screening. That is an ecosystem of rules rather than one giant AI law. It may be more practical, but it also creates seams that companies, agencies, and courts will have to reconcile.
The larger signal is that voluntary commitments have reached their credibility ceiling. OpenAI is publicly asking elected officials to set minimum requirements that bind OpenAI too. The useful next question is not whether the company sounds serious. It is whether Congress writes measurable duties, funds competent oversight, protects independent evaluators, and imposes consequences when a frontier laboratory fails them.
03
WHERE IT COULD HELP
- Set capability thresholds that activate stronger duties as systems become more powerful
- Require independent pre-deployment assessments for frontier systems
- Mandate prompt reporting of serious AI security and safety incidents
- Protect startups and non-frontier research from rules designed for the largest laboratories
- Coordinate national rules with state safeguards and compatible international standards
KEEP A HAND ON THE WHEEL
This is a policy position from a company that would be regulated, not a federal bill or enacted national framework. OpenAI did not specify complete capability thresholds, enforcement powers, penalties, assessor access rights, or funding for an oversight body in this statement. Its claims about Astra monitoring and internal safety gates are self-reported. Two California bills cited here were signed on September 9, while SB 1119 and AB 1864 remained enrolled at verification and could still be signed, vetoed, or otherwise updated. Any final regime should be judged for measurable requirements, independent access, public accountability, effects on competition, and whether open research is restricted indirectly.
04
TERMS WORTH KEEPING
OPEN GLOSSARY CARD
Capability-based regulation
Rules that become applicable or stricter when an AI system demonstrates specified abilities or risks.
OPEN GLOSSARY CARD
Independent assessment
A review performed by a qualified party that is separate from the organization building or operating the system.
OPEN GLOSSARY CARD
Incident reporting
A requirement to disclose serious failures, breaches, harms, or near misses to specified authorities or affected parties.
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on September 10, 2026.
PUBLICATION RECEIPT: Revision 1. Published September 10, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US