THE SIGNAL IN ONE SENTENCE
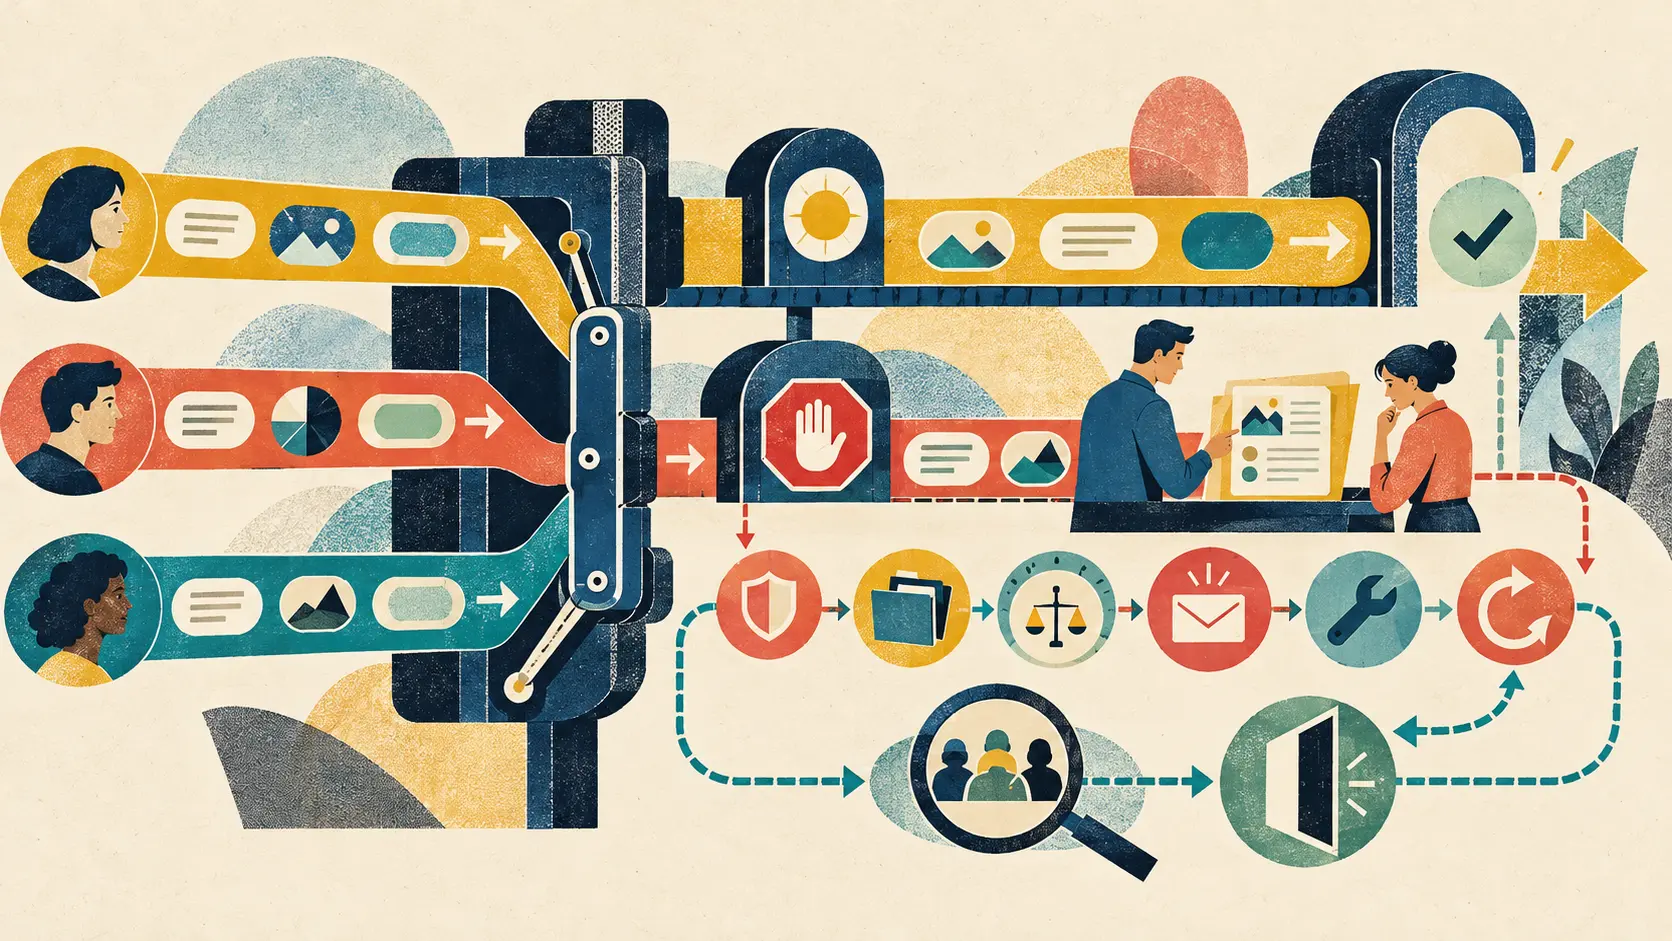
A model gateway offers a practical bargain. Send one request to one interface, then let the service route it to the model that fits the job, budget or latency target. OpenAI is adding a condition to that bargain. In an October 21 announcement, the company said partners that provide access to its models must maintain safeguards consistent with OpenAI's, investigate potential violations and take appropriate action. It also said partners will coordinate enforcement so restrictions remain effective across services that offer OpenAI models. Updated Usage Policies take effect November 20. They say a model-access intermediary, meaning a platform or service that lets third parties directly access OpenAI models, must obtain OpenAI's prior review and approval. An ordinary application that uses a model to power its own features is not covered solely for that reason. That distinction matters. A travel planner that calls a model behind the scenes is not the same thing as a router that sells direct access to several models through one account. OpenAI's goal is understandable. If a customer loses access for serious misuse at one provider, switching the endpoint should not automatically erase the restriction. Safety controls that disappear at the reseller boundary are mostly decorative. But consistent enforcement creates a second problem. A decision made in one place can affect access somewhere else. If that decision is wrong, vague or attached to the wrong end user, consistency can scale the mistake just as efficiently as it scales the safeguard. The plain signal is that a cross-provider restriction needs to travel with an appeal trail. OpenAI says its enforcement decisions are based on documented conduct and risk, applied consistently and proportional to the circumstances. It says restrictions can be revisited when meaningful changes in conduct, commitments or safeguards address the concern. The updated policy page also links to an appeal route for people who think enforcement was mistaken. Those are useful commitments. The October 21 announcement does not, however, publish a full operating protocol for gateway users. It does not specify a common notice format, review deadline, evidence schema, false-positive rate, independent reviewer requirement or method for propagating a corrected decision across every provider that enforced it. That missing machinery is where an appeal either becomes real or turns into customer-support archaeology. Imagine a small security company using a gateway to compare models on malware analysis. One provider flags a burst of requests as suspicious. The account is restricted. Coordinated enforcement prevents the same customer from immediately sending the traffic through another service. Perhaps the restriction is correct. Perhaps a compromised API key is being abused. Perhaps the traffic belongs to a legitimate defensive evaluation. Perhaps the gateway attached several organizations to one shared identifier. The user should not have to guess which story the system believes. Start with a decision receipt. Every restriction should have a stable decision ID, the policy section involved, the service that made the decision, the date, the affected account or pseudonymous end-user identifier, the scope of the restriction and a plain description of the conduct under review. It should say whether the action is a warning, a capability limit, a temporary suspension or a termination. That receipt should avoid exposing detection methods that would make evasion easy. It can still provide enough information for a person to identify a stolen key, a mislabeled workload or a policy misunderstanding. Next, separate the actors. The model provider writes rules and may operate safety systems. The gateway routes requests and controls the customer relationship. A reseller may handle billing and identity. The customer may serve many end users. Each party can see different evidence and control different remedies. A useful notice should name who decided, who enforced and who can fix the underlying problem. Sending a gateway customer to a model provider that cannot see the account record is not an appeal path. Sending the same customer back to a gateway that can only repeat a provider code is not one either. Scope must be equally explicit. A leaked key should not silently become a permanent ban on an entire company. Misuse by one end user should not automatically disable unrelated teams if the gateway can distinguish them safely. A restriction on a powerful cyber capability should not be described as if every ordinary model request were forbidden. OpenAI says it is working with customers on SafetyIDs, identifiers customers can provide to help distinguish individual end users during an investigation without revealing their identities to OpenAI. That could improve precision. It also creates an implementation duty: identifiers must be stable enough to investigate a pattern, separated enough to avoid grouping innocent users and governed so they do not become a shadow identity system. The article announcing consistent standards does not say that SafetyIDs are mandatory for every gateway. It describes them as work in progress with customers. A gateway should therefore document whether it uses them, how they are generated, how long they persist, which services receive them and how a user can correct a bad association. Privacy belongs in the receipt too. OpenAI's separate description of Private Safety Processing says automated systems can return limited safety signals without giving OpenAI personnel access to underlying customer content in certain eligible deployments. Customers keep information in their own systems and may choose to share relevant material when appealing or supporting an investigation. That is a promising direction, but it is not a blanket description of every gateway arrangement. A user needs the actual boundary for the service in front of them: what content is retained, which party can read it, what signal crosses providers, how long it remains available and what extra evidence an appeal will disclose. Do not make a person surrender an entire private workload merely to learn why one request was blocked. The appeal itself needs stages. First comes correction. Let the customer rotate a compromised key, isolate an end user, tighten a tool permission, update a filter or explain a legitimate research context. If a practical safeguard resolves the concern, the system should say what proof is needed. Second comes review. A reviewer should receive the original decision, the evidence available at the time, the customer's response and the policy version that applied. The reviewer should be able to change the result, not merely forward the appeal to the same automated rule. Third comes propagation. If the decision is reversed or narrowed, every participating service that received or implemented the restriction needs a correction. A network that coordinates suspensions but leaves reinstatement to separate tickets is not consistent. It is sticky. Fourth comes measurement. Providers and gateways should publish aggregate figures for warnings, restrictions, successful appeals, median review time, decisions changed after review and accounts restored after a compromised credential was fixed. Sensitive categories can be grouped, but the public should be able to see whether proportional enforcement survives contact with actual cases. False positives are not a reason to abandon safeguards. They are a reason to build safeguards with repair. Gateways can begin before November 20. Map every place a policy decision can originate. Give each event a stable identifier. Preserve the model, policy version, time, customer account, end-user token, relevant safety signal and action taken. Decide which fields can cross organizational boundaries and which must stay local. Test a stolen-key case, a legitimate security-research case, a shared-account mix-up and a reversal that has to reach several providers. Then run the test from the user's side. Can the person understand what happened without opening five tickets? Can they reach the party with authority to change the decision? Can they submit a narrow correction without exposing unrelated data? Does a successful appeal restore access everywhere the restriction traveled? Does the record show who approved the reinstatement? OpenAI is right that direct access through a partner should not create a safety loophole. A model router should not be a laundromat for restricted accounts. The inverse matters just as much. A coordinated safety system should not become an invisible blacklist assembled from unexplained codes and orphaned support cases. Consistency is valuable when it keeps rules from vanishing at the next endpoint. It is dangerous when it makes an error harder to find and slower to reverse. Carry the restriction if the evidence supports it. Carry the receipt with it. And when the decision changes, carry the correction just as far.
01
WHAT ACTUALLY CHANGED
OpenAI announced on October 21 that it is aligning safety policies across services that provide access to its models
The policies apply to direct OpenAI access, partners that host its models and reseller partners
OpenAI says access partners must maintain safeguards consistent with its own, investigate potential violations and take appropriate action
The company says partners will coordinate enforcement so restrictions remain effective across services providing access to OpenAI models
Updated Usage Policies are scheduled to take effect on November 20, 2026
The updated policy requires model-access intermediary platforms that let third parties directly access OpenAI models to obtain prior OpenAI review and approval
An application is not covered by that intermediary requirement solely because it integrates OpenAI models to power its own features
OpenAI says it bases enforcement on documented conduct and risk, uses proportional action and may revisit restrictions after meaningful changes
The policy page provides an appeal route for people who believe an enforcement decision was mistaken
OpenAI says it is developing SafetyIDs to distinguish end users during investigations without learning their identities
02
WHY THIS MATTERS
A restriction that disappears when a user switches providers leaves an obvious safety gap
Coordinated enforcement can also spread a mistaken or overbroad decision across several services
Gateways, model providers, resellers and customers hold different evidence and control different remedies
A clear decision receipt lets a legitimate customer identify compromised credentials, user mix-ups and policy misunderstandings
Proportional scope can isolate one key, user or capability without unnecessarily disabling unrelated work
Pseudonymous end-user identifiers can improve precision but need retention, separation and correction rules
Privacy-preserving safety signals do not remove the need to explain what data each service retains and shares
A successful appeal must propagate as reliably as the original restriction
Aggregate appeal outcomes and review times reveal whether proportional enforcement works in practice
Repairable enforcement makes strong safeguards more credible to legitimate users
03
WHERE IT COULD HELP
- Issue a stable decision receipt for every warning, capability limit, suspension and termination
- Name the policy section, provider, enforcement service, scope, date and available remedy
- Separate provider decisions from gateway enforcement and customer-level remediation
- Use pseudonymous end-user identifiers to avoid grouping unrelated users when the deployment supports them
- Document identifier generation, retention, sharing and correction practices
- Limit evidence sharing to the fields necessary to investigate and review the decision
- Offer a narrow path to rotate a leaked key, isolate an abusive user or add a missing safeguard
- Route appeals to reviewers with authority to change the original result
- Propagate reversals, narrower scopes and reinstatements to every participating service
- Test coordinated enforcement with legitimate security research, compromised credentials and shared-account edge cases
- Publish aggregate restriction, appeal, reversal, review-time and reinstatement metrics
- Version policy rules so an appeal is evaluated against the requirements that applied when the event occurred
KEEP A HAND ON THE WHEEL
OpenAI describes its policy direction and its own enforcement commitments, not an independent audit of gateway behavior. The October 21 announcement does not publish a shared notice schema, evidence format, review deadline, false-positive rate, independent reviewer rule or complete protocol for propagating reversals across providers. SafetyIDs are described as work in progress, and Private Safety Processing applies to eligible deployments rather than every possible gateway arrangement. Watch for the gateway approval process; implementation guidance before November 20; provider-specific data boundaries; notice and appeal service levels; proportional restriction scopes; published reversal metrics; pseudonymous identifier governance; remedies for compromised keys and end-user misuse; and evidence that reinstatement reaches every service that received the original restriction.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on October 22, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US