THE SIGNAL IN ONE SENTENCE
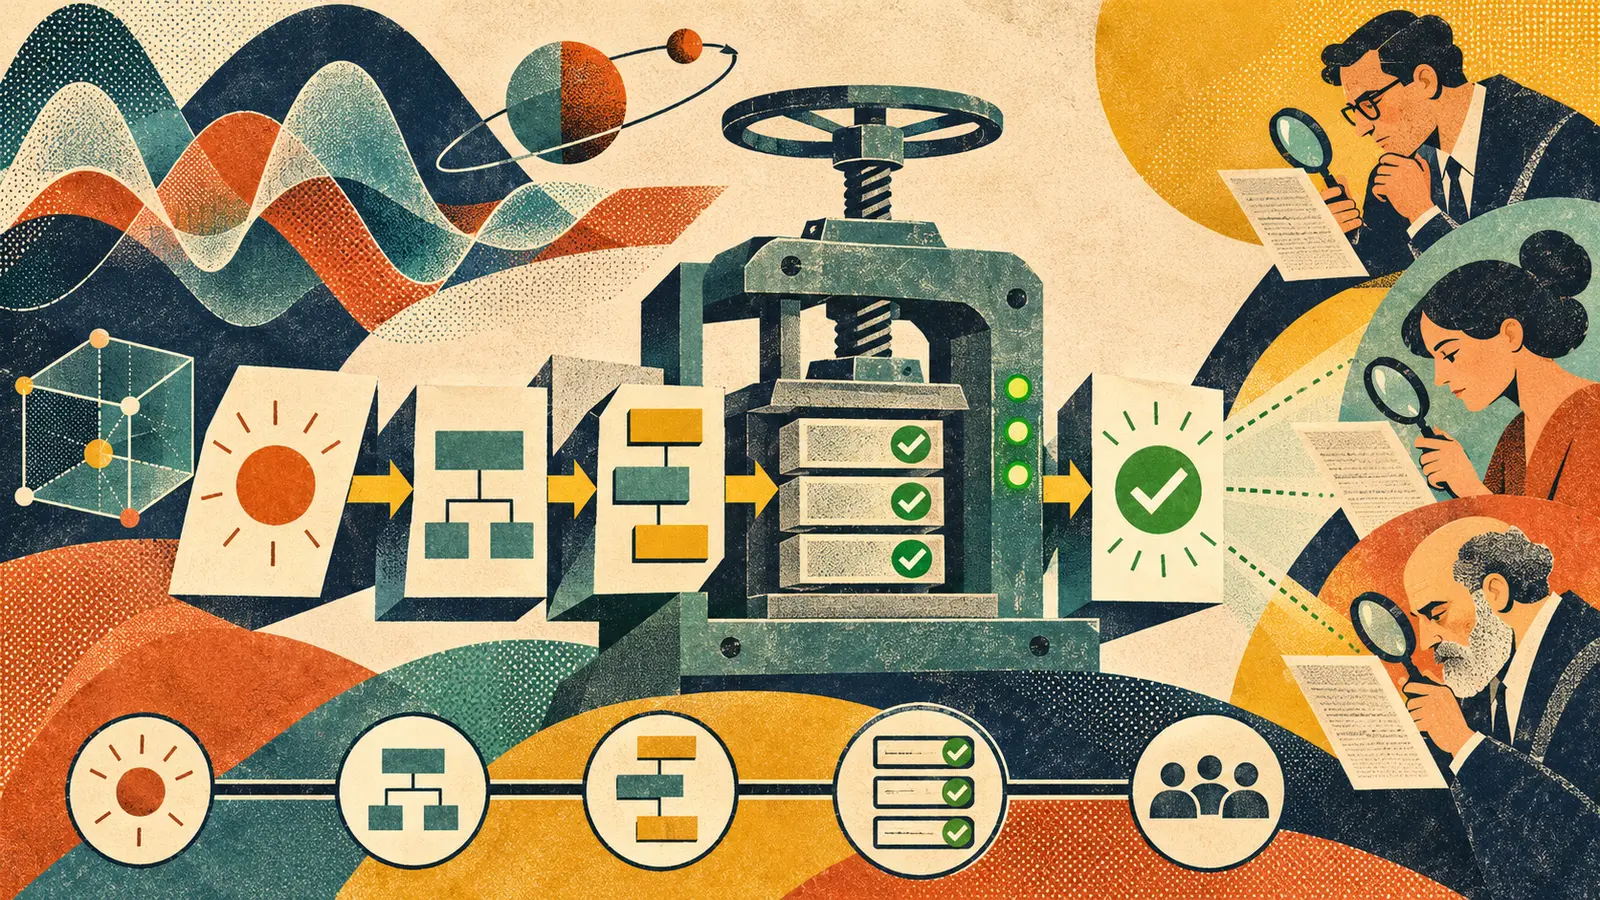
A computer-assisted proof should not arrive as a magic trick with a green check mark at the end. It should arrive with a receipt. Physical Superintelligence, or PSI, reported on November 6 that its internal research system produced a complete proof of the Aaronson-Ambainis conjecture, a mathematical problem introduced in work by Scott Aaronson and Andris Ambainis and open since 2008. The conjecture lives in the theory behind quantum computing. Very roughly, it says that a bounded, low-degree polynomial cannot depend meaningfully on many inputs while every individual input remains almost irrelevant. At least one variable must have noticeable influence. That sounds like a specialist puzzle because it is one. It also supports a larger question: when can a quantum algorithm gain an enormous advantage over a classical one? Aaronson and Ambainis showed that their conjecture would constrain certain routes to exponential quantum speedups in the black-box setting. PSI says its system worked on the problem during a three-day run and found a complete proof on the third day. The system used instances of a non-public Anthropic model inside PSI's own research environment. David Turturean led the work, built and ran the system, reviewed the result and takes responsibility for its correctness. PSI says Jim Halverson audited the proof, Phiala Shanahan commented on the Lean formalization, and researchers at Stanford have been reading it and are preparing a shorter expert exposition. The team also released the proof, paper and Lean code in a public repository under an Apache 2.0 license. The repository says the formal development is complete, contains no placeholders and adds no new axioms. PSI reports that Lean accepted the proof and that two independent Lean kernel implementations rechecked it. That is a serious evidence package. It is not the same thing as universal mathematical agreement. Lean checks whether the formal proof follows from the formal statement, definitions, imported library and accepted logical foundations. It does not check whether the formal statement perfectly captures every informal intention, whether the literature review found every prior result, whether a theorem deserves its claimed historical importance or whether the proof changes practical quantum computing next Tuesday. A human mathematician still has to ask the annoying and essential questions. Is this the right theorem? Is the statement strong enough to resolve the original conjecture? Are the assumptions ordinary and visible? Does the argument reveal a reusable idea? Did someone else publish the result first? What does it actually change? This is why the proof receipt matters. Keep the original conjecture beside the formal statement. Name the exact model and research system as far as disclosure allows. Preserve prompts, intermediate attempts and tool traces when they exist. Pin the Lean and mathlib versions. List the axioms. Run more than one kernel. Record who reviewed which layer. Invite independent experts to attack the statement and exposition. Keep corrections public. The glamorous claim is that an AI system helped solve a long-standing problem. The durable result is an inspectable chain from old question to formal theorem to proof object to kernel check to human mathematical judgment. That chain will not make every proof correct. It will make disagreement much more useful. And in mathematics, useful disagreement is how the green check mark earns its keep.
01
WHAT ACTUALLY CHANGED
PSI released a claimed proof of the Aaronson-Ambainis conjecture and the artifacts needed to inspect it. The conjecture originated in work by Scott Aaronson and Andris Ambainis on the structure required for quantum speedups. Their paper connected a statement about influential variables in low-degree polynomials with limits on how far certain quantum query algorithms can separate themselves from classical algorithms on most inputs. PSI's theorem gives an explicit lower bound on the influence of at least one variable. In the notation used by the project, the bound is proportional to epsilon raised to the five-halves power divided by the sixth power of the degree. The important point for non-specialists is that the influence cannot vanish arbitrarily fast. A polynomial relationship exists.
The project describes a mixed machine and human research process. PSI says an internal system used instances of a non-public Anthropic model and reached a complete proof during the third day of a run. The public report does not make that entire system reproducible. It does name the human lead, the internal audit and the external experts reviewing the result. That distinction matters. Saying an AI proved a theorem compresses several jobs into one sentence. A model can propose lemmas and proof steps. A research system can search, test and package them. Lean can verify a formal derivation. Humans choose the problem, interpret the claim, audit the formalization, connect it with the literature and accept responsibility.
The proof is accompanied by a complete Lean formalization. Lean is a proof assistant. It translates a theorem into precise objects and checks each permitted inference. The public repository says the development has no placeholders and introduces no extra axioms. PSI also reports that two independent Lean kernels rechecked the proof. Independent kernels reduce the chance that one checker implementation silently accepted an invalid proof. They do not remove every trust assumption. Users still depend on the theorem statement, definitions, library, compiler path and the foundations that Lean permits. The receipt should expose those boundaries instead of treating verified as a synonym for infallible.
Independent mathematical review is still underway. PSI reports that Guy Blanc, Jordan Docter, Carmen Strassle and Li-Yang Tan at Stanford have been reading the proof, sent comments and are writing a shorter expert exposition. That is encouraging because a formal proof and a readable proof serve different purposes. The formal object establishes a checkable derivation. The exposition helps mathematicians understand the central idea, compare it with earlier techniques, find fragile interpretations and decide where the method might travel next. A proof can be formally accepted and still need a great deal of human explanation before a field knows what it has learned.
02
WHY THIS MATTERS
For mathematicians, the release offers something better than a screenshot of a successful run. The public code lets specialists inspect definitions, dependencies and proof structure. They can challenge the correspondence between the informal conjecture and the formal theorem. They can attempt shorter arguments, test alternate assumptions and identify which lemmas contain the real idea. That is how a machine-assisted result becomes part of mathematics rather than a product demonstration with unusually stern punctuation.
For quantum computing, the result clarifies a theoretical boundary rather than delivering a new machine. The original Aaronson-Ambainis work asks when quantum algorithms can achieve dramatic query advantages over classical methods. Resolving the conjecture strengthens that line of theory. It does not produce a faster chip, a new error-correcting code or an immediate quantum advantage for a commercial workload. Readers should celebrate the theorem at the scale of a theorem. Quantum computing has enough fog machines already.
For AI research, the process suggests that formal domains can support unusually strong verification loops. A model can generate an argument, but a proof assistant can reject steps that do not follow. That creates a feedback signal much sharper than a human preference score or a plausible-looking paragraph. The model still may formalize the wrong claim, import a surprising assumption or find a proof no one understands. The checker makes one layer rigorous, not the whole scientific story.
For research institutions, responsibility remains human even when contribution becomes distributed. The PSI report names who scoped and ran the work, who audited it, who commented on formalization and who is conducting external review. That is a useful pattern. Institutions should resist the temptation to assign all credit to the machine when a result succeeds and all blame to a person when it fails. Authorship and accountability need contribution records precise enough to survive both marketing and correction.
For everyone publishing machine-assisted science, the release raises the expected standard of evidence. A consequential claim should travel with source material, machine-readable artifacts, versions, assumptions, checks, named reviewers, known limitations and a correction path. Not every field has a proof kernel. Every field can still publish a receipt that shows what was measured, what was inferred, what was checked and what remains uncertain.
03
WHERE IT COULD HELP
- Publish the exact target statement before the proof. Preserve the original wording, the formal theorem and a plain-language map between them so reviewers can find mismatches.
- Record the research system. Name the model, model version, orchestration, tools, search strategy, run dates, compute limits and any hidden components that prevent reproduction.
- Preserve the run artifacts when policy and privacy allow. Keep prompts, intermediate lemmas, rejected attempts, tool calls and the final packaging step instead of saving only the successful ending.
- Pin the formal environment. Record the Lean version, mathlib commit, dependencies, build commands and hardware or container details needed to reproduce the check.
- Audit the trust boundary. List imported axioms, unsafe features, opaque definitions, generated code, compiler assumptions and any part that a kernel check does not cover.
- Use independent checkers. Re-run the proof with separate kernels or trusted builds and publish the resulting hashes and logs.
- Separate verification roles. Assign reviewers to the formal statement, proof object, mathematical exposition, prior literature, significance claim and reproducibility package.
- Write a human exposition. Identify the central idea, explain why older approaches stalled, show which steps are new and mark where the formal proof is doing work that prose tends to hide.
- Invite adversarial review. Offer a clear channel for counterexamples, statement mismatches, missing citations and build failures, then keep corrections and version history public.
- Carry the receipt into downstream claims. If a paper, lecture, model card or product uses the theorem, link the exact version and distinguish the proved result from broader interpretation.
KEEP A HAND ON THE WHEEL
The primary announcement comes from PSI, the organization that built the research system and released the proof. Independent expert review is in progress, and the result has not yet completed the ordinary cycle of journal publication and broad community scrutiny. Watch for a shorter expert exposition, independent reproductions, citations to any related prior work and corrections to the formal or informal statement. The underlying Anthropic model is described as non-public, and PSI's internal research system is not fully reproducible from the released repository. The proof artifacts can be checked even when the discovery process cannot be replayed. Those are different forms of reproducibility and should not be blended into one claim. Lean acceptance is powerful evidence about a formal derivation. It does not prove that the formal statement exactly matches the historical conjecture, that all definitions carry the intended meaning, that the imported library is free of defects or that the theorem has the claimed significance. Watch for explicit statement correspondence and a documented trust boundary. The absence of added axioms and placeholders is important. It is not the same as having no assumptions. Every formal system rests on foundations and libraries. Watch for a machine-readable axiom report, pinned versions, reproducible builds and independent kernel logs. Credit can become muddy when models, system builders, proof assistants and mathematicians all contribute. Watch for contribution statements that name problem selection, system design, prompting, proof discovery, formalization, code review, mathematical audit, exposition and responsibility. A vague AI did it story erases both the people and the technical mechanism. Finally, resist practical overreach. This theorem concerns computational complexity and the structure behind possible quantum speedups. It does not make today's quantum computers faster, prove that quantum advantage is impossible or settle every separation between quantum and classical computation. The result deserves attention without borrowing consequences it has not earned.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on November 8, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US