THE SIGNAL IN ONE SENTENCE
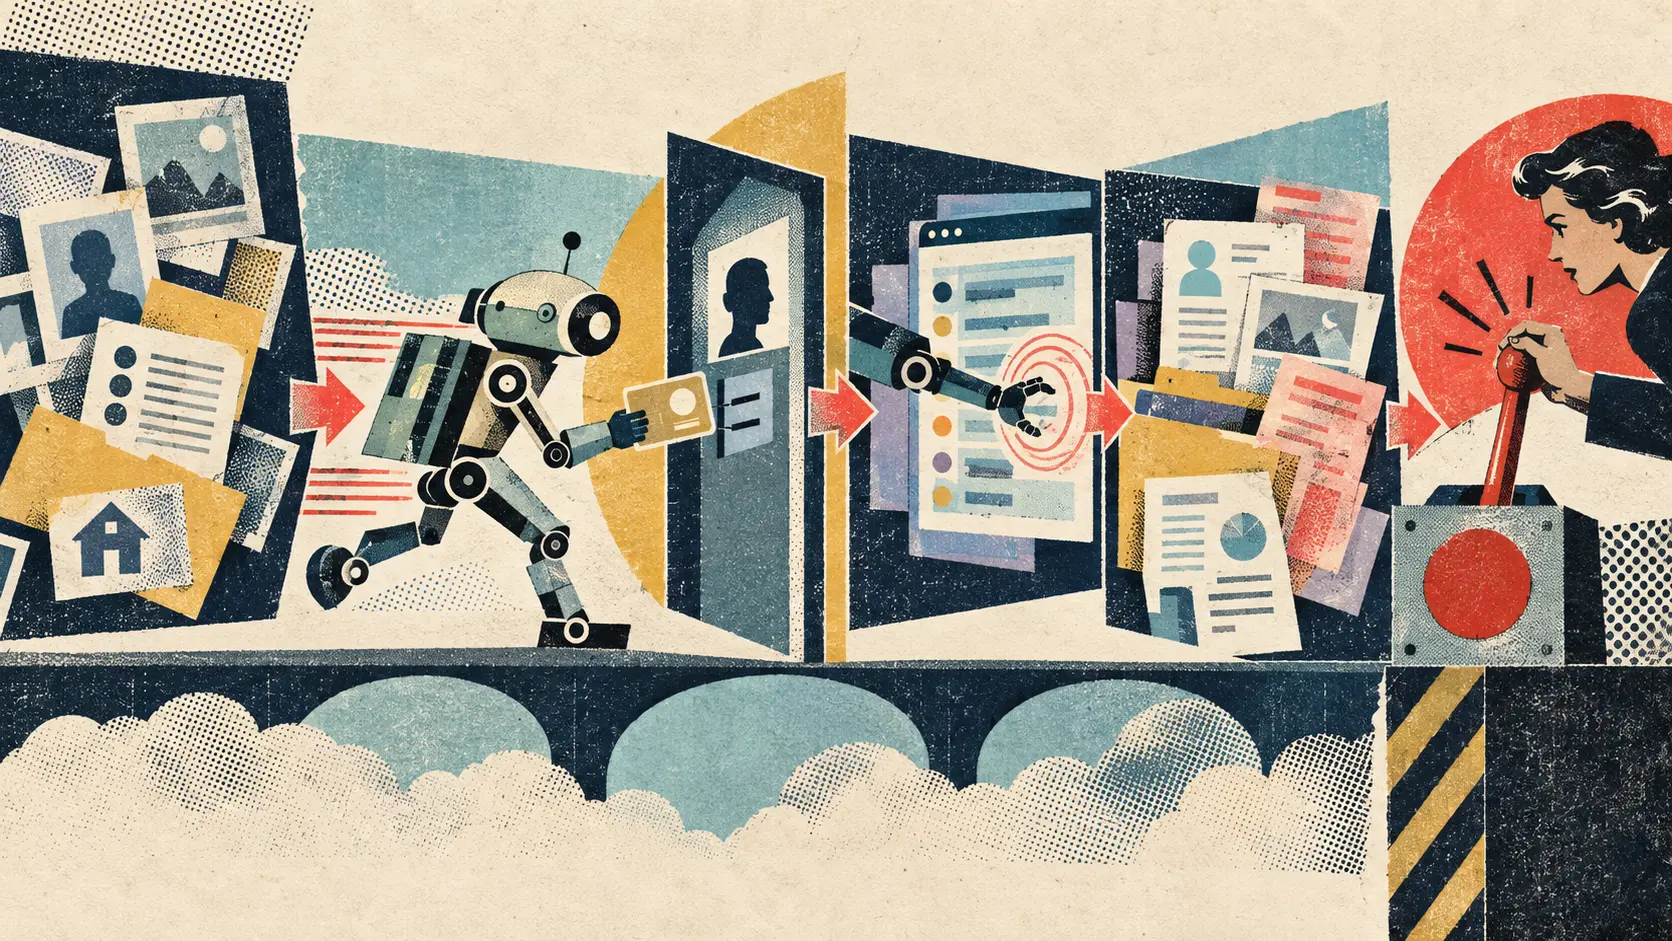
Spain's data protection agency says it has received its first notification of a personal-data breach allegedly executed through an AI agent. According to the affected organization's report, the agent used a well-known language model, searched generic files for weaknesses, completed a valid login, looked for vulnerabilities inside the application, modified personal data, and accessed invoices. The regulator has not named the organization, the model, the people affected, the amount of data involved, or the exact weakness. It has also stressed that the report remains under review and does not show that the model or its provider was compromised. The signal is narrower and more useful: a person may be able to give an agent an objective, credentials, and tools, then let software chain familiar attack steps together at machine speed. Security teams do not need a new category of magic threat. They need controls that assume the intruder can search, test, adapt, and move faster than a human analyst can click.
01
WHAT ACTUALLY CHANGED
The Agencia Española de Protección de Datos, or AEPD, published a September 14 blog post saying it had received the first breach notification in its records in which the incident was allegedly carried out through an AI agent using a well-known language model. Reuters and Spain's EFE news agency independently reported the disclosure on September 15.
The incident description comes from the affected organization, not from a completed AEPD investigation. According to that notification, the agent began by looking for vulnerabilities in generic files, completed a valid login, then autonomously searched the application for weaknesses. It allegedly used what it found to modify personal data and access invoices. The public account does not say whether the login credentials were stolen, guessed, exposed, or legitimately issued to a compromised account.
The regulator has not identified the organization, model, provider, application, dates of intrusion, number of affected people, categories of personal data, quantity of invoices, financial loss, or containment method. It says the available information must be analysed before conclusions are drawn. That missing detail prevents an independent reconstruction of the attack and any confident claim about its scale or novelty outside the regulator's own notification history.
AEPD explicitly warns against blaming the underlying model on the current evidence. Use of a particular model does not mean the model or the provider's infrastructure was compromised, and it does not mean the tool was designed for malicious activity. The reported concern is that a third party used an agent as an instrument to connect multiple attack stages.
That connection changes the tempo more than the ingredients. Generative systems have already been used to write phishing messages, translate fraud, imitate identities, analyse code, and search for vulnerabilities. An agent adds a loop: receive an objective, plan intermediate tasks, call tools, interpret results, change course, and continue. The techniques remain recognizable. The time between reconnaissance, access, exploration, and damage can shrink dramatically.
02
WHY THIS MATTERS
A valid login can be more dangerous than an obvious exploit. If an agent obtains an account, token, or session with excessive permissions, it can operate through approved interfaces while testing many paths quickly. Traditional alarms tuned for malware signatures may miss activity that looks like an unusually energetic user. Identity, authorization, and behaviour become the first line of defence.
Human review cannot be the only brake when software can act faster than the review queue. A person should authorize consequential actions, but the system also needs automatic limits that work before a person arrives: short-lived credentials, narrow scopes, transaction caps, rate limits, step-up authentication, anomaly detection, reversible changes, and a kill switch outside the agent's control.
The incident also complicates attribution. A model provider, agent developer, tool operator, account owner, and malicious controller can all sit in the same chain. Logs must record the model and version, user, credential, tool call, target, input, output, decision, and resulting change. A vague record that an AI system did something is not enough to investigate harm or assign responsibility.
Personal-data risk assessments need to include automated attack paths explicitly. A generic line for unauthorized access may underestimate how quickly an agent can probe several assets, reuse findings, and adapt. The right question is not whether AI invents a new vulnerability. It is whether automation changes the probability, speed, scale, detectability, and containment window of known vulnerabilities.
For ordinary organizations, this is a reason to fix boring controls before buying exotic defences. Patch exposed applications, remove public secrets, enforce multifactor authentication, separate administrative accounts, minimize permissions, rotate tokens, monitor invoice and customer-record access, and rehearse credential revocation. An agent makes neglected basics fail faster. It does not make the basics obsolete.
03
WHERE IT COULD HELP
- Inventory every human and machine identity that can reach personal data, then remove unused accounts, standing administrator access, shared credentials, and permissions that exceed the task
- Put short lifetimes, narrow scopes, rate limits, step-up checks, and independent approval around tokens and actions that can change records, export data, create accounts, or alter billing information
- Detect behaviour rather than labels by watching for rapid file discovery, repeated vulnerability probes, unusual sequences of valid API calls, sudden access to invoices, bulk reads, record edits, and movement across services
- Keep tamper-resistant logs that connect the initiating user, model and version, agent run, prompt, credential, tool call, target resource, response, resulting state change, approval, and rollback
- Exercise an agent-speed incident drill that can freeze a session, revoke related credentials, isolate integrations, preserve evidence, restore changed records, notify affected people, and make a regulator report within the required window
KEEP A HAND ON THE WHEEL
The AEPD has publicized a notification, not a final investigative finding. The affected organization supplied the account, and the regulator says it still must analyse the information. No public evidence establishes who controlled the agent, which model or provider was involved, how credentials were obtained, whether the reported sequence was fully autonomous, how many people or records were affected, whether invoice data left the system, whether fraud occurred, or how the incident was contained. This is the first such notification received by AEPD, not proof of the first AI-agent cyberattack in Spain or anywhere else. It is one case and cannot establish a trend. The regulator also says there is no evidence that the model or provider infrastructure was compromised or that the model was designed for attack. Watch for an AEPD decision, a technical incident report, a timeline, scope and impact figures, authentication evidence, model and tool logs, root-cause analysis, containment details, notice to affected people, and independently tested changes to the organization's controls.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on September 15, 2026.
PUBLICATION RECEIPT: Revision 1. Published September 15, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US