THE SIGNAL IN ONE SENTENCE
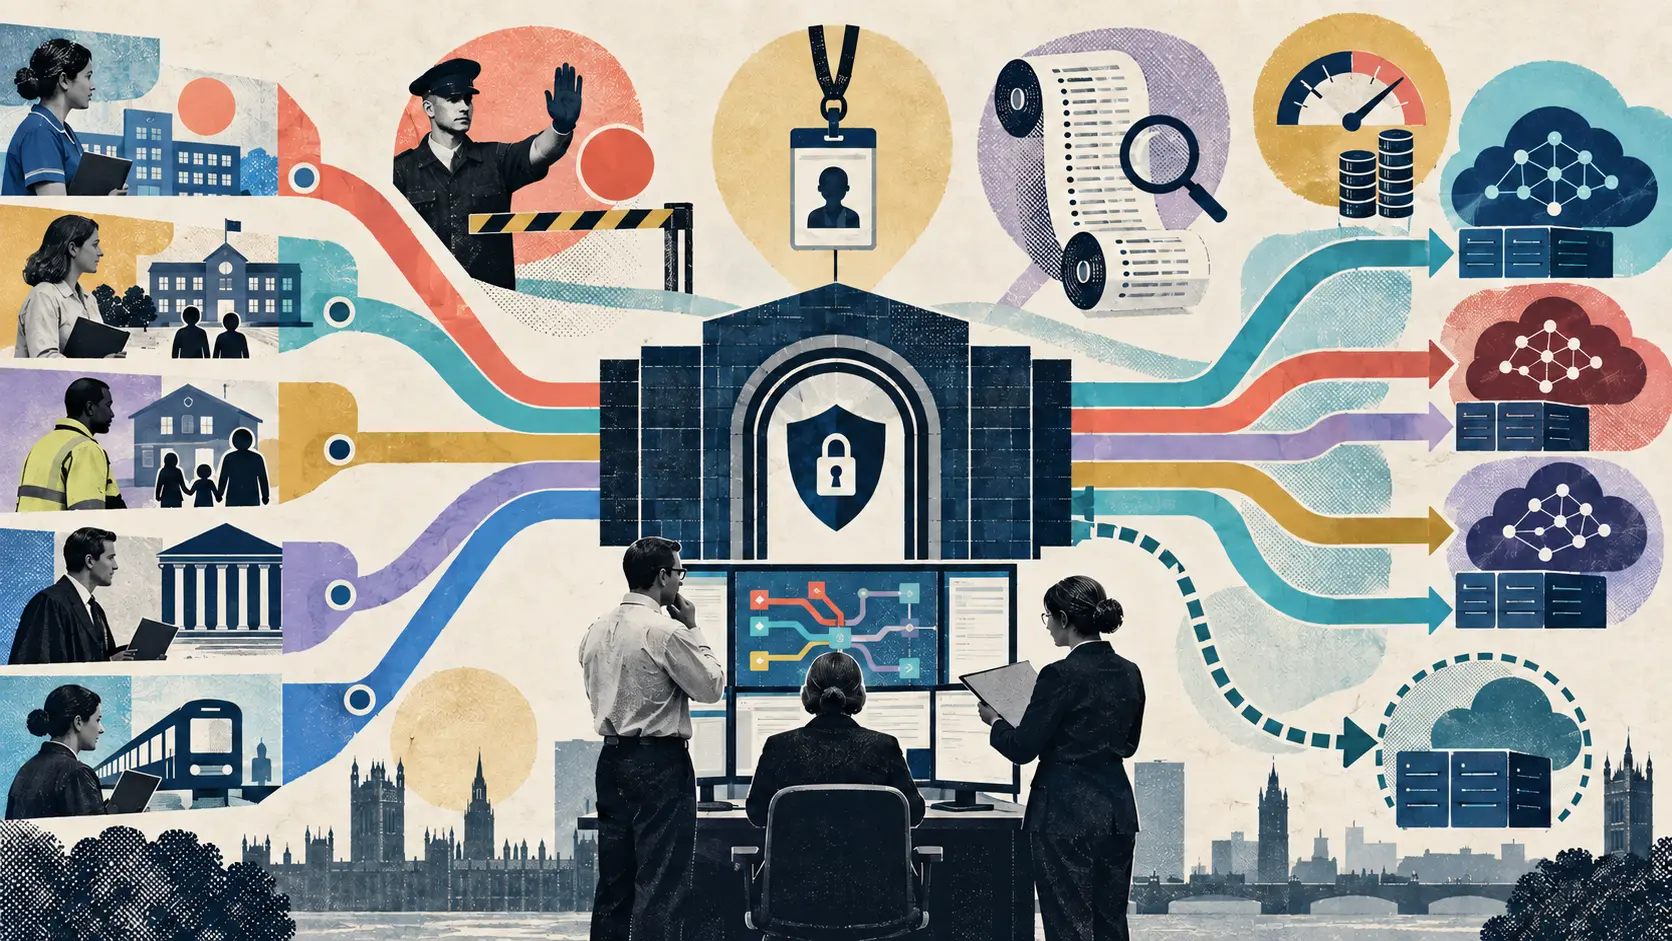
The UK Ministry of Housing, Communities and Local Government has built a shared AI Gateway for its own digital teams. Instead of every service connecting separately to an AI vendor, developers, data scientists, and applications can use one departmental route to approved models. The ministry says the gateway is built around Microsoft Azure API Management, works with services running in Azure and AWS, and now provides access to approximately 20 models. It is meant to put authentication, role-based access, model approval, monitoring, audit records, support, and cost visibility in one place. That is useful plumbing, not a safety certificate. A gateway can make common rules easier to enforce and evidence easier to collect, but it also concentrates permissions, prompts, logs, spending data, and operational dependence. The real test is whether the department can show which model handled a request, what data it received, why that route was allowed, who can inspect the record, how failures are contained, and what happens when the central gate is unavailable.
01
WHAT ACTUALLY CHANGED
On September 15, the Ministry of Housing, Communities and Local Government published a technical account of its AI Gateway. The department says it created the platform because separate teams were otherwise building their own integrations, governance processes, and support arrangements, which duplicated effort and produced inconsistent standards.
The ministry says Microsoft Azure API Management is the core platform. The gateway is designed to be provider-agnostic, so approved models from multiple providers can sit behind a common interface and new providers can be added later. Applications and services running in both Azure and AWS can use it. That is a departmental architecture choice, not evidence that every UK public service or local council now uses the gateway.
The shared route gives teams a standard API, common onboarding, and centralized technical controls. The department says it can restrict access to approved vendors and models, apply security controls, monitor use, support audits, and track consumption and cost. A shared gateway does not evaluate every answer automatically. It creates one place where the department can put and inspect those controls.
MHCLG says the platform passed its internal AI approval process, specialist technical and data-protection approvals, and a penetration-testing assessment. It also says the service uses authentication, role-based access control, existing monitoring and logging, commercial contracts, cyber assurance, acceptable-use rules, operational responsibilities, data-handling guidance, and the department's AI Register. No public report currently shows the test methods, findings, unresolved weaknesses, or remediation evidence.
The department says multiple teams have adopted the gateway, several initiatives are using it, more teams are onboarding, and approximately 20 AI models are available through the platform. It does not name the initiatives, publish the complete model and provider list, quantify traffic or cost savings, describe incidents, or measure effects on staff and residents. The adoption figures therefore describe the department's present account of the service, not an independently audited result.
02
WHY THIS MATTERS
A gateway turns scattered model access into a control plane. If every team connects directly to a provider, policies can diverge, credentials can sprawl, and nobody may have a complete view of cost or use. One route can enforce a common identity check, approved-model list, request limit, logging rule, and shutdown decision. That is especially valuable in government, where the same basic safeguards should not depend on which project happened to buy an API first.
Centralization also creates a larger blast radius. A mistaken policy, compromised administrator, routing error, unavailable gateway, or exposed log can affect many services at once. The department needs tested isolation between teams, narrow permissions, protected administrative access, independent monitoring, rollback, provider failover, and a route for essential services to degrade safely. A single front door is easier to guard only if the building has fire doors behind it.
Model approval should attach to the exact route, not just a vendor name. Different versions can have different capabilities, retention rules, regions, safety behaviour, prices, and failure patterns. A useful register records the model and version, provider, hosting region, approved purpose, allowed data class, retention setting, evaluation evidence, responsible owner, and review date. If the gateway silently changes the destination, the audit trail should show that change.
Logging creates evidence and a new privacy boundary at the same time. Prompts and responses may contain case details, addresses, financial circumstances, planning records, complaints, or staff notes. The department should log enough to reconstruct a decision without collecting an unnecessary second copy of sensitive material. Redaction, access limits, retention periods, tamper resistance, and tested deletion matter as much as turning logging on.
The public value is not the existence of an API layer. It is whether services become more reliable, understandable, affordable, accessible, and correct. Technical teams can measure onboarding time, blocked requests, cost, latency, incidents, and failover. Public-service owners also need measures for error severity, human review, appeals, exclusion, staff workload, resident outcomes, and whether an affected person can learn that AI shaped a decision and challenge it.
03
WHERE IT COULD HELP
- Maintain a live route register that names the exact model and version, provider, hosting region, approved service and purpose, permitted data class, retention rule, evaluation evidence, cost owner, review date, and tested fallback
- Give every service its own identity and least-privilege permissions, then separate model access, log access, policy changes, key rotation, and emergency shutdown so one compromised account cannot control the whole gateway
- Classify and minimize data before a request leaves the service, redact unnecessary personal information, reject prohibited fields, and record why the selected model was allowed to receive what remained
- Make logs useful without turning them into a shadow case-management system by defining captured fields, redaction, access, retention, deletion, tamper protection, resident-access rights, and a process for correcting a misleading record
- Exercise failures on purpose: disable a provider, revoke a model, corrupt a route, overload the gateway, lose a region, and compromise an administrator, then prove that services fail safely, investigators can reconstruct events, and teams can restore a known-good configuration
KEEP A HAND ON THE WHEEL
The evidence here is a department-authored technical account. It establishes the stated architecture, approval path, approximately 20 available models, and adoption by multiple internal teams, but not an independent security or privacy assessment. The ministry has not published its penetration-test scope or findings, unresolved risks, service-level objectives, uptime, incident history, traffic, model and provider inventory, data-flow map, prompt-retention rules, log-access matrix, privacy impact assessment, procurement terms, total cost, realized savings, failure tests, or resident outcomes. The gateway belongs to MHCLG. The announcement does not establish use across the whole UK government, local authorities, or every public service. Provider-agnostic design does not prove quick substitution, and central controls do not prove that every model output is accurate, fair, lawful, or reviewed. Watch for a public model register, architecture and data-flow diagrams, evaluation records, independent testing, incident disclosure, resilience exercises, cost evidence, named service use cases, and measures showing what changed for staff and residents.
04
TERMS WORTH KEEPING
OPEN GLOSSARY CARD
Permission scope
The specific systems, records, fields, users, and actions that an account or software connection is allowed to access.
OPEN GLOSSARY CARD
Audit log
A timestamped record of system activity used to review who accessed information, what a tool did, and which action was approved.
OPEN GLOSSARY CARD
Model routing
The service decision that maps an API request or product name to the specific model that will handle it.
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on September 15, 2026.
PUBLICATION RECEIPT: Revision 1. Published September 15, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US