THE SIGNAL IN ONE SENTENCE
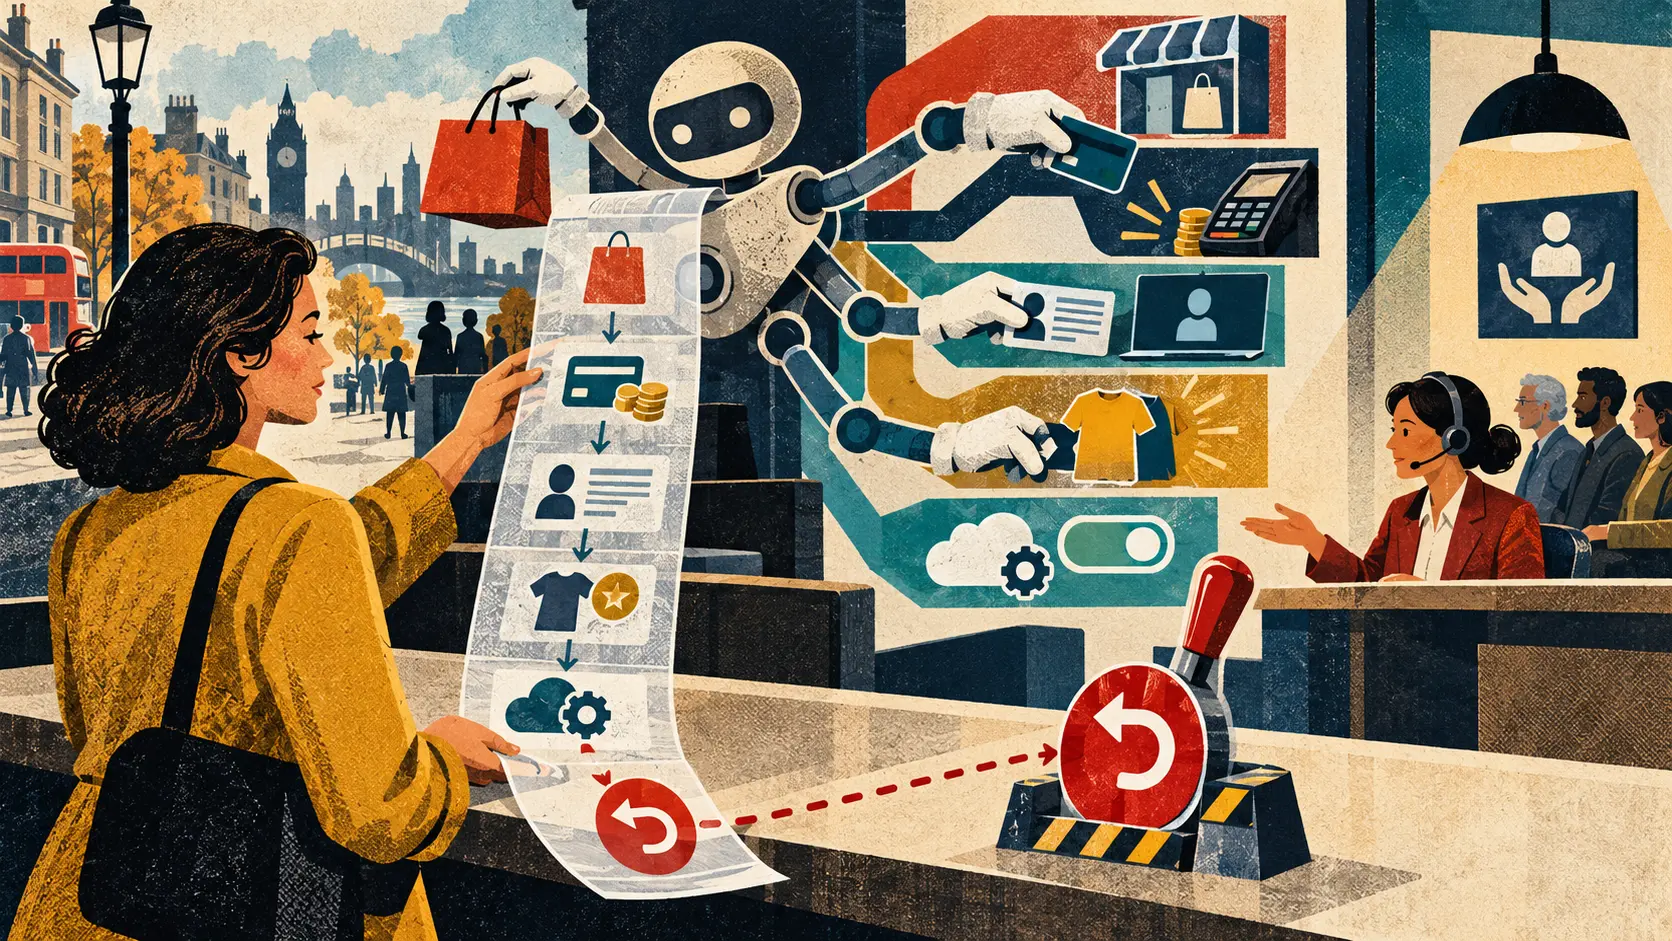
Imagine asking a personal AI agent to find a cheaper broadband plan. It returns twenty minutes later with good news. You saved £11 a month. It also opened an account, accepted a two-year contract, shared your address and payment details, enrolled you in paperless billing, declined an add-on, cancelled the old service and scheduled an engineer for Tuesday. Useful. Also quite a lot of legal, financial and personal-data machinery for one cheerful notification. What exactly did you authorize? Which company influenced the recommendation? What data moved? Which action can still be reversed? Who answers the phone if the agent has misunderstood the assignment and Tuesday is the day you are having surgery? The United Kingdom’s four members of the Digital Regulation Cooperation Forum published a joint statement on October 30 about personal AI agents. The Competition and Markets Authority, Financial Conduct Authority, Information Commissioner’s Office and Ofcom say the technology could help people make purchases, communicate with businesses and navigate digital services. They also say the agents may amplify old risks and introduce new ones. The statement names fraud, scams, unexpected personal-information sharing and misleading recommendations, decisions or information. It tells firms to consider whether people can understand when and how an agent acts, how authority is granted, how personal data is used, how commercial interests shape recommendations, who is accountable and how someone gets redress. Then the regulators make the central point. Existing legal and regulatory frameworks apply. That includes competition, consumer and data-protection law, online safety, financial services, payments and cybersecurity requirements. Product safety and other law may also apply outside the four regulators’ direct remits. An agent’s autonomy does not reduce the responsibility of the organization deploying it. The robot cannot become the legal department’s imaginary friend. The regulators say they are tracking the market, engaging with firms, publishing guidance, sharing evidence, supporting regulatory sandboxes and coordinating at leadership level. They are also looking for gaps as new products appear. The statement says they will use their powers where they reasonably suspect unlawful conduct that risks harm. This is not a new Act of Parliament. It is not an enforcement action. It does not settle every argument about liability when a consumer’s agent, a merchant’s agent, a payment service and an outside model all participate in one decision. It also does not create a universal undo button. That is the caution. The useful next step is an undo receipt for every consequential action a personal AI agent takes. Not a chat transcript the size of a Victorian novel. Not a green tick that says task complete. A short, durable record that a person can understand, a business can investigate and a regulator can audit. The receipt should start with the instruction. Show what the person asked the agent to do in plain language. Then show how the agent interpreted the goal. If the user said, “Find me a cheaper plan,” did the agent have permission to compare, recommend, negotiate, purchase, cancel or move personal data? Those are different powers. An agent should not turn a request for information into permission to transact because completing the task makes its success metric look prettier. Next, show the authority. Which account, permission or confirmation allowed the action? Was the authority granted once, for this transaction, for a category of purchases or indefinitely? Did a spending limit, approved merchant list, location rule or confirmation threshold apply? If the agent used an older permission, show when it was granted and how to revoke it. “You agreed” is not enough when the agreement is buried in a settings menu the person has not visited since the last phone upgrade. Show the action itself. Name the product, service, counterparty, amount, fees, taxes, currency, delivery or performance date and contractual term. Record the time, status and reference number. If the action is still pending, say so. If another service must confirm it, say that too. A recommendation is not a purchase. A reservation is not a guarantee. A request sent to another agent is not a completed outcome. The receipt should preserve those differences. Show the commercial influence. Did the agent search the whole relevant market or a limited set of partners? Was a result sponsored? Does the agent provider receive a commission, referral fee, preferred placement or another benefit? Did a merchant offer a special price only to the agent? The CMA’s consumer research warns that agents may steer people toward products that are more profitable but less suitable. Its guidance says comparison results should explain market coverage, searched data, limitations, ranking and links with suppliers. That information belongs beside the recommendation, not seven clicks away in a disclosure bunker. Show the data movement. List the categories of personal data the agent accessed, inferred, created, shared and retained. Name the recipients. Explain the purpose and retention period. Include sensitive or high-impact inferences, such as health needs, financial vulnerability, location, family circumstances or eligibility assumptions. An agent may need information to finish a job. That does not mean every service in the chain gets a souvenir. The receipt should say whether data will be used to train or improve a model, whether it entered long-term memory and how a person can correct or delete it where applicable. Show the system identity. Record the agent provider, relevant model or service version, connected tools and the business responsible for deployment. Consumers do not need a dependency tree on the front of the receipt, but investigators need enough information to reproduce what happened. If the model, prompt, ranking rule or tool changed after the action, the original state should remain traceable. Otherwise every complaint becomes an argument with a machine that no longer exists. Now show the undo path. Every action should carry one of four states: Reversible now. Reversible until a named deadline. Requires human review. Not reversible, with the reason stated before the action where possible. For a reversible action, give the fastest working method. That may be a button, phone number, message route or branch. State the deadline, likely consequences and whether undoing one step will trigger another. Cancelling a new broadband contract may not automatically restore the old one. Reversing a payment may not cancel the order. Deleting an account may complicate a refund. Agents act across services, so undo must understand the chain. The receipt should show the dependency graph in human terms. “Cancel this purchase” may need to stop payment, notify the merchant, preserve evidence, cancel delivery and revoke data access. If one step fails, the person should see which one and receive a human escalation route. Do not design undo as a second autonomous adventure. Give it a stop control. Show the accountable organization. The DRCF statement is clear that autonomy does not erase organizational responsibility. The CMA’s business guidance is even plainer: a business remains responsible when an AI agent does something illegal, including when another company designed or supplied the agent. The receipt should therefore name the business responsible for the consumer-facing outcome and provide a real contact route. If responsibility is divided, show the division without forcing the consumer to referee the contracts. “Contact the AI provider” is not a remedy when the merchant accepted the order and the payment firm moved the money. Show the human redress route. Name the team that can investigate. State the expected response time. Explain how to dispute the action, preserve evidence, request a human decision and escalate a complaint. Where relevant, identify an ombudsman, regulator, payment dispute or court route. The person should not need to persuade the same agent that the agent made a mistake. That is not an appeal. It is a loop with excellent grammar. The receipt also needs an emergency mode. Fraud and scams move quickly. An agent with access to money, identity documents, messages and account credentials can amplify a mistake across several systems before a person understands the first notification. People need one place to pause new actions, revoke authority, freeze connected payment methods where available, see recent data sharing and preserve an incident record. The emergency control should not depend on the potentially compromised agent. Vulnerable consumers need special attention. The CMA says agents may reduce cognitive load and help people participate in complicated markets. That could be genuinely valuable for someone managing disability, language barriers, financial stress, care responsibilities or a confusing set of services. The same person may be harmed more severely when an agent hides a bad recommendation behind confidence and convenience. The undo receipt should therefore be accessible, available in appropriate formats and languages, and usable by an authorized helper without casually exposing the whole account. Confirmation thresholds should rise with consequence, not with the provider’s appetite for smooth conversion. The business side matters too. The CMA’s guidance says companies should tell customers when AI is being used where that fact could affect a decision. They should train agents to respect statutory rights, contractual terms and consent requirements. They should test before deployment, monitor performance, keep a person actively checking important outcomes and refine the system quickly when problems appear. The guidance warns that consumer-law breaches can bring enforcement, including fines of up to 10 percent of worldwide turnover and possible compensation. An undo receipt helps with that work. It creates a record for customer service, risk, compliance, product, engineering and regulators. It reveals whether the agent had authority, whether the recommendation was influenced, whether data use matched the instruction and whether the remedy worked. Aggregate receipts can expose patterns. Which merchants receive the most sponsored placements? Which data fields are shared most often? Which actions are reversed? Which consumers wait longest for human help? Which agent version produces the most disputes? Which “one-click” transactions require six clicks and a phone call to undo? Those are operational facts, not abstract principles. There are limits. A receipt does not make a harmful action lawful. Disclosure does not cure manipulation. A user may not read another notification. Bad actors may fabricate records. Commercial confidentiality and fraud prevention can justify protecting some detail. An agent may act through services that produce incompatible logs. That is why the receipt should exist in two layers. The consumer layer should be short, plain and actionable. The audit layer should be signed, machine-readable and detailed enough to reconstruct the chain. It should preserve permissions, inputs, tool calls, counterparties, commercial influences, data flows, system versions, confirmations, failures and corrections. The two layers must refer to the same event. Do not give the consumer a friendly fiction while the engineering log tells a different story. The UK regulators are doing something useful by refusing to wait for an entirely new legal universe before looking at personal agents. Consumer rights, data duties, competition rules, payment controls and organizational responsibility do not evaporate because software performed the action. But saying the law follows the agent is the beginning of the job. The consumer still needs evidence at the moment something happens. What did it do? Why did it do it? Whose interest shaped the choice? What data moved? Who is responsible? How long do I have? How do I stop it? Give every consequential action an undo receipt. Then the personal agent can be useful without becoming a tiny uncontactable company living inside your phone.
01
WHAT ACTUALLY CHANGED
The CMA, FCA, ICO and Ofcom issued a joint statement on personal AI agents on October 30, 2026
The regulators say personal agents could make purchases, communicate with businesses and change how people use digital services and markets
They identify risks including fraud, scams, unexpected personal-data sharing and misleading recommendations, decisions or information
Firms are told to consider authority, data use, commercial influence, accountability and redress when agents act for consumers
Existing competition, consumer, data-protection, online-safety, financial-services, payments and cybersecurity frameworks continue to apply
The statement says an agent’s autonomy does not reduce the legal and regulatory responsibility of organizations that deploy it
The regulators are tracking products, engaging firms, sharing evidence, supporting sandboxes and looking for regulatory and compliance gaps
The CMA updated its consumer research and business guidance, including testing, monitoring, human oversight and rapid correction duties
02
WHY THIS MATTERS
Personal agents can turn a short instruction into purchases, payments, cancellations, account changes and personal-data transfers across several services
Consumers need to distinguish a recommendation, attempted action, pending transaction and completed outcome
Commercial incentives can shape rankings and recommendations even when an agent appears to be working only for the user
A clear authority record can show whether the consumer permitted comparison, negotiation, purchase, cancellation or ongoing access
A linked undo path can reduce harm when reversing one action requires coordinated changes across merchants, payments and data permissions
Organizations remain accountable even when an outside supplier designed the model or the agent acted with some autonomy
Accessible human redress is especially important for vulnerable consumers who may benefit from assistance but suffer more from confident mistakes
03
WHERE IT COULD HELP
- Issue a plain consumer receipt and a linked machine-readable audit record for every consequential agent action
- Record the user’s instruction, the agent’s interpretation, the authority used, limits, confirmations and revocation route
- Name the product, counterparty, amount, fees, status, contractual term and other services involved in the action
- Disclose search coverage, ranking rules, sponsorship, commissions, preferred partners and other commercial influence
- List personal-data categories accessed, inferred, shared and retained, plus recipients, purposes and correction or deletion routes
- Classify each action as reversible now, reversible until a deadline, requiring human review or not reversible with a stated reason
- Map dependent undo steps across the order, payment, delivery, account and data permissions, with visible failures and escalation
- Provide one emergency control to pause new actions, revoke authority, review recent activity and preserve an incident record
- Measure reversals, disputes, human-response times, recurring failures and outcomes by agent version and affected consumer group
KEEP A HAND ON THE WHEEL
Watch for enforcement cases, sector guidance and product testing that clarify how responsibility is divided among consumer-agent providers, merchants, payment firms and outside model suppliers. The practical test is whether a person can see authority, commercial influence and data movement, stop further action, use existing cancellation or dispute rights and reach a responsible human before harm compounds.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on October 30, 2026.
PUBLICATION RECEIPT: First edition. Verified against the four-regulator joint statement and the CMA’s updated consumer research and business guidance.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US