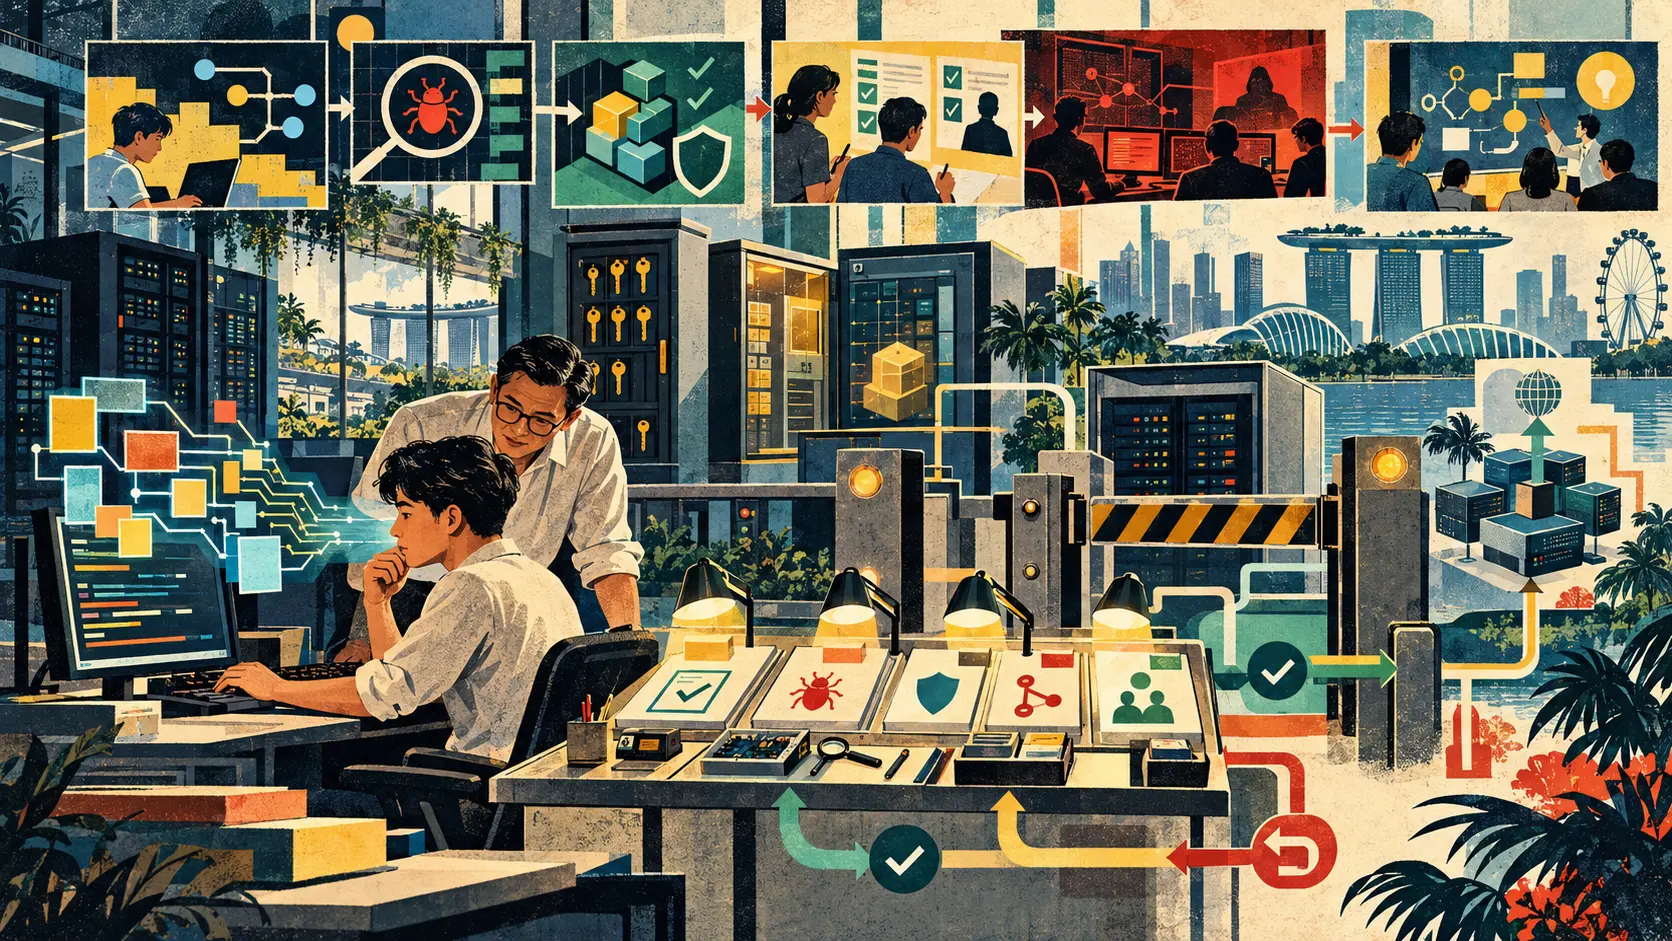
THE SIGNAL IN ONE SENTENCE
The most dangerous permission in an AI coding assistant may be the one nobody remembers granting. At first, the tool looks like a very fast colleague sitting beside the editor. It suggests a function, explains an error and drafts a test. Then it connects to the repository. It reads configuration files. It opens an issue. It runs a command. It sees a credential left in the development environment. The helpful colleague has quietly acquired keys to half the workshop. Singapore's Cyber Security Agency has put that problem into a public security conversation. On October 15, Senior Minister of State Tan Kiat How announced that CSA was releasing a Handbook on the Secure Use of AI Coding Assistants. He said the agency had studied the risks through security assessments and that the handbook translates its findings into practical guidance on how attacks could happen and which safeguards organizations can apply. The announcement did not publish evidence that the handbook has already prevented an incident. It did something more modest and immediately useful: it named the access surface. Tan said coding assistants may have deep access to source code, development environments, repositories and credentials. He also described a second risk that is easier to miss. If organizations automate every routine task, they may also automate away the work through which junior professionals learn to notice when something is wrong. His phrase for the work worth keeping was meaningful friction. That is the plain signal. Secure adoption needs two kinds of gates at once. One limits what the assistant can reach and do. The other makes a person explain, test and own the consequential decision. Remove pointless paperwork. Keep the moments that produce evidence and judgment. The distinction matters because friction has a deservedly poor reputation in software teams. Slow ticket queues, duplicate approvals and security reviews that arrive after release do not make a system safer. They make developers look for a side door. Meaningful friction is different. It appears where a mistake can cross a trust boundary. If an assistant is drafting a comment in an isolated file, the process can be light. If it is changing authentication code, reading production-like data, installing a package, calling an external service or using a credential, the process should become deliberate. The review should scale with consequence rather than with the number of lines changed. Start with access. Every coding assistant should have a written inventory of the repositories, files, tools, commands, networks, secrets and data it may reach. The default should be the smallest useful set. A tool that only needs to explain a compiler error should not inherit the developer's cloud credential. An assistant that drafts a patch should work in an isolated branch or workspace. Production access should not be available merely because a human operator happens to possess it. Credentials deserve their own boundary. Use short-lived, task-specific tokens. Keep secrets out of prompts, logs and generated artifacts. Prevent the assistant from reading broad environment files when it only needs one approved service. Record which identity performed each action, including the human who initiated it and the machine credential that executed it. That record is not surveillance theatre. It is the beginning of a recovery path. When generated code causes a problem, a team should be able to answer basic questions quickly. Which assistant and version produced the change? What context did it receive? Which tools did it call? What tests ran? Who reviewed the result? What was deployed, and how can it be reversed? Without that receipt, an AI-assisted change can become a small archaeological dig conducted during an outage. The next gate is evidence. A plausible patch is not a safe patch. Generated code should enter the same engineering system as human code, but teams should add tests aimed at the assistant's particular failure modes. Run unit and integration tests. Scan for exposed secrets and vulnerable dependencies. Check licences. Test authorization boundaries. Examine error handling, logging and data retention. Use static and dynamic analysis where it fits. For higher-risk changes, ask a human to state the threat model before approval. The important word is state. Clicking approve after skimming green checks is not judgment. A reviewer should be able to explain what the change does, which trust boundary it touches, how it could fail and what evidence supports release. If the reviewer cannot do that, the team has not finished the work, even if the assistant has. This is where the security handbook and Singapore's workforce argument meet. At an October 13 workforce panel, Tan said organizations should automate the task, not the learning. He distinguished administrative overhead from the experience, mistakes and guidance through which professionals develop judgment. Two days later, speaking about coding assistants, he returned to the same idea: preserve meaningful friction so younger professionals still build skills and learn from senior mentors. That is more than a training slogan. It suggests a design rule for AI-assisted development. Give junior engineers real responsibility inside a safe boundary. Ask them to predict what the assistant may miss before running the test suite. Have them explain a generated diff to a senior reviewer. Let them investigate a failed scan, design an abuse case and practice a rollback. Use red-team exercises with synthetic repositories and disposable credentials so mistakes become instruction rather than incidents. The mentor's job is not to retype the code. It is to make tacit judgment visible. Why did this permission feel too broad? Why is a dependency update riskier in this service than another? Why does a correct-looking authorization check fail when two systems disagree about identity? Those questions are the apprenticeship. A tool can accelerate the answer while still leaving the learner responsible for the reasoning. Teams also need a clear intervention ladder. At the lowest level, the assistant proposes text and cannot execute anything. Next, it may run approved tools in a sandbox. Higher levels might allow it to open a pull request or perform a limited build. Actions that touch secrets, external systems, releases, customer data or security controls should require explicit human approval and stronger logging. A stop control should revoke the tool's credentials and end active work, not merely hide the chat window. The ladder should be tested. Try to make the assistant read a forbidden file. Put a fake secret in a path it should not access. Feed it an instruction hidden inside repository content. Ask it to install an unapproved dependency or contact an unknown endpoint. Confirm that the control blocks the action, records the attempt and leaves the workspace recoverable. A policy that has never faced an adversarial prompt is a polite hope. Procurement should ask for the same evidence. Vendors can describe encryption, isolation and enterprise controls, but customers need exact answers about data retention, model training, subprocessors, regional processing, administrator access, incident notification and audit exports. Organizations should know whether they can disable individual capabilities and whether logs remain available after a contract ends. Smaller teams across Southeast Asia may not have a dedicated AI security group. A national handbook can help if it turns broad concerns into reusable control patterns: a minimum permission profile, a sample threat model, a test checklist, a logging schema, an incident playbook and examples for common development environments. Shared patterns can prevent every organization from rediscovering the same danger with fewer people and less time. But publication is not proof of adoption. The CSA address says the handbook is based on security assessments and provides practical guidance. The speech does not, by itself, show how many tools were assessed, which controls failed, whether the handbook is mandatory, how organizations will report incidents or whether smaller teams can implement the advice. Those details should be visible in the handbook, supporting material or later implementation records. The professional accreditation plan is also still a plan. CSA says Singapore will pilot a voluntary Cybersecurity Professional Accreditation Framework from the second quarter of 2027. It is intended to consider technical knowledge, practical experience and professional conduct, initially in selected organizations and specialties. That could reward demonstrated competence instead of certificate collecting. It could also become another credential unless assessment includes realistic exercises, evidence of judgment and continued practice. The useful test is whether the framework recognizes the work that safe AI adoption actually requires. Can a professional define least-privilege access for a coding assistant? Can they trace a generated change from prompt to deployment? Can they identify a poisoned instruction inside repository content? Can they stop an agent, rotate its credentials and restore a clean state? Can they explain the trade-off to an engineering manager without turning every release into a committee meeting? Those are consequential skills. They travel beyond Singapore. Software teams across the region share cloud platforms, open-source dependencies, outsourced development chains and cross-border services. A compromised assistant in one organization can expose credentials or introduce code that moves through suppliers and customers. A practical control pattern that works for a Singapore bank, hospital or public agency may help a smaller company in Malaysia, Indonesia, Thailand, Vietnam or the Philippines, provided local law, language, infrastructure and staffing differences are not papered over. Regional usefulness will depend on evidence rather than ceremony. Publish anonymized incident patterns. Show which safeguards stopped an attack and which produced false confidence. Offer machine-readable control mappings and small-team profiles. Run joint exercises. Record the time and expertise needed to implement each measure. Let practitioners report where the handbook collides with real development work. Then revise it. That feedback loop is another form of meaningful friction. It slows the easy story that a document solved the problem. It speeds the harder work of discovering whether the controls function when an assistant has a repository open, a token in memory and a deadline on the clock. The goal is not to make every generated semicolon wait at customs. It is to put the checkpoint where the blast radius begins. Let the assistant draft quickly. Limit its keys. Make the consequential change explain itself. Test the boundary. Keep the receipt. Practice the stop and rollback. Give the junior defender enough protected difficulty to become the senior mentor somebody else will need. That is friction worth keeping.
01
WHAT ACTUALLY CHANGED
Singapore announced a Handbook on the Secure Use of AI Coding Assistants on October 15, 2026
CSA says the handbook translates findings from its security assessments into guidance on attack paths and safeguards
The official address identifies source code, development environments, repositories and credentials as assets coding assistants may access deeply
Singapore connected secure AI adoption with professional judgment, mentorship and continued learning
The government used the phrase meaningful friction for experience-building work that should remain even as administrative overhead is automated
Singapore plans a voluntary Cybersecurity Professional Accreditation Framework pilot from the second quarter of 2027
The accreditation framework is intended to consider technical knowledge, practical experience and professional conduct
02
WHY THIS MATTERS
A coding assistant can move from suggestion tool to privileged actor when it gains repository, command, network or credential access
Least-privilege controls reduce the damage possible from a malicious instruction, unsafe tool call or mistaken generated change
Security checks create value only when they produce evidence, intervention and recovery paths
Automating routine tasks can remove the situations through which junior professionals learn to notice risk
Consequence-based review is more useful than applying the same bureaucracy to every generated edit
Common control patterns can help smaller Southeast Asian teams that lack dedicated AI security staff
Accreditation will be credible only if it tests practical judgment rather than adding another collectible certificate
03
WHERE IT COULD HELP
- Inventory every repository, file, tool, command, network, secret and data source available to the assistant
- Use isolated branches or workspaces and grant the smallest set of permissions needed for each task
- Issue short-lived task-specific credentials and keep secrets out of prompts, logs and generated artifacts
- Require explicit approval for changes involving authentication, authorization, secrets, external systems, releases or customer data
- Run unit, integration, secret, dependency, licence and authorization checks on generated changes
- Ask reviewers to explain the threat model, trust boundary, failure path and rollback before a consequential release
- Log the assistant version, context, tool calls, test evidence, reviewer and deployed artifact
- Test stop controls by revoking credentials, ending active work and restoring a clean workspace
- Use synthetic repositories and disposable credentials for adversarial exercises and junior staff training
- Measure whether controls prevent unsafe actions without driving developers into ungoverned tools
KEEP A HAND ON THE WHEEL
Watch for the full handbook and its control details, the number and types of assistants assessed, downloadable checklists, minimum permission profiles, guidance for smaller organizations, reporting of incidents and near misses, independent evaluation of recommended safeguards, updates after field use, accreditation criteria published from March 2027, realistic practical assessments in the second-quarter pilot, and evidence that junior staff retain hands-on security judgment as routine work is automated.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on October 16, 2026.
PUBLICATION RECEIPT: The article separates the verified handbook and accreditation announcements from analysis proposing permissions, review, testing, logging, training and recovery controls. It does not claim that the handbook has reduced incidents or that the voluntary accreditation pilot has begun.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US