THE SIGNAL IN ONE SENTENCE
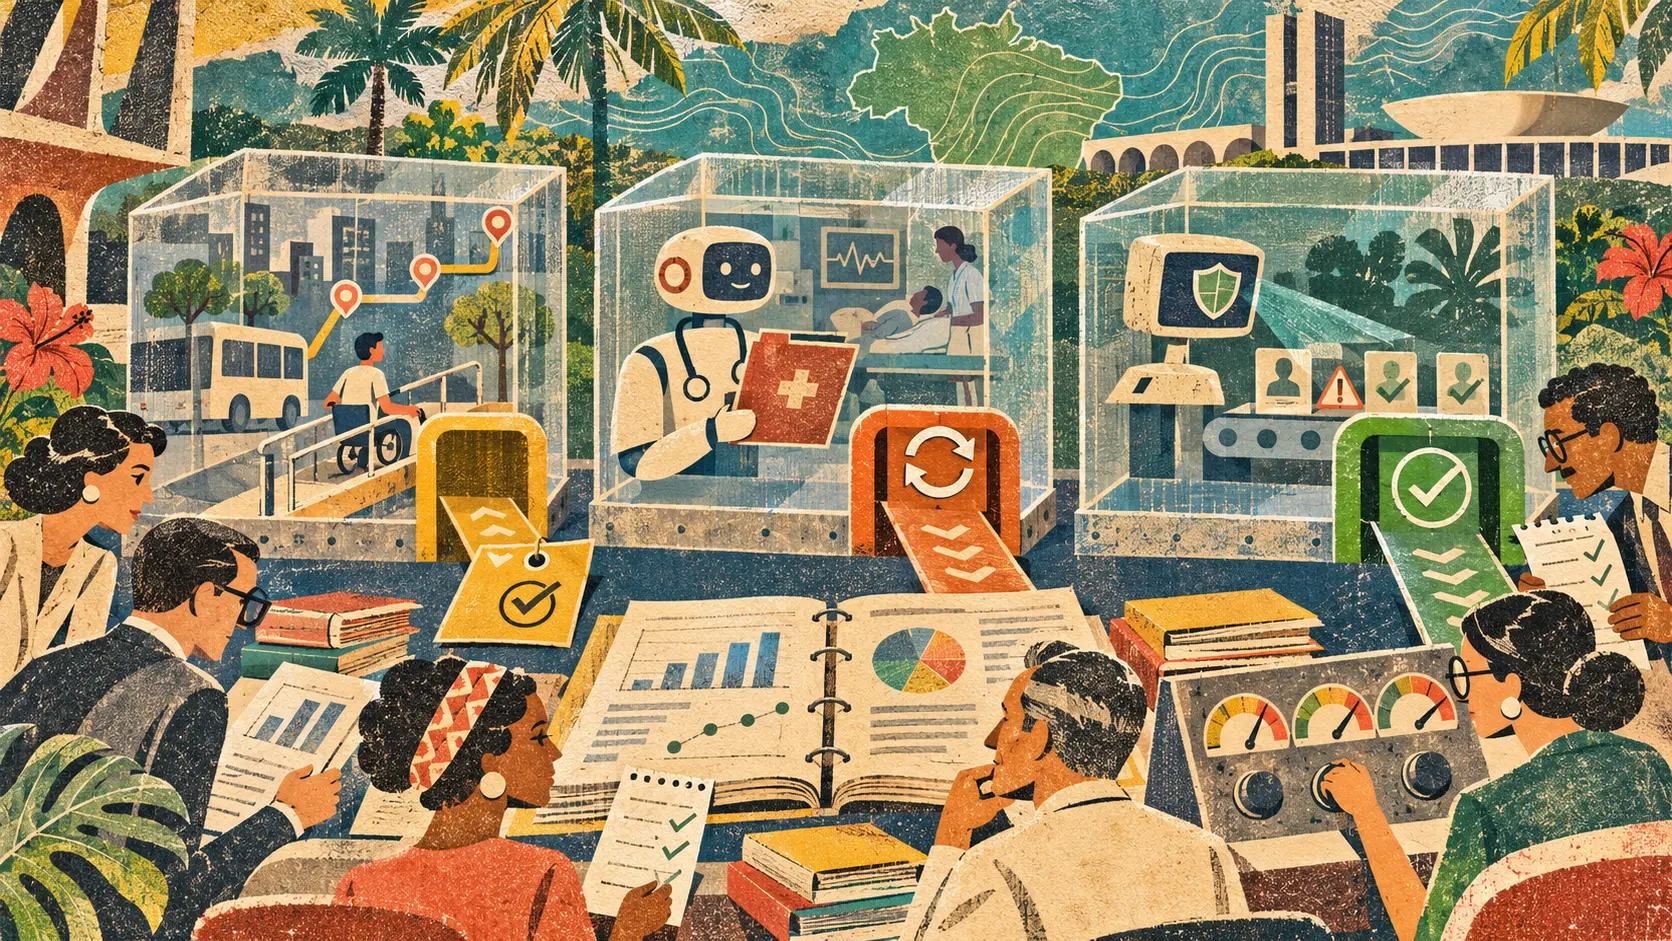
A regulatory sandbox should be a workshop with evidence on the floor, not a velvet rope leading to a launch party. Brazil's National Data Protection Authority has now shown what that looks like when the workshop reaches its exit. On November 3, the ANPD published the fourth, fifth and sixth monitoring reports from its pilot regulatory sandbox for artificial intelligence and data protection. The project was run with the University of São Paulo's Center for Artificial Intelligence and Machine Learning, known as CIAAM/USP. Three Brazilian companies brought three very different systems into six supervised cycles. Synapse AI brought Trajetto, a mobility platform that integrates real-time information to manage passenger flows and accessible routes. Prevvine brought STAiDOC, a clinical assistant built around language models adapted to the Brazilian medical context. Metatext brought GuardionAI, a gateway intended to detect and reduce risks in generative AI and autonomous-agent traffic. The regulator did not push all three through the same green door. Trajetto closed with partial success and remaining conditions. STAiDOC ended the experiment with useful learning and operational improvements, but still had corrections and retests to complete. GuardionAI received a satisfactory closing recommendation after the evaluators found that five conditions had been met, while continuing improvements were still expected. That is the signal. The same sandbox, methodology and regulator produced three different records because the evidence, risks and unfinished work were different. A supervised experiment did not become a participation trophy. The reports are careful about the boundary. In this sandbox, success means producing evidence and learning about progress, risk, limits, conditions and the requirements for safer development. It does not mean full approval, complete legal compliance or permission for unrestricted use. For Trajetto, the final report kept the assessment at sufficient with conditions. It recorded high aggregate inherent risk and medium aggregate residual risk. The sensitive material is not abstract. The system may handle changing location, mobility patterns and accessibility preferences. The report says closing the experimental cycle does not itself authorize regular operation. Among the remaining questions were what users actually see, whether explanations work in the interface, resistance to manipulated coordinates, protection against linking routes back to people, accessibility, third-party integrations and evidence that the discontinuation plan can really be executed. A plan to revoke credentials, deactivate infrastructure and delete telemetry is useful. A completed shutdown drill is better. STAiDOC carried a different risk shape. The system sits near clinical judgment and sensitive patient information. Across the sandbox, evaluators examined the quality of clinical and bibliographic answers, removal of identifiers, privacy filtering, transparency, responsibilities across institutions and providers, and the limits of automated recommendations. The closing report says the technical opinion remained favorable with conditions, but the aggregate inherent risk was critical and residual risk was medium. Corrections intended for the next version still needed to be deployed and retested. The report also notes that the joint classification of overall success was not completed. That is not a tiny administrative footnote. It means the public record should not turn a supervised clinical experiment into a broad claim of safety. GuardionAI had the cleanest exit, but even that result needs its boundaries attached. The report says Metatext met five technical conditions and received a favorable recommendation for satisfactory closure. The evaluators examined privacy protection in messages, sanitization, alerts for security teams, audit records, explanations and the division of responsibility between the customer controlling its own operations and Metatext operating the gateway. The final record still calls for continued work on performance and communication. A security layer can meet the conditions tested in a sandbox and still face new prompts, models, languages, agents and attack methods in ordinary operation. The point is not to pick a winner among three unrelated products. The point is to preserve the shape of each verdict. Most product announcements flatten evaluation into a badge. Passed. Certified. Approved. Ready. Real evidence is lumpy. One control was demonstrated. Another was described but not observed. A third worked on the tested version and needs to survive a live environment. A risk fell from high to medium, but a particular failure mode stayed high. A company completed the experiment, but the regulator did not authorize commercial use. That needs an exit receipt. Start with the exact system. Record the model, application, dataset, interface, infrastructure and policy versions that entered the test. If the company changes the model, privacy filter or mapping provider afterward, the receipt should not quietly travel with the new system. Name the affected people and data. Location and accessibility preferences create different harms from clinical records or security alerts. A general label such as personal data hides the decisions reviewers actually need to make. Separate every finding by evidence type. Mark what was demonstrated in a test, inspected in code or documentation, declared by the participant, planned for a future version or left unverified. One of the strongest habits in the ANPD reports is refusing to treat a documented safeguard as proof that the safeguard works. Keep the risk before and after controls. Aggregate labels are useful, but they can hide one severe item under several moderate ones. Publish the individual risks, the mitigation attached to each one, the test that checked it and the owner responsible for unfinished work. List every condition in plain language. Give it an identifier, evidence requirement, due date, reviewer and status. Completed should mean the required evidence was examined. Planned should stay planned. Retest required should not be translated into nearly done. Preserve disagreements. If a regulator records partial success and a company describes a stronger outcome, readers should see both positions and the evidence behind them. An empty joint conclusion is information, not a formatting problem to be cleaned up by communications staff. Attach the discontinuation plan. Show how credentials are revoked, keys handled, infrastructure disabled, telemetry removed, audit records retained and people notified. Then record the drill. A shutdown plan that has never shut anything down is still a hypothesis. Finally, state what the exit does not mean. It may close a research cycle without approving a product. It may validate a control without validating a business model. It may inform future regulation without creating a new rule. It may reduce a known risk without covering every live environment. The Brazilian pilot also offers a useful lesson for regulators outside Brazil. The ANPD says the work was experimental, preventive and designed for institutional learning, not direct enforcement. That can create room for companies to expose problems without treating every failed test as a violation. It can also create a perception problem if participation becomes marketing shorthand for regulatory blessing. The cure is not less experimentation. It is better public accounting. Publish the method. Publish the versions. Publish the conditions. Publish the failed and incomplete tests. Publish the difference between an exit, an authorization and a law. The regulator learns what evidence future rules should require. Companies learn which safeguards survive contact with tests. People affected by the systems get something more useful than a logo on a landing page. They get a receipt showing what was checked, what changed and what still needs work. That is what a sandbox should produce when the door opens.
01
WHAT ACTUALLY CHANGED
Brazil's ANPD published the fourth, fifth and sixth monitoring reports from its pilot AI and data-protection regulatory sandbox on November 3.
The pilot was conducted with CIAAM/USP and followed three systems across mobility, clinical assistance and AI security through six supervised cycles.
Trajetto closed with partial success, high inherent and medium residual aggregate risk, and conditions that still require evidence before possible regular operation.
STAiDOC ended the experiment with corrections, retests and regulatory work still pending, including fixes intended for a later version.
GuardionAI received a satisfactory closing recommendation after evaluators found five conditions had been met, while continued performance and communication improvements remained on the agenda.
ANPD says the sandbox is experimental, preventive and intended for institutional learning rather than direct enforcement.
02
WHY THIS MATTERS
A sandbox exit can close an experiment without proving complete legal compliance, unrestricted safety or permission for commercial operation.
Mobility, clinical and security systems affect different people and data, so a single pass label would erase the risk that matters in each setting.
Separating demonstrated controls from documented, declared and planned safeguards prevents paperwork from masquerading as operational proof.
Different outcomes from one methodology show that a credible sandbox can preserve uncertainty instead of rewarding every participant equally.
Public exit records can help future regulators define evidence requirements while giving affected people a clearer account of residual risk.
03
WHERE IT COULD HELP
- Create a versioned sandbox receipt naming the model, application, interface, data, infrastructure and policy that were actually tested.
- Map every affected group and data type, including location, accessibility preferences, clinical information, prompts, alerts and audit records.
- Label each safeguard as demonstrated, inspected, participant-declared, planned, unverified or failed.
- Publish individual inherent and residual risks beside aggregate scores so severe items cannot disappear inside an average.
- Track each condition with an identifier, evidence requirement, owner, due date, reviewer and exact status.
- Keep regulator, evaluator and participant conclusions separate when they disagree or when a joint conclusion is incomplete.
- Run the discontinuation plan as a drill and record credential revocation, key handling, infrastructure shutdown, data deletion and retained evidence.
- Require a new review when the model, provider, data flow, interface, clinical scope, mapping partner or security architecture changes materially.
- State explicitly whether an exit closes an experiment, authorizes operation, certifies a control or creates a binding rule.
- Continue post-sandbox monitoring for drift, new attack methods, incidents, accessibility failures and harms that controlled tests could not reproduce.
KEEP A HAND ON THE WHEEL
These findings come from ANPD and CIAAM/USP monitoring inside a supervised Brazilian pilot. They are not independent audits, blanket approvals or proof of performance in every live environment. The systems, versions, evidence and tests differed, so their outcomes are not a comparative leaderboard. Trajetto retained important conditions and elevated individual risks. STAiDOC still required corrections and retests, and its overall joint success classification remained incomplete. GuardionAI's satisfactory closure does not guarantee protection against future models, prompts or attacks. Watch for the final consolidated report, evidence that discontinuation plans were exercised, implementation of pending fixes, live-operation authorization where applicable, incident data and public records showing how sandbox lessons change future ANPD guidance or rules.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on November 4, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US