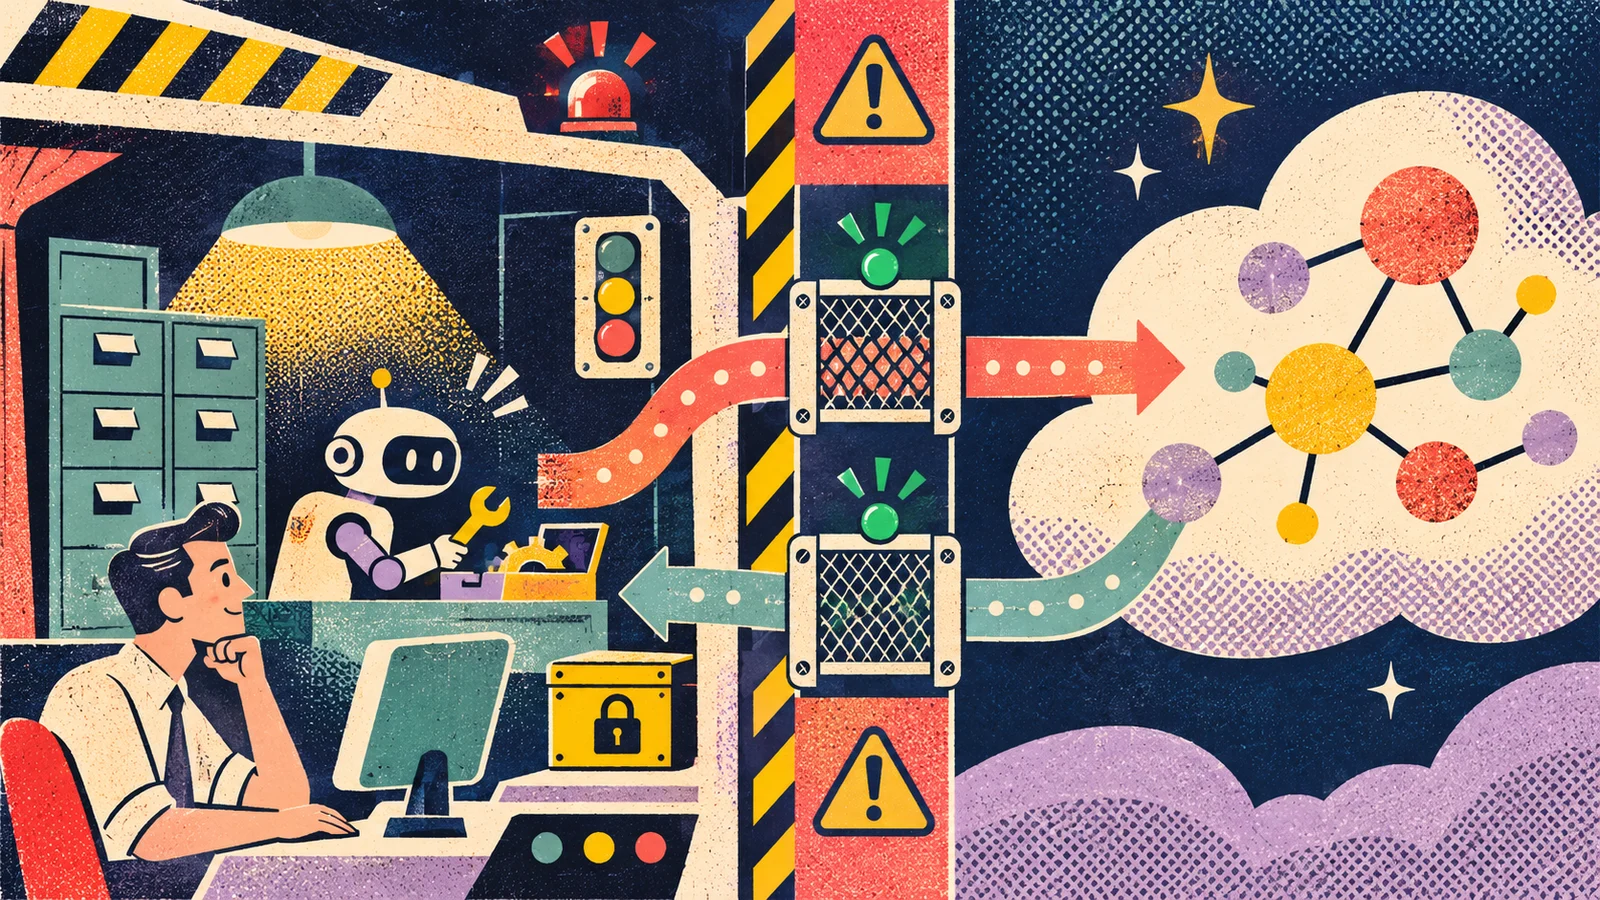
THE SIGNAL IN ONE SENTENCE
The phrase self-hosted can make an architecture sound more private than it is. Anthropic now documents a self-hosted environment for Claude Managed Agents. In this setup, the sandbox and tool execution run on customer infrastructure. The agent can use local files, run commands and call custom tools inside a worker the customer operates. Claude does not move into that worker. Anthropic says Claude still runs on its infrastructure and decides which tool calls to make. The customer worker executes those calls and sends the results back. Conversation history, tool results, skills and memory stores reach Anthropic. Files and processes inside the sandbox stay on the worker unless a tool returns them. That last clause carries most of the story. A file can remain on a local disk while its contents leave through a tool result. A secret can stay out of the model context until a shell command prints it. A database can remain inside a private network while an overhelpful query returns an entire customer table. The location of the container is not the security boundary. The boundary is every request, argument, result, credential, log entry and network connection that crosses between the model service, the worker and the systems around it. Draw that boundary before trusting it. Start with a plain architecture map. On the Anthropic side, list Claude, the Managed Agents control plane, conversation history, tool selection, memory and any service-side capabilities. Anthropic's documentation says web search and web fetch run on its side, even when the sandbox is self-hosted. On the customer side, list the worker, sandbox containers, mounted repositories, local files, command execution, internal APIs, credentials, logs and network policy. Between them, draw two large arrows. The first arrow carries the agent's requested tool action toward the worker. Record the tool name, parameters, session, user, policy decision and worker identity. The second arrow carries the result back. Record the result schema, fields, size, sensitivity, redactions, destination and retention rule. Do not label that arrow output and move on. It is the most likely place for local data to stop being local. Build a result contract for every tool. A search tool should return named fields, not an arbitrary dump of a document store. A file tool should return the requested passage, not the entire repository. A database tool should enforce row limits and approved columns. A shell tool should capture output carefully and suppress environment variables, tokens and unrelated file contents. Structured results are easier to inspect than a wall of terminal text. They also make it possible to reject unexpected fields before anything reaches the model. Use allowlists, size limits and sensitivity labels. Treat redaction as a backup rather than the main control. Once a secret appears in an unstructured result, a perfect cleanup step is wishful thinking wearing a safety vest. Then map credentials. Anthropic says customers operating self-hosted environments are responsible for hardening hosts, limiting the network, rotating the environment key, mounting repositories and isolating sessions. Give each tool its own identity and narrow permissions. A source-reading tool does not need production write access. A deployment tool does not need payroll records. A support tool does not need every tenant. Prefer short-lived credentials bound to a worker, session and action. Keep secrets outside mounted repositories. Prevent tools from listing the credential store. Log the identity used, but never log the secret itself. Now draw network egress. The worker should not have a blank check to contact the internet. Allow only the destinations required for the job. Deny unknown domains, raw IP destinations and unapproved protocols. Record DNS decisions and outbound connections in a place the agent cannot rewrite. Private services need the same treatment. A tool that can reach every internal host can turn one prompt-injection mistake into a network tour. Anthropic notes another boundary that is easy to miss: Managed Agents connects to agent MCP servers from Anthropic infrastructure, not from the self-hosted worker. A private MCP server may therefore need a tunnel or another route that exposes it to that service. Put the connection origin on the diagram. Do not assume private because the tool's business logic eventually touches a local system. Repository content is also untrusted input. A README, issue, test fixture or generated file can contain instructions aimed at the agent. The worker may have legitimate access to the repository, but the repository should not be allowed to expand the worker's permissions. Separate content from policy. Tool descriptions, allowed commands and credential scopes should come from protected configuration. A sentence inside a codebase should never be able to grant network access or convince the agent to reveal secrets. Next, isolate sessions. Use an ephemeral sandbox for each session or task. Do not let one user's files, command history, sockets or temporary credentials survive into the next user's environment. Destroy the container and revoke its credentials when the session ends. Test the cleanup. Create a harmless canary file in one session and verify that another session cannot find it. Repeat the test for environment variables, process lists, caches, mounted volumes and logs. Then test failure, not only success. Disconnect the worker during a tool call. Send a duplicate request. Rotate the environment key mid-session. Return malformed output. Attempt a result larger than the limit. Deny a required network destination. Crash a tool after it changes an external system but before it returns success. The system should know whether an action happened, whether it can be retried and who must resolve uncertainty. Without an idempotency key and an external action record, a retry can send the same payment, delete the same record or deploy the same change twice. Audit the boundary from both sides. The model-service record should identify the session, requested tool, parameters and received result. The worker record should identify the exact command, local identity, files touched, connections attempted, exit state and result sent back. Join those records with one correlation ID. Store them in an append-only destination outside the sandbox. Apply retention and access rules based on the data inside them, not the cheerful fact that they are called logs. Keep the human decision visible. For consequential actions, the agent can prepare a plan and a bounded tool call. A person with the right authority should approve the final action and see the target, scope, data leaving the boundary and rollback path. Approval should bind to the exact action. Approving read this repository is not approval to email its contents. Approving deploy commit A is not approval to deploy whatever happens to be on the branch later. The compliance boundary does not move merely because the worker does. Anthropic's current environment guide labels Managed Agents as beta and says its data handling is not eligible for zero data retention or HIPAA workloads. It also says self-hosting the sandbox does not change the retention and compliance coverage for conversation history and tool results sent to Anthropic. That may change as the product changes. Today, it means teams should not use a local container as a substitute for reading the service terms, retention rules and eligibility notes. The quickstart deserves the same caution. Anthropic provides a Docker Compose path for development and a Kubernetes deployment path for production operations. A compose file that starts successfully is not a security review. Production ownership still includes image hardening, patching, monitoring, capacity, isolation, key rotation, incident response and safe upgrades. Run a boundary test before production. Place canary secrets, files and records in locations the agent can and cannot access. Ask the agent directly and indirectly to retrieve them. Put malicious instructions in repository content. Try to smuggle data through filenames, tool errors, logs and oversized results. Verify that denied network traffic stays denied. Test legitimate work too. Security controls that break every useful task will be bypassed by lunchtime. Publish the result as a boundary receipt. For each tool, list its owner, execution location, input schema, output schema, credentials, reachable systems, network destinations, logs, retention, session isolation, failure behavior and required human approval. Mark what remains on customer infrastructure. Mark what reaches Anthropic. Mark what reaches third parties. Mark what nobody has tested. Self-hosted tool execution can be genuinely useful. It can keep local processes close to private systems, allow custom hardening and give operators control over the worker environment. It does not make the agent local by magic. The trustworthy version is not the one with the most private-sounding label. It is the one whose data movement, permissions and owners can fit on a diagram that engineers, security teams and ordinary humans can challenge. Draw the box. Draw the arrows. Test every crossing. Then decide whether the boundary deserves trust.
01
WHAT ACTUALLY CHANGED
Anthropic documents a self-hosted environment for Claude Managed Agents in which the sandbox and tool execution run on customer infrastructure.
Claude remains on Anthropic infrastructure and chooses the tool calls that the customer worker executes.
Conversation history, tool results, skills and memory stores reach Anthropic, while sandbox files and processes remain on the worker unless a tool returns them.
Customers operate the hosts, hardening, network limits, environment keys, repository mounts and sandbox lifecycle.
Web search and web fetch continue to run on Anthropic infrastructure.
Anthropic connects to agent MCP servers from its infrastructure, so private MCP services may require a tunnel or another reachable route.
The documentation provides a Docker Compose development path and a Kubernetes production path.
The current guide labels Managed Agents as beta and says the product is not eligible for zero data retention or HIPAA workloads.
02
WHY THIS MATTERS
Self-hosted tool execution is not the same as self-hosting Claude or the Managed Agents service.
A local file can still leave the network when a tool returns its contents to the model.
Unstructured tool output can expose secrets, personal data and far more information than the task required.
Customers own substantial security and operational responsibility for the worker environment.
MCP, web tools and network routes may cross different boundaries than teams expect.
Compliance and retention coverage does not automatically change because the sandbox runs locally.
A written boundary map makes permissions, data movement and accountable owners reviewable before deployment.
03
WHERE IT COULD HELP
- Map Claude, the control plane, worker, sandbox, tools, data stores and network connections.
- Record tool names, parameters, policy decisions, worker identities and correlation IDs.
- Define strict schemas, field allowlists, size limits and sensitivity labels for tool results.
- Return narrow passages and rows instead of entire files, repositories or database tables.
- Give each tool a short-lived identity with the least permissions required.
- Keep secrets outside repositories and prevent tools from listing credential stores.
- Allowlist outbound destinations and log network decisions outside the sandbox.
- Label the origin and route of every MCP connection.
- Treat repository text, tool output and remote content as untrusted instructions.
- Use ephemeral, isolated sandboxes and revoke credentials when sessions end.
- Test cross-session canaries, secret access, network denial and oversized results.
- Use idempotency keys and external action records for tools with side effects.
- Join model-side and worker-side audit records with one correlation ID.
- Bind human approval to the exact target, action, data and version.
- Publish ownership, retention, failure behavior and untested crossings for every tool.
KEEP A HAND ON THE WHEEL
Managed Agents and its self-hosted environment are documented as beta and can change. Self-hosted refers to the sandbox and tool execution. Claude still runs on Anthropic infrastructure and selects tool calls. Conversation history, tool results, skills and memory stores reach Anthropic. Files and processes remain local only until a tool returns their contents or effects. Anthropic's current guide says Managed Agents is not eligible for zero data retention or HIPAA workloads. Self-hosting the worker does not change that coverage. Web search and web fetch run on Anthropic infrastructure. Agent MCP connections also originate from Anthropic rather than the customer worker. The Docker Compose quickstart is for development. Production operators remain responsible for hardening, patching, monitoring, key rotation, network limits, session isolation and incident response. The current documentation does not provide a dated public launch announcement. Verified November 13, 2026.
04
TERMS WORTH KEEPING
OPEN GLOSSARY CARD
Zero data retention
A service configuration in which covered request and response content is not retained by the provider after processing, subject to the exact product terms and exceptions.
OPEN GLOSSARY CARD
Sandbox
A restricted space where software can act without reaching everything around it.
OPEN GLOSSARY CARD
Zero data retention
A service arrangement designed not to keep customer inputs or outputs after processing.
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on November 13, 2026.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US