THE SIGNAL IN ONE SENTENCE
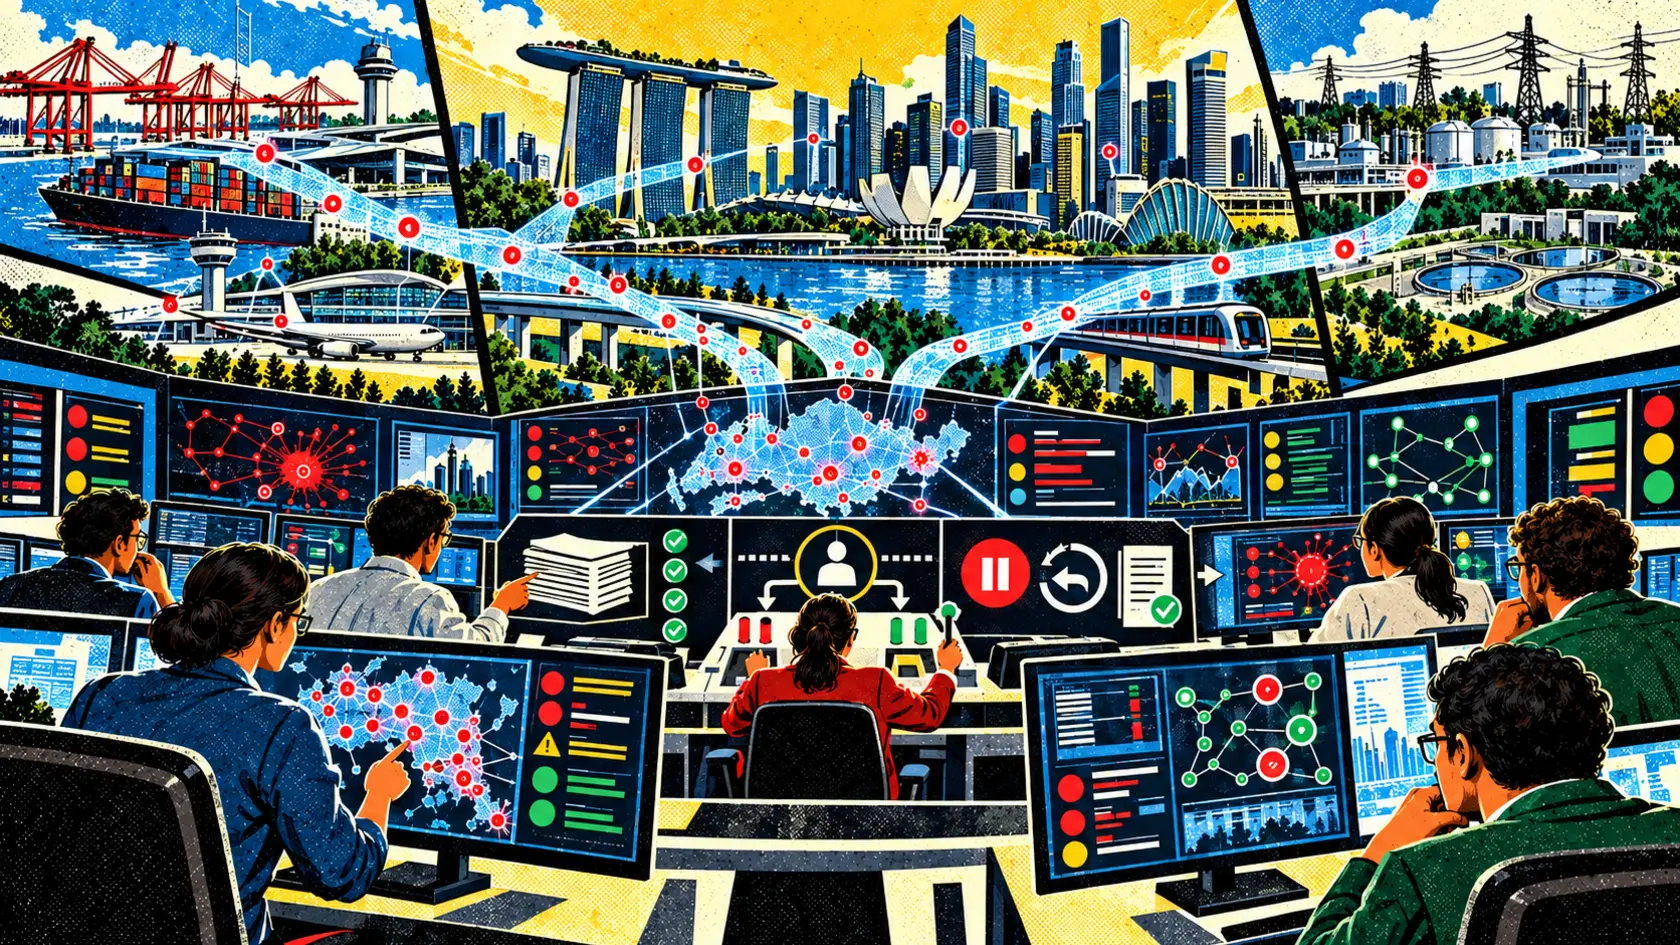
A wall of threat maps is not a chain of command. Singapore launched its Cybersecurity Strategy 2026 on October 13 and described a new National Cyber Command Centre, known as NC3, as the Cyber Security Agency's operations hub for national cyber defence. The centre is meant to assemble a common picture of vulnerabilities and threats. It will combine information from government agencies, owners of critical information infrastructure, cybersecurity companies and international partners. Officials say it will support continuous monitoring, earlier detection of advanced threats and coordination during major national incidents. Artificial intelligence is woven through the plan. Singapore says it will progressively deploy AI across NC3 and the Government Cyber Security Operations Centre. Existing tools automate the discovery and mapping of exposed assets and vulnerabilities. Government teams also use AI agents to assist with vulnerability discovery and testing. The strategy includes protective DNS, which can block connections to known malicious domains before they reach users, and investment in AI harness engineering so agencies can integrate different models, tools, data and workflows securely. The ambition is easy to understand. Attacks move quickly. Defenders need to find weak points earlier, connect clues across organizations and act before a compromise spreads. The plain signal is that a common operational picture is not common authority. When a dashboard says a hospital, bank, transport operator or government network may be under attack, someone still has to decide what happens next. Who may see the underlying evidence? Who may ask for more data? Who may isolate a machine, block a domain, revoke credentials, interrupt a public service or tell a private operator to disconnect part of its network? Who can stop an automated response when it begins to cause harm? Those decisions should not be inferred from who happens to be standing nearest the screen. NC3 needs an authority ledger. For every class of action, the ledger should identify the evidence required, the agency or person allowed to approve it, the systems affected, the operator who must be notified, the conditions for human override, the rollback path and the record that remains afterward. Start by separating six levels of activity. The first is observation. Systems collect logs, vulnerability data, network signals and reports. This stage needs clear purpose limits, access controls and retention rules because a national view can expose sensitive information about public agencies and private operators. The second is enrichment. Analysts and automated tools connect signals, compare them with threat intelligence and estimate confidence. The original evidence must remain available. A model's neat summary cannot become the only surviving version of an uncertain event. The third is recommendation. A system may suggest blocking a domain, rotating credentials or isolating a host. The recommendation should name the supporting evidence, confidence, expected benefit, possible collateral damage and alternatives. The fourth is low-risk containment. Some reversible actions can be pre-authorized within narrow boundaries. A suspicious connection might be rate limited. A known malicious domain might be blocked for a short period. A compromised account might be forced through another authentication step. Each action needs an expiry time and a tested undo button. The fifth is high-impact intervention. Disconnecting a hospital system, shutting down an industrial network or blocking a widely used service can create risks of its own. Those actions should require named human authorization and, where time permits, confirmation from the affected operator. The sixth is emergency action. A genuinely fast-moving national incident may justify extraordinary powers. The ledger should still specify who invokes them, how long they last, who is informed and when an independent review begins. Speed does not remove governance. It makes governance time-sensitive. AI can compress the period between detection and response. It can also compress the period between a mistake and widespread damage. A model may connect unrelated events, assign too much confidence to weak intelligence or recommend a familiar response for an unfamiliar system. A compromised data source can poison the common picture. An attacker can generate noise to exhaust analysts or trick an automated control into blocking legitimate traffic. That is why NC3 should measure the quality of decisions, not merely the speed of them. Publish false-positive and false-negative rates for bounded tasks. Measure the time from signal to human review, from confirmed incident to containment and from containment to restored service. Record collateral impact, reversals, analyst workload and cases in which an operator rejected the system's recommendation. The rejected recommendations may be especially useful. They show where local knowledge beat the central picture. Private-sector participation makes that local knowledge essential. Singapore's critical services are not all operated from government offices. Telecommunications, finance, energy, transport, health and cloud services cross organizational boundaries. A central command centre can connect evidence that no single operator holds. It can also become a powerful collector of commercial and operational data. The authority ledger should therefore include a data ledger. For each source, state what data is shared, why it is needed, who can access it, how long it is kept, whether it may train or evaluate an AI system and how an operator can correct a mistaken interpretation. Log every access. Separate information needed for immediate defence from information useful for later research. Do not let an incident become a permanent permission slip. The strategy's emphasis on proprietary threat detection and privileged intelligence creates another accountability question. Some secrecy is unavoidable in cyber defence. Publishing live detection methods can help attackers. But secrecy about techniques does not require secrecy about performance and authority. Singapore can publish aggregate measures, independent test methods, model and tool version records, red-team results and post-incident findings without revealing exploitable details. It can say how often an alert led to action, how often action was reversed and whether the affected service recovered faster. Protective DNS needs the same discipline. Blocking a known malicious domain upstream can prevent many users from reaching phishing or malware infrastructure. It can also block a legitimate service when a domain is misclassified or reused. Publish the source of block decisions, expiry rules, false-block rate, appeal path and average repair time. Emergency blocking without an equally fast correction channel is unfinished infrastructure. The government's investment in AI harness engineering is a sensible technical choice. A harness sits between models and operational systems. It manages tools, data, permissions, workflows and monitoring. Building that layer can let Singapore choose among models instead of wiring national defence to one vendor. It can also keep sensitive data inside controlled environments and impose consistent approval rules. The harness is where the authority ledger can become executable. Permissions should be attached to actions, not to vague labels such as agent or analyst. A model may read one data set but not export it. It may draft a containment plan but not execute it. It may block a domain for fifteen minutes but not indefinitely. A human approver may authorize one action within one incident, not grant a permanent role expansion. Every tool call should leave a record. Every automated action should have a reason, scope, expiry and rollback instruction. The minister also said he had met major AI companies, including OpenAI, Anthropic, Google and Amazon, and asked for early notification, high-quality information and full transparency when incidents occur. The companies expressed willingness to cooperate, but the work remains in progress. Turn that expectation into a protocol. Define what triggers a notification, who receives it, how quickly it must arrive, what evidence format is required, which affected systems must be named and when customers or the public are told. A friendly promise made during a meeting is not the same thing as an incident interface that works at 3 a.m. Regional coordination also remains unfinished. Singapore says ASEAN members are discussing coordinated responses involving AI agents. Any regional mechanism will need interoperable incident reports, shared severity definitions, contact points, limits on cross-border data and a clear map of who remains responsible when an automated response crosses a network boundary. Singapore is right that defenders cannot wait until every institution sees an attack independently. NC3 could shorten the distance between a weak signal and a coordinated response. It could give small operators access to intelligence they could not produce alone. It could help the country learn from one incident instead of repeating it across many systems. But a common picture concentrates attention, data and power. The public should be able to see the rules around that concentration before a major incident tests them. Publish the authority ledger. Test it through exercises with agencies and private operators. Include mistaken alerts, conflicting evidence, unavailable decision makers and a containment action that must be reversed. Record who noticed the problem and how quickly the system recovered. The command centre may make Singapore's cyber defence faster. Its legitimacy will depend on whether everyone knows who owns the next move.
01
WHAT ACTUALLY CHANGED
Singapore launched its Cybersecurity Strategy 2026 on October 13
The National Cyber Command Centre has been established as the Cyber Security Agency operations hub for national cyber defence
NC3 is intended to provide a national picture of vulnerabilities and threats
The centre will combine information from government, critical-infrastructure owners, security companies and international partners
Officials say NC3 will support continuous monitoring and earlier detection of advanced persistent threats
The centre will support major national responses using AI-enabled coordination systems
Singapore plans to deploy AI progressively across NC3 and the Government Cyber Security Operations Centre
Existing government tools automate mapping of exposed assets and assist vulnerability testing
The strategy includes protective DNS to block known malicious domains upstream
Singapore plans to invest in AI harness engineering for secure model, tool, data and workflow integration
The government is asking major AI companies for earlier notification and better incident information
Coordinated ASEAN responses involving AI agents remain work in progress
02
WHY THIS MATTERS
A shared national picture can connect threat evidence that no single operator holds
Earlier detection can reduce the time attackers have to move across critical systems
Central coordination concentrates sensitive public and private operational data
AI can accelerate useful containment and mistaken intervention alike
A recommendation is different from legal or operational authority to act
High-impact responses can interrupt hospitals, finance, transport or utilities
Private operators need clear rights, duties and correction paths when they share data
Proprietary detection can protect methods while still allowing aggregate public evaluation
Model-independent harnesses can reduce vendor dependence if permissions remain explicit
Regional coordination needs interoperable reports and named responsibility across borders
03
WHERE IT COULD HELP
- Publish an authority ledger for observation, recommendation, containment and disruption
- Name the evidence, approver, affected systems, expiry and rollback for each action class
- Preserve original evidence alongside model summaries and confidence estimates
- Use narrow, reversible and time-limited permissions for automated containment
- Require named human approval for high-impact interventions
- Create a data ledger for purpose, access, retention, training use and correction
- Log every access, tool call, decision, override and rollback
- Measure false positives, false negatives, decision latency and service restoration
- Track collateral impact, reversed actions and rejected recommendations
- Publish protective-DNS block sources, expiry rules and appeal performance
- Red-team the coordination system with conflicting evidence and poisoned data
- Turn vendor cooperation promises into a timed incident-notification protocol
KEEP A HAND ON THE WHEEL
The National Cyber Command Centre and its intended functions are described by the Singapore government. The reviewed official material does not publish a budget, implementation timetable, legal authority map, automation thresholds, technical architecture, independent evaluation or measured defensive outcomes. Company cooperation on early incident notification and ASEAN coordination are described as ongoing work. Watch for operational rules, data-sharing agreements, public performance measures and post-incident review requirements.
04
TERMS WORTH KEEPING
SOURCES AND VERIFICATION STATUS
This article was written from the materials below. Product claims and dates were checked against those sources on October 13, 2026.
PUBLICATION RECEIPT: The article attributes the centre and strategy to Singapore government sources, separates announced functions from proposed controls and does not treat planned coordination as measured operational performance.
THE PUBLICATION ENGINE
WANT A SIGNAL OF YOUR OWN?
We build source-grounded publications, private briefings, and editorial systems for organizations with something useful to say.
WORK WITH US